

Australian Daily Threat Briefing: Exploitation Windows Collapse Amid AI-Driven Attacks
As a senior penetration tester actively analysing adversary behaviour and responding to frontline incidents, I am tracking a highly volatile cyber threat landscape across Australia. Over the past 24 hours, the window between vulnerability disclosure and active exploitation has collapsed to mere days—and in some cases, hours. Adversaries are aggressively weaponising artificial intelligence, exploiting cloud misconfigurations, and capitalising on critical zero-day vulnerabilities in web applications and APIs.
As a senior penetration tester actively analysing adversary behaviour and responding to frontline incidents, I am tracking a highly volatile cyber threat landscape across Australia. Over the past 24 hours, the window between vulnerability disclosure and active exploitation has collapsed to mere days—and in some cases, hours. Adversaries are aggressively weaponising artificial intelligence, exploiting cloud misconfigurations, and capitalising on critical zero-day vulnerabilities in web applications and APIs.
Here is your daily threat briefing detailing the active exploits, prominent threat actors, and critical vulnerabilities impacting Australian organisations across key sectors.
Sector Threat Analysis
Healthcare The Australian healthcare sector remains under intense siege from double-extortion ransomware. Threat actors like DragonForce and the INC Ransom group are actively targeting healthcare software vendors and third-party systems to disrupt patient services and extract medical records. Affiliates operating Ransomware-as-a-Service (RaaS) models are using legitimate administrative tools to blend into normal network traffic, bypassing basic defences. The focus has shifted from merely locking databases to exfiltrating highly sensitive patient records via vulnerable web applications and poorly secured APIs.
FinTech & eCommerce Financially motivated cyber attacks are taking longer to detect, and cyber extortion has now officially eclipsed Business Email Compromise (BEC) as the leading threat type in our region. FinTech and eCommerce platforms are seeing adversaries bypass traditional perimeter security by targeting financial APIs and cloud payment gateways. Threat groups are aggressively scraping cloud environments for authentication tokens, meaning organisations must urgently secure their cloud infrastructure to defend against sophisticated extortion and comply with Australian regulatory reporting requirements.
SaaS Providers & Government Supply chain and cloud vulnerabilities have taken centre stage. The Australian Signals Directorate’s ACSC recently issued a "High Alert" regarding the ongoing malicious targeting of online code repositories. Threat actors are turning trusted code repositories into malicious delivery systems to harvest credentials, deploy malware, and execute supply-chain compromises affecting both SaaS providers and federal government departments. We are also continuing to observe the exploitation of unpatched web applications to breach major cloud environments, exposing highly sensitive data.
Education / EdTech Higher education institutions and EdTech platforms remain highly exposed due to their expansive attack surfaces. Threat actors are actively leveraging critical pre-authentication Remote Code Execution (RCE) vulnerabilities in remote support software to hijack university networks. Attackers are exploiting weak access controls in student portals and third-party SaaS integrations, capitalising on the high volume of users to hide lateral movement.
IoT (Internet of Things) With the new Cyber Security (Security Standards for Smart Devices) Rules officially coming into effect last month (March 2026), the baseline for IoT security has shifted, making generic default passwords illegal. However, legacy devices remain a critical vulnerability. Sophisticated threat actors are exploiting flaws in distributed IoT networks and edge-facing infrastructure to gain administrative privileges and establish persistent access, which serves as a launchpad to attack converged IT and OT environments.
Technology Highlights: Web Apps, APIs, Cloud, and AI Systems
- AI Systems: The attack surface has expanded rapidly into Artificial Intelligence. Just yesterday (9 April), the ACSC urged organisations to adapt as advanced AI models are drastically speeding up the discovery of software vulnerabilities, significantly lowering the barrier to entry for cybercriminals. Furthermore, we are seeing the real-world impact of AI-specific vulnerabilities, such as flaws in AI-integrated browser extensions that allow attackers to tap into the browser environment and access local operating system files. Additionally, "data spills" caused by employees uploading sensitive commercial data into public-facing generative AI tools are creating a severe internal risk that requires immediate governance.
- Web Applications & Cloud APIs: Attackers are moving away from traditional malware deployments, favouring identity-based attacks on APIs and cloud infrastructure. Misconfigured cloud buckets, over-privileged API keys, and unpatched web applications remain the most consistent initial access vectors I exploit during adversary simulations.
Conclusion
The speed at which threat actors are weaponising newly disclosed vulnerabilities demands a proactive and offensive security posture. Australian organisations can no longer rely on reactive monitoring. Regular testing of web applications, cloud configurations, and API endpoints is critical to identifying gaps before they are exploited.
Contact us for a quote for penetration testing service or adversary simulation.

Australian Cyber Threat Briefing: Exploited Repositories, AI Risks, and Zero-Day Ransomware
As a senior penetration tester monitoring the evolving tactics of threat actors, it is clear that the attack surface for Australian organisations is expanding at an unprecedented rate. Over the last 24 hours up to 09 April 2026, the Australian threat landscape has seen aggressive moves by ransomware operators, the active exploitation of artificial intelligence workflows, and critical high-priority alerts from the Australian Cyber Security Centre (ACSC).
As a senior penetration tester monitoring the evolving tactics of threat actors, it is clear that the attack surface for Australian organisations is expanding at an unprecedented rate. Over the last 24 hours up to 09 April 2026, the Australian threat landscape has seen aggressive moves by ransomware operators, the active exploitation of artificial intelligence workflows, and critical high-priority alerts from the Australian Cyber Security Centre (ACSC).
Here is our daily deep dive into the most pressing threats affecting Australian organisations across key sectors, including actionable intelligence on exploited web applications, APIs, cloud environments, and AI systems.
1. SaaS Providers, eCommerce, and FinTech: Supply Chain and API Threats
The Threat: The ACSC has re-issued a "High Alert" to Australian leaders regarding the active targeting of online developer code repositories. Threat actors are compromising authentication tokens and abusing valid tooling to scan for cryptographic secrets, alter public packages, and covertly migrate private repositories to public access. This poses a massive supply-chain risk for SaaS platforms and FinTechs processing critical eCommerce transactions. Exploited Vulnerabilities:
- ActiveMQ Jolokia API (CVE-2026-34197): We are tracking an unauthenticated Remote Code Execution (RCE) vulnerability in Apache ActiveMQ, a middleware widely used in FinTech and eCommerce for message brokering. Attackers are abusing the Jolokia REST API to fetch remote configurations and run arbitrary OS commands.
- Cloud Privilege Escalation: A recently addressed flaw in the Google Cloud Vertex AI Agent Engine allowed attackers to extract service agent credentials, enabling them to pivot across customer cloud projects and access sensitive storage and Artifact Registries.
2. Healthcare and Legal Services: High-Tempo Ransomware Operators
The Threat: The healthcare sector, alongside third-party service providers like legal firms handling highly sensitive data, remains in the crosshairs of rapid-deployment ransomware groups. Threat actor Storm-1175 has accelerated its operations, aggressively targeting internet-facing assets in Australia, the UK, and the US to deploy Medusa ransomware. Exploited Vulnerabilities: Storm-1175 operates high-velocity campaigns using a slew of zero-day vulnerabilities, including recent flaws in SmarterMail (CVE-2026-23760) and GoAnywhere MFT (CVE-2025-10035). Their time from initial access to ransomware deployment has shrunk to under 24 hours, highlighting the urgent need for robust external attack surface management.
3. Government and IoT: Regulatory Enforcement and Targeted Campaigns
The Threat: As of last month, Australia’s new mandatory smart device security rules are actively enforced under the Cyber Security Act 2024. This means IoT manufacturers are now legally accountable for baseline security, including banning default passwords and mandating vulnerability disclosure. Meanwhile, government networks continue to face highly sophisticated, targeted espionage. Exploited Vulnerabilities: The "TrueChaos" campaign has been observed exploiting a zero-day vulnerability (CVE-2026-3502) in on-premises communication update processes to push Havoc payloads into government networks across the Asia-Pacific region.
4. Education & EdTech: The Skills Gap and Sector Vulnerabilities
The Threat: The education sector continues to be heavily targeted by ransomware syndicates like Qilin, who only yesterday claimed a breach of Australian tech firm Seeing Machines. EdTech platforms must remain incredibly vigilant, particularly regarding student data privacy. However, there is positive news: the Cyber Battle Australia 2026 programme officially kicks off this month. This nationwide initiative aims to combat severe skills shortages by bringing practical, mission-based learning—covering web vulnerabilities, Linux fundamentals, and cryptography—to students across the country.
5. AI Systems: Weaponised Prompt Injection and Malicious Workflows
The Threat: Artificial Intelligence is no longer just a defensive tool; it is a direct attack vector. The ACSC has just released guidance on the cyber security impacts of Frontier AI models, warning organisations to aggressively review their security baselines. Exploited Vulnerabilities:
- Flowise AI (CVE-2025-59528): Over the past 48 hours, we have seen the first in-the-wild exploitation of this critical flaw in Flowise (a UI for LangChain). Attackers are injecting arbitrary JavaScript code, compromising thousands of exposed AI workflows globally.
- AI Code Editors ("NomShub"): We are tracking novel prompt injection vulnerabilities in autonomous developer tools where attackers use malicious repositories to execute shell commands within the developer's environment—effectively turning a prompt injection attack into an RCE.
Penetration Tester’s Recommendations
The attack surface is expanding rapidly across APIs, cloud architectures, and AI pipelines. Traditional vulnerability scanning is no longer sufficient to stop identity-based cloud pivoting or AI prompt injections. Australian organisations must adopt a proactive, "assume breach" mentality, enforce strict credential hygiene in code repositories, and continuously test internet-facing infrastructure against real-world adversary behaviour.
Contact us for a quote for penetration testing service or adversary simulation.

Daily Cyber Threat Briefing: High-Velocity Ransomware and Cloud Supply Chain Risks in Australia
As the Australian digital landscape continues to expand, so does the sophistication and speed of modern threat actors. Over the last 24 hours, security teams across the country have faced an elevated operational tempo of cyber activity, ranging from browser-based zero-day exploitation to high-velocity ransomware deployments. In this daily briefing, we analyse the latest threat intelligence, prominent adversaries, and critical vulnerabilities impacting key Australian sectors.
07 April 2026
As the Australian digital landscape continues to expand, so does the sophistication and speed of modern threat actors. Over the last 24 hours, security teams across the country have faced an elevated operational tempo of cyber activity, ranging from browser-based zero-day exploitation to high-velocity ransomware deployments. In this daily briefing, we analyse the latest threat intelligence, prominent adversaries, and critical vulnerabilities impacting key Australian sectors.
Sector Threat Landscape
Healthcare The healthcare sector remains under immense pressure from both hacktivists and financially motivated syndicates. Following a recent cyber incident involving medical device manufacturer Stryker, the Iranian-linked hacktivist group Handala claims to have wiped and exfiltrated terabytes of sensitive data. Simultaneously, the Aeromedical Society of Australasia (ASA) is currently navigating a ransomware incident tied to the LockBit 5.0 group. Furthermore, the China-linked actor Storm-1175 has been aggressively targeting Australian healthcare organisations with Medusa ransomware, successfully moving from initial breach to encryption in under 24 hours.
FinTech Financial technology platforms are facing intense scrutiny regarding data protection. The Australian FinTech platform youX recently confirmed a massive cloud breach. Attackers gained unauthorised access to a MongoDB Atlas cluster, exposing 141 gigabytes of data and potentially compromising over 600,000 loan applications. This incident highlights the severe operational impact of cloud database misconfigurations and insecure integrations.
SaaS Providers & Government Supply chain attacks targeting Software-as-a-Service (SaaS) providers continue to present systemic risks to government entities. A major cloud breach at LexisNexis has exposed sensitive data affecting several Australian law firms, courts, and federal agencies. In response to these cascading disruptions across critical networks, the Australian Government is actively consulting industry on reforms to the Security of Critical Infrastructure (SOCI) framework to strengthen governmental intervention powers during catastrophic cyber incidents.
Education / EdTech Educational institutions are increasingly targeted for their vast repositories of personal identifying information (PII). The Victorian Department of Education recently suffered a breach where student names, school emails, and encrypted passwords were accessed by an unauthorised party. Furthermore, the Australian education sector has been heavily featured on Storm-1175's target list as they scan for vulnerable perimeter assets.
eCommerce & IoT For eCommerce and retail platforms, the primary threat vector is shifting towards browser-based SaaS attacks and identity abuse, effectively bypassing traditional endpoint security. In the Internet of Things (IoT) and Operational Technology (OT) spaces, authorities are warning of severe vulnerabilities in edge devices. Threat actors are actively exploiting unpatched internet-facing routers and VPN concentrators to infiltrate corporate networks, with the ACSC noting that edge compromises boast an alarming success rate.
Vulnerability Spotlight: Web Apps, APIs, Cloud, and AI Systems
Adversaries are exploiting a range of emerging vulnerabilities across the technology stack:
- Web Applications & APIs: Threat actors are weaponising zero-day vulnerabilities at an unprecedented rate. Google recently issued an emergency patch for a high-severity Chrome zero-day (CVE-2026-5281) that is actively being exploited in the wild. Additionally, attackers are abusing APIs and exploiting vulnerabilities in web-facing applications like SmarterMail (CVE-2026-23760) and GoAnywhere Managed File Transfer to drop ransomware payloads immediately after public disclosure.
- Cloud Systems: The Australian Cyber Security Centre (ACSC) has issued a "High Alert" regarding the active targeting of cloud-hosted online code repositories. Threat actors are using compromised credentials to modify packages and achieve supply-chain compromise, actively scanning repositories for embedded API keys, cryptographic secrets, and hardcoded passwords.
- AI Systems: AI is fundamentally changing the attack surface. Threat actors are deploying AI-native and agent-driven attacks for rapid reconnaissance and highly convincing social engineering. Simultaneously, organisations face new data leakage risks from AI environments—as seen in the recent exposure of Anthropic's Claude Code source material—demonstrating how AI developmental pipelines can inadvertently expose intellectual property to the public.
Strengthening Your Defences
The margin for error in patching and configuration management is shrinking rapidly. Today's threat actors are bypassing traditional perimeters, moving laterally, and exfiltrating data in a matter of hours. To maintain operational resilience, Australian organisations must adopt a proactive, intelligence-driven approach to cybersecurity, focusing heavily on rigorous cloud hygiene, API hardening, and continuous threat monitoring.
Contact us for a quote for penetration testing service or adversary simulation.

Australian Daily Threat Briefing: Zero-Days, SaaS Supply Chains, and AI-Driven Cyber Risks
As a senior penetration tester monitoring the Australian threat landscape, I routinely analyse the tactics, techniques, and procedures (TTPs) deployed against our domestic networks. Over the last 24 hours leading up to 04 April 2026, we have observed a significant escalation in targeted cyber campaigns. The environment has shifted definitively from opportunistic infrastructure attacks to highly orchestrated, identity-driven breaches.
As a senior penetration tester monitoring the Australian threat landscape, I routinely analyse the tactics, techniques, and procedures (TTPs) deployed against our domestic networks. Over the last 24 hours leading up to 04 April 2026, we have observed a significant escalation in targeted cyber campaigns. The environment has shifted definitively from opportunistic infrastructure attacks to highly orchestrated, identity-driven breaches.
Below is your daily threat briefing, summarising the current and emerging cyber threats, prominent threat actors, and critical vulnerabilities affecting key Australian sectors.
Sector-Specific Threat Analysis
Healthcare & SaaS Providers The Australian healthcare sector remains under immense ransomware pressure. In recent days, the DragonForce ransomware group successfully breached an Australian healthcare software provider, threatening to release sensitive medical data. This incident perfectly illustrates the vulnerability of our supply chains; attackers are actively compromising third-party SaaS vendors to execute lateral movement into interconnected hospital networks and clinics. For healthcare providers relying heavily on SaaS, a single compromised vendor can lead to sector-wide patient service disruption.
FinTech & eCommerce FinTech and eCommerce platforms are facing sophisticated, financially motivated extortion campaigns. The regulatory environment in Australia is hardening in response, as evidenced by the recent $2.5 million fine handed down to an investment firm over cyber governance failures. Furthermore, threat actors are aggressively targeting payment processing APIs and cloud-hosted eCommerce databases, bypassing traditional perimeter defences to execute mass data theft and financial fraud.
Government & Education / EdTech State-sponsored actors and cybercriminal syndicates are maintaining high operational tempos against government agencies and the education sector. Following recent major cloud breaches impacting suppliers of legal and government data, the Australian Signals Directorate (ASD) has strongly reiterated warnings about the danger of legacy IT assets. EdTech platforms and university student management systems continue to be lucrative targets, with attackers hunting for rich repositories of personally identifiable information (PII) via compromised third-party access.
IoT & Critical Infrastructure Connected devices and network-edge hardware are currently under siege. Threat actors are deploying novel malware toolkits designed specifically to infect network-edge devices and maintain long-term, stealthy access for cyber-espionage. Simultaneously, our threat intelligence feeds are tracking over 400 IP addresses systematically exploiting vulnerabilities across web-facing operational technology and IoT infrastructure globally.
Vulnerability Spotlight: Web, APIs, Cloud, and AI Systems
To maintain a proactive defence, security teams must understand the exact mechanisms adversaries are exploiting today:
- Web Applications: An emergency patch has just been released for an active Google Chrome Zero-Day (CVE-2026-5281). This high-severity use-after-free vulnerability in the WebGPU component is already being exploited in the wild, allowing threat actors to execute arbitrary code via malicious web applications.
- APIs & Cloud Platforms: The boundary between legitimate use and exploitation is blurring. We are tracking a surge in identity-driven API attacks, where threat actors harvest compromised credentials to bypass multi-factor authentication (MFA), breach SaaS platforms, and pivot into connected corporate environments. Cloud storage environments and unauthenticated API endpoints remain critical weak points due to misconfigurations in Identity and Access Management (IAM).
- AI Systems: Adversary behaviour is rapidly adapting to the era of Artificial Intelligence. AI is being operationalised to conduct rapid reconnaissance, scale convincing phishing campaigns, and deploy hyper-realistic deepfake audio and video. These deepfakes are specifically being weaponised against finance teams for executive impersonation and Business Email Compromise (BEC). Furthermore, as organisations deploy internal AI tools, we are seeing emerging attack vectors like prompt injection and model data poisoning, which trick AI assistants into leaking sensitive corporate data or granting unauthorised access.
- Network Edge & IoT: Server-Side Request Forgery (SSRF) vulnerabilities remain highly exploitable. Attackers are heavily targeting unpatched SSRF flaws on network-edge IoT devices to bypass perimeter firewalls and establish persistent footholds inside corporate networks.
Defensive Recommendations
The ASD notes that the average cost of a cyber attack for large Australian businesses has surged to over $200,000 per incident. Australian organisations must move beyond passive defence. Aligning with the ACSC Essential Eight is merely a baseline. Modern resilience requires continuous network monitoring, rigorous patching of edge devices, strict third-party risk management, and the implementation of phishing-resistant MFA.
Most importantly, you must proactively test your cloud perimeters, web applications, and AI deployments before a threat actor does.
Contact us for a quote for penetration testing service or adversary simulation.

The 2026 Shift from Annual Compliance to Continuous Penetration Testing and Red Teaming in Australia
Upgrade from annual pen tests to continuous penetration testing services in Australia. Discover 2026 red teaming trends, PTaaS, and expert security assessments.
Beyond the Checkbox: Why Continuous Penetration Testing & Red Teaming Are Essential in 2026
The cybersecurity landscape has reached a pivotal turning point in 2026. We are no longer living in an era where cyber threats evolve month by month; today, they evolve minute by minute. With the explosive rise of AI-assisted exploit chaining, sophisticated Phishing-as-a-Service (PHaaS), and automated vulnerability discovery, threat actors are moving at machine speed.
If your organisation relies solely on a traditional, once-a-year pen test to check a compliance box, you are inherently operating with a massive blind spot. By the time that static PDF report lands on your desk, your digital environment has already shifted, and new security weaknesses have likely emerged. In Australia, regulatory bodies and enterprise boards are waking up to this reality, sparking a massive shift toward continuous, intelligence-led offensive security.
Whether you are seeking a premier penetration testing service or looking to test your in-house defenders through a full-scale red team engagement, understanding how testing methodologies have evolved is crucial for protecting your bottom line. Let’s dive into the current state of penetration testing Australia and how you can stay ahead of the curve.
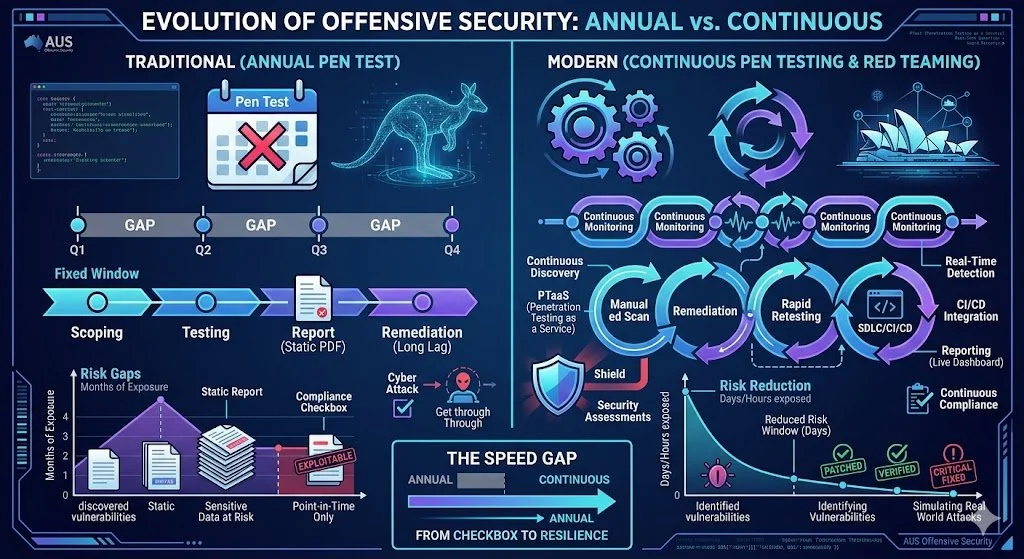
Evolution of offensive security: Annual vs Continuous
Why Annual Penetration Testing is Failing Modern Businesses
In the past, organisations scheduled a penetration test service once a year to satisfy auditors and renew their cyber insurance. While point-in-time assessments still hold value for specific baseline checks, they fail to account for the velocity of modern development. Every time your engineering team pushes a code update, launches a new microservice, or modifies a cloud configuration, your attack surface changes.
The "Speed Gap" and AI-Assisted Attacks
In 2026, attackers are heavily leveraging generative AI to automate reconnaissance and craft highly convincing, hyper-personalised lures. They chain together low-severity vulnerabilities to execute a devastating cyber attack. This creates a "speed gap" between rapid threat evolution and static, calendar-based testing cycles. If an exploitable flaw is introduced to your network in February, waiting until your annual test in November leaves your sensitive data exposed for nine months. A modern cyber security posture demands agility.
Evolving Australian Regulatory Pressures
The Australian regulatory environment is actively tightening to combat these threats. With the expansion of the Security of Critical Infrastructure (SOCI) Act, APRA CPS 234, and strict PCI DSS 4.0 enforcement, regulators no longer accept simple policy documentation. They require demonstrable technical validation of your security controls. Boards now expect quantified risk reduction, pushing organisations to partner with an elite penetration testing provider that can translate technical risks into business impact.
The Rise of Penetration Testing as a Service (PTaaS)
To bridge the speed gap, the industry is heavily adopting penetration testing as a service (PTaaS). This model represents a fundamental shift in how testing services are delivered.
Instead of a siloed engagement, a penetration test as a service integrates directly into your Software Development Life Cycle (SDLC) and CI/CD pipelines. This approach combines the scale of automated vulnerability scanning with the contextual intelligence of an expert human penetration tester.
When you engage reputable penetration testing service providers for PTaaS, you receive:
Continuous Monitoring: Rapid identification of new exposures in real-time.
On-Demand Retesting: The ability to instantly verify that a vulnerability has been successfully remediated by your development team.
Actionable Dashboards: Live insights into your risk posture rather than a static annual report.
By moving to continuous penetration testing services, Australian businesses reduce their window of exposure from months to mere days, ensuring exploitable vulnerabilities are patched before threat actors can weaponise them.
Red Teaming: Simulating Real World Attacks
While standard penetration test services focus on finding as many vulnerabilities as possible within a defined scope, red teaming takes a vastly different approach. Red teaming is about simulating real world attacks to test how well your people, processes, and technology respond to a determined, covert adversary.
A mature penetration testing service in australia will deploy a red team to mimic the exact Tactics, Techniques, and Procedures (TTPs) of known threat actors targeting your specific industry. This multi-layered assessment often occurs over weeks or months and tests the defensive capabilities (the "Blue Team") of your organisations.
Red teaming pushes beyond digital borders, often incorporating:
Advanced Social Engineering: Spear-phishing executives, voice cloning (vishing), and deepfake exploitation to bypass initial access controls.
Physical Breaches: Assessing facility security by attempting to clone badges, tailgate employees, or plant rogue devices on the corporate network.
Evasion Tactics: Testing if the Security Operations Centre (SOC) can detect lateral movement, privilege escalation, and data exfiltration without alerting the attackers.
For organisations with a mature security posture, red teaming provides the ultimate reality check.
Core Focus Areas for 2026: APIs, Cloud, and Identity
As perimeters dissolve and workforces remain distributed, threat actors have shifted their crosshairs. A comprehensive security strategy must prioritise the following critical areas:
1. API Penetration Testing Services
Application Programming Interfaces (APIs) are the backbone of modern digital architecture, connecting countless microservices and third-party apps. Unfortunately, they are also frequently under-tested and over-trusted. In 2026, APIs are essentially the backdoor to your data. Specialized API penetration testing services are crucial to identify broken object level authorisation (BOLA), mass assignment flaws, and rate-limiting failures that automated scanners completely miss.
2. Active Directory Penetration Testing Service
If a threat actor gains a foothold in your network, their next immediate goal is lateral movement and privilege escalation. Your Active Directory (AD) or Entra ID environment is the keys to the kingdom. An expert active directory penetration testing service uncovers misconfigurations, weak password policies, and excessive permissions that could allow an attacker to achieve total domain compromise.
3. Application Security
Your customer-facing applications are your most visible attack surface. Engaging dedicated web application testing and a robust mobile application penetration testing service ensures that your software is resilient against complex logic flaws, session hijacking, and insecure data storage. For organisations heavily invested in mobile ecosystems, engaging recurring mobile application penetration testing services is non-negotiable to protect consumer trust and comply with global privacy laws.
How Penetration Testing Involves Identifying Vulnerabilities
If you are new to the process, you might wonder what a thorough engagement looks like. Penetration testing involves a highly structured methodology to ensure safety, comprehensiveness, and accuracy.
Scoping and Rules of Engagement: The provider works collaboratively with you to define what systems are in bounds, what techniques are off-limits, and the ultimate goals of the assessment.
Reconnaissance & Threat Modelling: Testers gather open-source intelligence (OSINT) to understand your digital footprint, identifying exposed credentials or shadow IT assets.
Identifying Vulnerabilities: Using a blend of bespoke automated tooling and deep manual analysis, experts search for weak points.
Exploitation: The critical step. Testers actively exploit the findings to validate the risk. This proves whether a theoretical vulnerability can actually lead to unauthorised access.
Reporting and Remediation: You receive a prioritised, highly detailed report outlining the business impact of each flaw, alongside precise, actionable remediation guidance.
Understanding Penetration Testing Cost in Australia
Budgeting for security is a common concern. Penetration testing cost varies wildly depending on the size of your infrastructure, the depth of the assessment, and the prestige of the firm. Below is a high-level guide to help you budget for penetration testing sydney and across Australia in 2026.
| Service Type | Typical Scope | Estimated Cost (AUD) |
|---|---|---|
| Web / Mobile App Test | Single application, API endpoints, role-based access checks. | $8,000 - $25,000+ |
| Internal Network Test | Active Directory, workstations, internal servers, lateral movement. | $12,000 - $35,000+ |
| Cloud Infrastructure Test | AWS/Azure/GCP configurations, IAM roles, container security. | $15,000 - $40,000+ |
| Full Red Team Engagement | Multi-month simulation, physical security, social engineering, evasion. | $45,000 - $150,000+ |
| Continuous PTaaS | Ongoing SDLC integration, automated scanning, manual verification. | $3,000 - $10,000+ / month |
Note: These estimates are indicative. Always request a custom scoping call with your provider to get an accurate quote tailored to your environment.
Types of Penetration Tests You Should Consider
Depending on your maturity and specific security standards, there are several types of penetration tests to integrate into your strategy:
Black Box Testing: Testers are given zero prior knowledge of the environment, perfectly mimicking an external, unauthenticated attacker.
Grey Box Testing: Testers are provided with basic user credentials and partial knowledge. This is the most common and efficient approach for application penetration testing, simulating a malicious insider or a compromised user account.
White Box Testing: Testers have full access to source code and architecture diagrams. This provides the most comprehensive evaluation of your code base and underlying logic.
Securing Your Future Today
The question is no longer if your organisation will be targeted, but when, and whether your defences will hold up against an adversary operating at the speed of modern AI. Clinging to outdated, annual compliance-driven testing methodologies is a dangerous gamble with your company's reputation and intellectual property.
By embracing continuous testing models, robust API and cloud scrutiny, and realistic red teaming exercises, you transition your security posture from reactive to proactively resilient.
Ready to mature your security operations and close the speed gap? Contact our expert team today for a confidential scoping call and customised quote. Let’s collaborate to build a defence strategy that stands up to the reality of 2026.