
Daily Cyber Threat Briefing: High-Velocity Ransomware and Cloud Supply Chain Risks in Australia
As the Australian digital landscape continues to expand, so does the sophistication and speed of modern threat actors. Over the last 24 hours, security teams across the country have faced an elevated operational tempo of cyber activity, ranging from browser-based zero-day exploitation to high-velocity ransomware deployments. In this daily briefing, we analyse the latest threat intelligence, prominent adversaries, and critical vulnerabilities impacting key Australian sectors.
07 April 2026
As the Australian digital landscape continues to expand, so does the sophistication and speed of modern threat actors. Over the last 24 hours, security teams across the country have faced an elevated operational tempo of cyber activity, ranging from browser-based zero-day exploitation to high-velocity ransomware deployments. In this daily briefing, we analyse the latest threat intelligence, prominent adversaries, and critical vulnerabilities impacting key Australian sectors.
Sector Threat Landscape
Healthcare The healthcare sector remains under immense pressure from both hacktivists and financially motivated syndicates. Following a recent cyber incident involving medical device manufacturer Stryker, the Iranian-linked hacktivist group Handala claims to have wiped and exfiltrated terabytes of sensitive data. Simultaneously, the Aeromedical Society of Australasia (ASA) is currently navigating a ransomware incident tied to the LockBit 5.0 group. Furthermore, the China-linked actor Storm-1175 has been aggressively targeting Australian healthcare organisations with Medusa ransomware, successfully moving from initial breach to encryption in under 24 hours.
FinTech Financial technology platforms are facing intense scrutiny regarding data protection. The Australian FinTech platform youX recently confirmed a massive cloud breach. Attackers gained unauthorised access to a MongoDB Atlas cluster, exposing 141 gigabytes of data and potentially compromising over 600,000 loan applications. This incident highlights the severe operational impact of cloud database misconfigurations and insecure integrations.
SaaS Providers & Government Supply chain attacks targeting Software-as-a-Service (SaaS) providers continue to present systemic risks to government entities. A major cloud breach at LexisNexis has exposed sensitive data affecting several Australian law firms, courts, and federal agencies. In response to these cascading disruptions across critical networks, the Australian Government is actively consulting industry on reforms to the Security of Critical Infrastructure (SOCI) framework to strengthen governmental intervention powers during catastrophic cyber incidents.
Education / EdTech Educational institutions are increasingly targeted for their vast repositories of personal identifying information (PII). The Victorian Department of Education recently suffered a breach where student names, school emails, and encrypted passwords were accessed by an unauthorised party. Furthermore, the Australian education sector has been heavily featured on Storm-1175's target list as they scan for vulnerable perimeter assets.
eCommerce & IoT For eCommerce and retail platforms, the primary threat vector is shifting towards browser-based SaaS attacks and identity abuse, effectively bypassing traditional endpoint security. In the Internet of Things (IoT) and Operational Technology (OT) spaces, authorities are warning of severe vulnerabilities in edge devices. Threat actors are actively exploiting unpatched internet-facing routers and VPN concentrators to infiltrate corporate networks, with the ACSC noting that edge compromises boast an alarming success rate.
Vulnerability Spotlight: Web Apps, APIs, Cloud, and AI Systems
Adversaries are exploiting a range of emerging vulnerabilities across the technology stack:
- Web Applications & APIs: Threat actors are weaponising zero-day vulnerabilities at an unprecedented rate. Google recently issued an emergency patch for a high-severity Chrome zero-day (CVE-2026-5281) that is actively being exploited in the wild. Additionally, attackers are abusing APIs and exploiting vulnerabilities in web-facing applications like SmarterMail (CVE-2026-23760) and GoAnywhere Managed File Transfer to drop ransomware payloads immediately after public disclosure.
- Cloud Systems: The Australian Cyber Security Centre (ACSC) has issued a "High Alert" regarding the active targeting of cloud-hosted online code repositories. Threat actors are using compromised credentials to modify packages and achieve supply-chain compromise, actively scanning repositories for embedded API keys, cryptographic secrets, and hardcoded passwords.
- AI Systems: AI is fundamentally changing the attack surface. Threat actors are deploying AI-native and agent-driven attacks for rapid reconnaissance and highly convincing social engineering. Simultaneously, organisations face new data leakage risks from AI environments—as seen in the recent exposure of Anthropic's Claude Code source material—demonstrating how AI developmental pipelines can inadvertently expose intellectual property to the public.
Strengthening Your Defences
The margin for error in patching and configuration management is shrinking rapidly. Today's threat actors are bypassing traditional perimeters, moving laterally, and exfiltrating data in a matter of hours. To maintain operational resilience, Australian organisations must adopt a proactive, intelligence-driven approach to cybersecurity, focusing heavily on rigorous cloud hygiene, API hardening, and continuous threat monitoring.
Contact us for a quote for penetration testing service or adversary simulation.
Australian Daily Threat Briefing: Zero-Days, SaaS Supply Chains, and AI-Driven Cyber Risks
As a senior penetration tester monitoring the Australian threat landscape, I routinely analyse the tactics, techniques, and procedures (TTPs) deployed against our domestic networks. Over the last 24 hours leading up to 04 April 2026, we have observed a significant escalation in targeted cyber campaigns. The environment has shifted definitively from opportunistic infrastructure attacks to highly orchestrated, identity-driven breaches.
As a senior penetration tester monitoring the Australian threat landscape, I routinely analyse the tactics, techniques, and procedures (TTPs) deployed against our domestic networks. Over the last 24 hours leading up to 04 April 2026, we have observed a significant escalation in targeted cyber campaigns. The environment has shifted definitively from opportunistic infrastructure attacks to highly orchestrated, identity-driven breaches.
Below is your daily threat briefing, summarising the current and emerging cyber threats, prominent threat actors, and critical vulnerabilities affecting key Australian sectors.
Sector-Specific Threat Analysis
Healthcare & SaaS Providers The Australian healthcare sector remains under immense ransomware pressure. In recent days, the DragonForce ransomware group successfully breached an Australian healthcare software provider, threatening to release sensitive medical data. This incident perfectly illustrates the vulnerability of our supply chains; attackers are actively compromising third-party SaaS vendors to execute lateral movement into interconnected hospital networks and clinics. For healthcare providers relying heavily on SaaS, a single compromised vendor can lead to sector-wide patient service disruption.
FinTech & eCommerce FinTech and eCommerce platforms are facing sophisticated, financially motivated extortion campaigns. The regulatory environment in Australia is hardening in response, as evidenced by the recent $2.5 million fine handed down to an investment firm over cyber governance failures. Furthermore, threat actors are aggressively targeting payment processing APIs and cloud-hosted eCommerce databases, bypassing traditional perimeter defences to execute mass data theft and financial fraud.
Government & Education / EdTech State-sponsored actors and cybercriminal syndicates are maintaining high operational tempos against government agencies and the education sector. Following recent major cloud breaches impacting suppliers of legal and government data, the Australian Signals Directorate (ASD) has strongly reiterated warnings about the danger of legacy IT assets. EdTech platforms and university student management systems continue to be lucrative targets, with attackers hunting for rich repositories of personally identifiable information (PII) via compromised third-party access.
IoT & Critical Infrastructure Connected devices and network-edge hardware are currently under siege. Threat actors are deploying novel malware toolkits designed specifically to infect network-edge devices and maintain long-term, stealthy access for cyber-espionage. Simultaneously, our threat intelligence feeds are tracking over 400 IP addresses systematically exploiting vulnerabilities across web-facing operational technology and IoT infrastructure globally.
Vulnerability Spotlight: Web, APIs, Cloud, and AI Systems
To maintain a proactive defence, security teams must understand the exact mechanisms adversaries are exploiting today:
- Web Applications: An emergency patch has just been released for an active Google Chrome Zero-Day (CVE-2026-5281). This high-severity use-after-free vulnerability in the WebGPU component is already being exploited in the wild, allowing threat actors to execute arbitrary code via malicious web applications.
- APIs & Cloud Platforms: The boundary between legitimate use and exploitation is blurring. We are tracking a surge in identity-driven API attacks, where threat actors harvest compromised credentials to bypass multi-factor authentication (MFA), breach SaaS platforms, and pivot into connected corporate environments. Cloud storage environments and unauthenticated API endpoints remain critical weak points due to misconfigurations in Identity and Access Management (IAM).
- AI Systems: Adversary behaviour is rapidly adapting to the era of Artificial Intelligence. AI is being operationalised to conduct rapid reconnaissance, scale convincing phishing campaigns, and deploy hyper-realistic deepfake audio and video. These deepfakes are specifically being weaponised against finance teams for executive impersonation and Business Email Compromise (BEC). Furthermore, as organisations deploy internal AI tools, we are seeing emerging attack vectors like prompt injection and model data poisoning, which trick AI assistants into leaking sensitive corporate data or granting unauthorised access.
- Network Edge & IoT: Server-Side Request Forgery (SSRF) vulnerabilities remain highly exploitable. Attackers are heavily targeting unpatched SSRF flaws on network-edge IoT devices to bypass perimeter firewalls and establish persistent footholds inside corporate networks.
Defensive Recommendations
The ASD notes that the average cost of a cyber attack for large Australian businesses has surged to over $200,000 per incident. Australian organisations must move beyond passive defence. Aligning with the ACSC Essential Eight is merely a baseline. Modern resilience requires continuous network monitoring, rigorous patching of edge devices, strict third-party risk management, and the implementation of phishing-resistant MFA.
Most importantly, you must proactively test your cloud perimeters, web applications, and AI deployments before a threat actor does.
Contact us for a quote for penetration testing service or adversary simulation.
The 2026 Shift from Annual Compliance to Continuous Penetration Testing and Red Teaming in Australia
Upgrade from annual pen tests to continuous penetration testing services in Australia. Discover 2026 red teaming trends, PTaaS, and expert security assessments.
Beyond the Checkbox: Why Continuous Penetration Testing & Red Teaming Are Essential in 2026
The cybersecurity landscape has reached a pivotal turning point in 2026. We are no longer living in an era where cyber threats evolve month by month; today, they evolve minute by minute. With the explosive rise of AI-assisted exploit chaining, sophisticated Phishing-as-a-Service (PHaaS), and automated vulnerability discovery, threat actors are moving at machine speed.
If your organisation relies solely on a traditional, once-a-year pen test to check a compliance box, you are inherently operating with a massive blind spot. By the time that static PDF report lands on your desk, your digital environment has already shifted, and new security weaknesses have likely emerged. In Australia, regulatory bodies and enterprise boards are waking up to this reality, sparking a massive shift toward continuous, intelligence-led offensive security.
Whether you are seeking a premier penetration testing service or looking to test your in-house defenders through a full-scale red team engagement, understanding how testing methodologies have evolved is crucial for protecting your bottom line. Let’s dive into the current state of penetration testing Australia and how you can stay ahead of the curve.
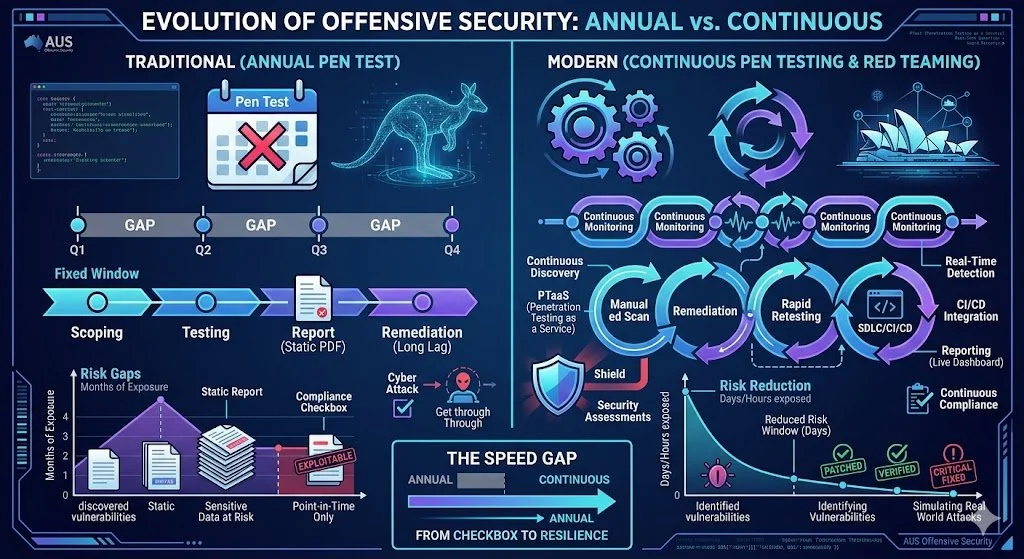
Evolution of offensive security: Annual vs Continuous
Why Annual Penetration Testing is Failing Modern Businesses
In the past, organisations scheduled a penetration test service once a year to satisfy auditors and renew their cyber insurance. While point-in-time assessments still hold value for specific baseline checks, they fail to account for the velocity of modern development. Every time your engineering team pushes a code update, launches a new microservice, or modifies a cloud configuration, your attack surface changes.
The "Speed Gap" and AI-Assisted Attacks
In 2026, attackers are heavily leveraging generative AI to automate reconnaissance and craft highly convincing, hyper-personalised lures. They chain together low-severity vulnerabilities to execute a devastating cyber attack. This creates a "speed gap" between rapid threat evolution and static, calendar-based testing cycles. If an exploitable flaw is introduced to your network in February, waiting until your annual test in November leaves your sensitive data exposed for nine months. A modern cyber security posture demands agility.
Evolving Australian Regulatory Pressures
The Australian regulatory environment is actively tightening to combat these threats. With the expansion of the Security of Critical Infrastructure (SOCI) Act, APRA CPS 234, and strict PCI DSS 4.0 enforcement, regulators no longer accept simple policy documentation. They require demonstrable technical validation of your security controls. Boards now expect quantified risk reduction, pushing organisations to partner with an elite penetration testing provider that can translate technical risks into business impact.
The Rise of Penetration Testing as a Service (PTaaS)
To bridge the speed gap, the industry is heavily adopting penetration testing as a service (PTaaS). This model represents a fundamental shift in how testing services are delivered.
Instead of a siloed engagement, a penetration test as a service integrates directly into your Software Development Life Cycle (SDLC) and CI/CD pipelines. This approach combines the scale of automated vulnerability scanning with the contextual intelligence of an expert human penetration tester.
When you engage reputable penetration testing service providers for PTaaS, you receive:
Continuous Monitoring: Rapid identification of new exposures in real-time.
On-Demand Retesting: The ability to instantly verify that a vulnerability has been successfully remediated by your development team.
Actionable Dashboards: Live insights into your risk posture rather than a static annual report.
By moving to continuous penetration testing services, Australian businesses reduce their window of exposure from months to mere days, ensuring exploitable vulnerabilities are patched before threat actors can weaponise them.
Red Teaming: Simulating Real World Attacks
While standard penetration test services focus on finding as many vulnerabilities as possible within a defined scope, red teaming takes a vastly different approach. Red teaming is about simulating real world attacks to test how well your people, processes, and technology respond to a determined, covert adversary.
A mature penetration testing service in australia will deploy a red team to mimic the exact Tactics, Techniques, and Procedures (TTPs) of known threat actors targeting your specific industry. This multi-layered assessment often occurs over weeks or months and tests the defensive capabilities (the "Blue Team") of your organisations.
Red teaming pushes beyond digital borders, often incorporating:
Advanced Social Engineering: Spear-phishing executives, voice cloning (vishing), and deepfake exploitation to bypass initial access controls.
Physical Breaches: Assessing facility security by attempting to clone badges, tailgate employees, or plant rogue devices on the corporate network.
Evasion Tactics: Testing if the Security Operations Centre (SOC) can detect lateral movement, privilege escalation, and data exfiltration without alerting the attackers.
For organisations with a mature security posture, red teaming provides the ultimate reality check.
Core Focus Areas for 2026: APIs, Cloud, and Identity
As perimeters dissolve and workforces remain distributed, threat actors have shifted their crosshairs. A comprehensive security strategy must prioritise the following critical areas:
1. API Penetration Testing Services
Application Programming Interfaces (APIs) are the backbone of modern digital architecture, connecting countless microservices and third-party apps. Unfortunately, they are also frequently under-tested and over-trusted. In 2026, APIs are essentially the backdoor to your data. Specialized API penetration testing services are crucial to identify broken object level authorisation (BOLA), mass assignment flaws, and rate-limiting failures that automated scanners completely miss.
2. Active Directory Penetration Testing Service
If a threat actor gains a foothold in your network, their next immediate goal is lateral movement and privilege escalation. Your Active Directory (AD) or Entra ID environment is the keys to the kingdom. An expert active directory penetration testing service uncovers misconfigurations, weak password policies, and excessive permissions that could allow an attacker to achieve total domain compromise.
3. Application Security
Your customer-facing applications are your most visible attack surface. Engaging dedicated web application testing and a robust mobile application penetration testing service ensures that your software is resilient against complex logic flaws, session hijacking, and insecure data storage. For organisations heavily invested in mobile ecosystems, engaging recurring mobile application penetration testing services is non-negotiable to protect consumer trust and comply with global privacy laws.
How Penetration Testing Involves Identifying Vulnerabilities
If you are new to the process, you might wonder what a thorough engagement looks like. Penetration testing involves a highly structured methodology to ensure safety, comprehensiveness, and accuracy.
Scoping and Rules of Engagement: The provider works collaboratively with you to define what systems are in bounds, what techniques are off-limits, and the ultimate goals of the assessment.
Reconnaissance & Threat Modelling: Testers gather open-source intelligence (OSINT) to understand your digital footprint, identifying exposed credentials or shadow IT assets.
Identifying Vulnerabilities: Using a blend of bespoke automated tooling and deep manual analysis, experts search for weak points.
Exploitation: The critical step. Testers actively exploit the findings to validate the risk. This proves whether a theoretical vulnerability can actually lead to unauthorised access.
Reporting and Remediation: You receive a prioritised, highly detailed report outlining the business impact of each flaw, alongside precise, actionable remediation guidance.
Understanding Penetration Testing Cost in Australia
Budgeting for security is a common concern. Penetration testing cost varies wildly depending on the size of your infrastructure, the depth of the assessment, and the prestige of the firm. Below is a high-level guide to help you budget for penetration testing sydney and across Australia in 2026.
| Service Type | Typical Scope | Estimated Cost (AUD) |
|---|---|---|
| Web / Mobile App Test | Single application, API endpoints, role-based access checks. | $8,000 - $25,000+ |
| Internal Network Test | Active Directory, workstations, internal servers, lateral movement. | $12,000 - $35,000+ |
| Cloud Infrastructure Test | AWS/Azure/GCP configurations, IAM roles, container security. | $15,000 - $40,000+ |
| Full Red Team Engagement | Multi-month simulation, physical security, social engineering, evasion. | $45,000 - $150,000+ |
| Continuous PTaaS | Ongoing SDLC integration, automated scanning, manual verification. | $3,000 - $10,000+ / month |
Note: These estimates are indicative. Always request a custom scoping call with your provider to get an accurate quote tailored to your environment.
Types of Penetration Tests You Should Consider
Depending on your maturity and specific security standards, there are several types of penetration tests to integrate into your strategy:
Black Box Testing: Testers are given zero prior knowledge of the environment, perfectly mimicking an external, unauthenticated attacker.
Grey Box Testing: Testers are provided with basic user credentials and partial knowledge. This is the most common and efficient approach for application penetration testing, simulating a malicious insider or a compromised user account.
White Box Testing: Testers have full access to source code and architecture diagrams. This provides the most comprehensive evaluation of your code base and underlying logic.
Securing Your Future Today
The question is no longer if your organisation will be targeted, but when, and whether your defences will hold up against an adversary operating at the speed of modern AI. Clinging to outdated, annual compliance-driven testing methodologies is a dangerous gamble with your company's reputation and intellectual property.
By embracing continuous testing models, robust API and cloud scrutiny, and realistic red teaming exercises, you transition your security posture from reactive to proactively resilient.
Ready to mature your security operations and close the speed gap? Contact our expert team today for a confidential scoping call and customised quote. Let’s collaborate to build a defence strategy that stands up to the reality of 2026.
Australian Daily Cyber Threat Briefing – 02 April 2026
Welcome to today's threat intelligence briefing. As organisations across Australia continue to digitise operations and adopt next-generation technologies, the local threat landscape is evolving at an unprecedented pace. Over the last 24 hours, our penetration testing and threat intelligence teams have observed significant adversarial behaviour targeting critical Australian infrastructure.
Welcome to today's threat intelligence briefing. As organisations across Australia continue to digitise operations and adopt next-generation technologies, the local threat landscape is evolving at an unprecedented pace. Over the last 24 hours, our penetration testing and threat intelligence teams have observed significant adversarial behaviour targeting critical Australian infrastructure.
Below is a deep-dive analysis of the current and emerging threats you need to monitor for today, 02 April 2026.
Sector-Specific Threat Analysis
Healthcare & AI Systems The Australian healthcare sector is increasingly adopting AI-driven diagnostic and patient triage tools. In the past 24 hours, we have seen proof-of-concept (PoC) exploits circulating for a novel prompt injection vulnerability affecting a popular cloud-based AI triage application used by several regional hospitals. By manipulating user inputs, attackers can bypass application guardrails (exploiting Insecure Output Handling) to coerce the AI model into leaking highly sensitive patient Personally Identifiable Information (PII). Pentester’s Takeaway: Treat all Large Language Model (LLM) inputs as untrusted. Ensure robust input sanitisation and implement strict data access controls within your AI models.
FinTech & API Security A coordinated reconnaissance campaign targeting Australian FinTech startups has been detected, specifically focusing on mobile application APIs. Threat actors are actively probing for Broken Object Level Authorisation (BOLA) vulnerabilities. By manipulating API request parameters (such as user IDs in the endpoint URI), attackers have successfully accessed the financial records and transactional data of unauthorised users. Pentester’s Takeaway: APIs are the backbone of modern FinTech. Organisations must implement rigorous access controls at the object level and conduct regular API penetration testing to identify logical flaws that automated scanners miss.
Government, SaaS Providers & Cloud Infrastructure A critical vulnerability in a widely used third-party SaaS HR platform has put several Australian government departments on high alert today. The flaw involves a Server-Side Request Forgery (SSRF) vulnerability within the SaaS provider's core web application. This flaw allows attackers to pivot into the underlying AWS cloud environment. By exploiting overly permissive Identity and Access Management (IAM) roles, threat actors are attempting lateral movement to access sensitive government data stored in cloud buckets. Pentester’s Takeaway: Defence-in-depth is non-negotiable. Enforce the principle of least privilege across all cloud IAM roles and strictly restrict outbound traffic from web application servers to mitigate SSRF impacts.
eCommerce & Web Applications Australian eCommerce platforms are currently facing a wave of sophisticated supply-chain attacks. Overnight, an emerging threat group has begun exploiting an unpatched deserialisation vulnerability in a popular open-source shopping cart framework. Once exploited, it grants remote code execution (RCE), allowing attackers to inject malicious skimming scripts directly into the checkout process, silently exfiltrating Australian consumer credit card details. Pentester’s Takeaway: Maintain a comprehensive Software Bill of Materials (SBOM) and ensure all third-party libraries and web application frameworks are aggressively patched.
Education/EdTech & IoT The Education sector, alongside modern smart-campus initiatives, is witnessing increased exploitation activity targeting Internet of Things (IoT) infrastructure. A newly discovered zero-day exploit targeting the firmware of a prominent brand of smart security cameras and building management IoT sensors is being actively weaponised. Threat actors are incorporating these compromised devices into high-volume botnets to launch Distributed Denial of Service (DDoS) attacks against university networks and EdTech portals, threatening to disrupt online learning programmes. Pentester’s Takeaway: Always segment IoT devices from corporate, faculty, and student networks. Ensure default IoT credentials are changed immediately and firmware update programmes are strictly enforced.
Conclusion
The shift towards complex cloud environments, interconnected APIs, and AI integrations has drastically expanded the attack surface for Australian organisations. As adversarial behaviour becomes more sophisticated, proactive identification and remediation of vulnerabilities are paramount to defending your digital assets.
Contact us for a quote for penetration testing service or adversary simulation.
Daily Threat Briefing - 1 April 2026: AI, Cloud, and Supply Chain Under Siege
As a senior penetration tester actively analysing the adversarial landscape, I am seeing a dramatic escalation in sophisticated attacks against Australian organisations. Over the last 24 hours, the threat landscape has been dominated by supply chain compromises, AI-driven exploitation, and aggressive ransomware campaigns targeting critical infrastructure.
As a senior penetration tester actively analysing the adversarial landscape, I am seeing a dramatic escalation in sophisticated attacks against Australian organisations. Over the last 24 hours, the threat landscape has been dominated by supply chain compromises, AI-driven exploitation, and aggressive ransomware campaigns targeting critical infrastructure.
Here is your daily threat briefing for 1 April 2026, detailing the tactics and vulnerabilities you need to prioritise today.
Government & SaaS Providers: Supply Chain and Web Application Threats
Today, the Australian Signals Directorate’s ACSC issued a high-priority alert regarding the active targeting of online code repositories. Threat actors are hijacking developer environments via compromised authentication tokens and social engineering to modify public packages and scrape for cryptographic secrets.
Furthermore, the SaaS supply chain remains highly vulnerable. The recent LexisNexis cloud breach has exposed critical data linked to Australian federal government agencies and law firms. We are also tracking the exploitation of "React2Shell," a critical vulnerability in unpatched web applications that recently facilitated the FulcrumSec breach of government platforms.
Healthcare & IoT: Ransomware and Edge Exploitation
The healthcare sector remains in the crosshairs of extortion groups. The DragonForce ransomware syndicate recently compromised Health Management Systems, an Australian healthcare SaaS provider, threatening to leak sensitive medical data. Concurrently, the INC Ransom group is actively targeting Australian medical and professional services. These adversaries are using legitimate administrative tools like rclone and 7-Zip to blend in with normal network behaviour and bypass traditional defences.
On the infrastructure and IoT front, attackers are exploiting network perimeters to reach vulnerable connected devices. The recent zero-day exploitation of Cisco SD-WAN appliances (CVE-2026-20127) highlights how adversaries are gaining persistent, authenticated access to critical networks.
FinTech & eCommerce: Cloud Misconfigurations and Identity Bypasses
Cloud environments and APIs remain the lowest-hanging fruit for automated scanning tools. The Australian FinTech sector suffered a massive blow with the breach of the youX platform, where threat actors exfiltrated 141 gigabytes of sensitive data. The attackers targeted a misconfigured MongoDB Atlas cluster, likely exploiting the MongoDB Server Leak vulnerability (CVE-2025-14847).
For eCommerce platforms and managed service providers, identity management is currently a critical attack vector. Organisations relying on Fortinet must urgently address the FortiCloud SSO authentication bypass (CVE-2025-59719), which allows unauthenticated attackers to gain complete administrative control.
Education/EdTech & AI Systems: The Weaponisation of Emerging Tech
Generative AI is actively being weaponised against the education sector and beyond. Adversaries are deploying highly convincing AI-generated Phishing-as-a-Service (PHaaS) campaigns to execute Adversary-in-the-Middle (AiTM) attacks, successfully bypassing Multi-Factor Authentication (MFA).
The convergence of AI orchestration and web APIs has also introduced complex new vulnerabilities. We are tracking the active exploitation of "Ni8mare" (CVE-2026-21858)—a CVSS 10.0 unauthenticated Remote Code Execution (RCE) flaw in the n8n workflow automation platform. This serves as a stark warning for EdTech providers and enterprises automating their AI workflows.
Conclusion
Australian organisations must shift from a reactive compliance mindset to proactive cyber defence. With adversaries operating at machine speed and weaponising AI, traditional perimeter defences are no longer sufficient. Continuous validation of your external attack surface, strict API security, and robust secure-by-design cloud architectures are critical.
Contact us for a quote for penetration testing service or adversary simulation.