

Australia Cyber Threat Update: Bulletproof Hosting Crackdown & Critical Fortinet/Cisco Exploits
Australia faces a crackdown on bulletproof hosting and active exploitation of critical Fortinet & Cisco vulnerabilities. Learn to protect your organization from these urgent cyber threats.
Executive Summary
The Australian cyber threat landscape for the last 24 hours has been dominated by a coordinated international response to resilient cybercrime infrastructure and the escalation of attacks against edge devices. The Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC), in conjunction with global partners (CISA, FBI, NCSC-UK), released pivotal guidance yesterday targeting "Bulletproof Hosting" providers. Meanwhile, critical vulnerabilities in Fortinet and Cisco appliances are seeing active exploitation, posing severe risks to Australian organisations relying on these perimeter defence technologies.
Top Strategic Development: Crackdown on Bulletproof Hosting
Sectors Impacted: Government, FinTech, Critical Infrastructure
In a major release on 19 November 2025, the ACSC joined international agencies to publish "Bulletproof Defense: Mitigating Risks From Bulletproof Hosting Providers." Bulletproof hosting (BPH) services are the backbone of the cybercrime economy, allowing ransomware gangs and phishing operators to host malicious content with impunity.
- The Threat: BPH providers knowingly ignore abuse complaints and facilitate high-volume phishing campaigns and C2 (Command and Control) infrastructure.
- Action Required: Australian network defenders and ISPs are urged to review the new guidance to identify and block traffic to and from known BPH IP ranges. This is a critical step for Government and FinTech sectors to reduce the attack surface for ransomware and fraud.
Critical Vulnerabilities Under Active Exploitation
Organisations using web application firewalls (WAFs) and secure gateways must urgently review the following exploits highlighted in the last 24 hours:
1. Fortinet FortiWeb – Critical Authentication Bypass
- CVE: CVE-2025-64446 (CVSS 9.1)
- Status: Active Exploitation Confirmed (Added to CISA KEV on 14 Nov 2025, widely targeted in the last 24 hours).
- Impact: This critical vulnerability allows unauthenticated remote attackers to bypass authentication and gain administrative control over FortiWeb appliances.
- Relevance: High risk for SaaS providers and eCommerce platforms using FortiWeb to protect customer data.
- Recommendation: Patch immediately. If patching is not possible, restrict management interface access to trusted internal IPs only.
2. Cisco ASA & FTD – State-Sponsored Targeting
- CVEs: CVE-2025-20333 (CVSS 9.9) and CVE-2025-20362
- Threat Actor: Linked to UAT4356/Storm-1849 (State-sponsored activity).
- Context: Despite patches being available, telemetry indicates approximately 48,000 appliances globally remain unpatched. Threat actors are chaining these vulnerabilities to establish persistent footholds in corporate networks.
- Sector Risk: Government and Education networks are frequent targets for this type of espionage-focused campaign.
3. WatchGuard Firebox & IoT Risks
- Observation: Security researchers have identified over 54,000 exposed WatchGuard Firebox devices as of mid-November 2025.
- IoT Threat: A new botnet is aggressively recruiting end-of-life GeoVision devices.
- Takeaway: IoT and edge security remains a weak point. Organisations with distributed branches (e.g., Healthcare clinics, retail chains) must audit their perimeter footprint for unmanaged or end-of-life devices.
Sector-Specific Threat Intelligence
- Healthcare: Following the trend of high-impact ransomware attacks (such as the MediSecure incident earlier in the decade), the sector remains a priority target. The new BPH guidance is crucial here—blocking BPH infrastructure can prevent the initial callback of ransomware payloads often used against hospitals.
- Education (EdTech): With the academic year wrapping up, schools and universities are facing increased phishing attempts disguised as administrative notices. The exploitation of Cisco VPN vulnerabilities is a specific vector being used to penetrate university research networks.
- FinTech: A new alert from the ACSC (13 Nov 2025) regarding scammers impersonating police to steal cryptocurrency remains highly relevant. FinTech platforms should warn users about this social engineering tactic, which often involves "urgent" requests to move funds to "safe" wallets.
Penetration Tester’s Perspective
From an offensive security standpoint, the current environment is volatile. Attackers are moving faster than defenders can patch. The FortiWeb bypass (CVE-2025-64446) is particularly dangerous because it compromises the very device meant to secure your web applications.
During our recent engagements, we have observed that API security remains a blind spot. With the rise of AI-driven attacks, automated scripts are now capable of probing APIs for logic flaws much faster than human analysts. Ensure your APIs are not just behind a WAF, but also rigorously tested for Broken Object Level Authorisation (BOLA) and other logic vulnerabilities.
Contact us for a quote for penetration testing service or adversary simulation.

CISA Alert: LANDFALL Spyware Hits Australian BYOD Devices
A zero-click vulnerability, CVE-2025-21042, in millions of Samsung devices is being actively exploited to install "LANDFALL," a commercial-grade spyware. This threat, now on CISA's KEV catalog , transforms an executive's personal device into a silent corporate surveillance tool, completely bypassing your MDM and EDR. For Australian organisations with BYOD policies, this is a critical, reportable data breach scenario under the NDB scheme.
Understanding the Threat: CVE-2025-21042 and the LANDFALL Spyware
For Australian CISOs and IT Directors, the enterprise perimeter no longer ends at the firewall. It ends in the pockets of your C-suite. The recent CISA alert for CVE-2025-21042 has elevated a theoretical risk into an actively exploited reality, with profound implications for Australian businesses.
This isn't a minor consumer-grade bug. This is a supply chain-style compromise of your most trusted, high-value assets: your executive team.
What is CVE-2025-21042?
Tracked as CVE-2025-21042, this is a critical (CVSS 8.8-9.8) out-of-bounds write vulnerability in a core image processing library (libimagecodec.quram.so) on a vast range of high-end Samsung Galaxy devices.
Its primary vector is a "zero-click" exploit. This is the apex predator of vulnerabilities. An attacker simply sends a specially crafted Digital Negative (DNG) image file via a messaging app like WhatsApp. The victim does not need to open the image, click a link, or interact in any way. The device's operating system processes the image preview, triggering the vulnerability and leading to remote code execution (RCE) with system-level privileges.
The Payload: "LANDFALL" Commercial-Grade Spyware
The vulnerability is merely the delivery mechanism. The payload, dubbed "LANDFALL," is a sophisticated, modular, commercial-grade spyware framework engineered for one purpose: total surveillance.
Research from Palo Alto Networks' Unit 42 confirms LANDFALL grants attackers complete control. Its capabilities include:
Audio Surveillance: Recording all microphone audio and phone calls, silently capturing board meetings, legal discussions, and M&A strategy sessions.
Data Exfiltration: Stealing all photos, contacts, SMS messages, and call logs.
Location Tracking: Continuous, real-time monitoring of the victim's movements.
Stealth and Persistence: LANDFALL is designed to evade detection and maintain access even after reboots, giving attackers a persistent foothold.
This toolkit is not the work of common criminals; it's associated with Private-Sector Offensive Actors (PSOAs)—mercenary groups that sell these capabilities to the highest bidder for corporate and state-level espionage.
Business Impact Analysis: The Australian BYOD Liability
This vulnerability was actively exploited for at least seven months (from July 2024 to February 2025) before Samsung's patch in April 2025. On November 10, 2025, CISA added it to the Known Exploited Vulnerabilities (KEV) catalog, mandating a fix by December 1 for federal agencies—a clear signal of its severity and active threat status.
For Australian leaders, this presents a catastrophic governance failure.
Your Executive's Pocket: The New Attack Surface
In Australia, Samsung holds over 25% of the mobile market , with over 9 million users. Many of these are the exact flagship Galaxy S22, S23, S24, and Z Fold devices targeted by this exploit.
In a corporate BYOD (Bring Your Own Device) environment, that personal phone is a trusted endpoint. It is used to check corporate email, access the VPN, join Teams/Zoom calls, and review sensitive documents. When compromised by LANDFALL, that device becomes a vector for a devastating corporate data breach. The ACSC has long warned that BYOD introduces new risks that require careful consideration and risk management, which this exploit directly targets.
A Corporate Data Breach on a Personal Device
The compromise of an executive's phone is not a personal matter. The exfiltration of corporate data (e.g., strategic plans, financial forecasts, client data) from that device is a clear-cut "eligible data breach" under the Office of the Australian Information Commissioner's (OAIC) Notifiable Data Breaches (NDB) scheme.
Your organisation is legally required to assess and report this breach. This introduces severe complications:
Legal Liability: How can you prove what data was not taken? The "employee records exemption" does not apply to the sensitive corporate data, client PII, or market-sensitive information discussed in a board meeting recorded by the spyware.
Reputational Damage: A breach originating from your C-suite's devices signals a fundamental failure of security and governance.
Detection Failure: The most critical question is: How would you even know?
Why Your MDM and EDR Are Blind to This Threat
This is the gap that PSOAs and LANDFALL exploit. Australian CISOs investing in robust security stacks are being failed by a critical blind spot.
Mobile Device Management (MDM): MDM and Unified Endpoint Management (UEM) solutions are governance tools, not security tools. They are designed to enforce policies, push patches, and wipe lost devices. On a BYOD device, their visibility is intentionally limited by employee privacy concerns. An MDM cannot inspect an image parsing library in real-time. It can only (slowly) report if the device is patched, which is useless against a zero-day exploit.
Endpoint Detection & Response (EDR): Your EDR is on the corporate laptop, not the executive's personal phone.
Network Monitoring: The exploit occurs on the device itself. The exfiltrated data is siphoned off over HTTPS on non-standard ports , blending in with thousands of other app connections from a mobile device, making it invisible to traditional network firewalls.
For seven months, this vulnerability was a zero-day. Patching was not an option. Detection was the only possible defence. Your stack was blind, and you were exposed.
How Red Teaming Exposes This Vulnerability
A standard penetration test will check if your external-facing servers are patched. It will not tell you if you could withstand a LANDFALL-style attack.
This threat requires an adversary-centric approach. Our red team engagements move beyond simple vulnerability scanning to simulate the tactics, techniques, and procedures (TTPs) of the PSOAs behind this attack.
Simulating the Mobile-Originated Breach Scenario
We answer the one question your board should be asking: "Can we detect and respond to a zero-click compromise of our executive team?"
A standard pen test checks a list of known vulnerabilities. Our mobile-originated red team engagement simulates the entire attack chain:
Targeted Reconnaissance: We identify high-value targets (e.g., C-suite, finance, legal) and their specific devices, just as a real attacker would.
Adversary Emulation: We emulate the TTPs of an actor like the one deploying LANDFALL, focusing on social engineering vectors and client-side exploits targeting mobile devices.
Payload & Exfiltration: We use a non-destructive, benign payload to simulate a zero-click compromise. The objective is to gain access and begin exfiltrating data.
Testing Your Detection: The real test begins now. Is your SOC blind? Does your SIEM generate an alert? Does your incident response team know how to contain a threat originating from a personal BYOD device? Can they differentiate malicious traffic from the "noise" of 300 other apps?
Our Methodology: Assume You Are Breached
Your MDM will fail to stop a zero-day. Your network perimeter will be bypassed. The battle is one of detection and response.
Our methodology provides the only realistic assessment of your resilience to this modern, mobile-first threat. We provide a clear, actionable report that moves beyond "patch this" and delivers a strategic roadmap for building resilience.
This isn't just about CVE-2025-21042. It's about the next zero-click exploit, and the one after that. Do not wait for a journalist's phone call to find out your most sensitive conversations are being auctioned by mercenaries.
Secure your enterprise. Contact Lean Security today for a confidential Red Team briefing.

Beyond the Patch: Why the Actively Exploited WSUS Vulnerability (CVE-2025-59287) Demands a Red Team Response in Australia
Actively exploited WSUS flaw CVE-2025-59287 (CVSS 9.8) threatens Australian businesses. Patching isn't enough. See why red teaming is essential to validate your security.
I. The Unseen Threat in Your Update Server: A "Keys to the Kingdom" Vulnerability
Within the complex architecture of enterprise security, the Windows Server Update Service (WSUS) stands as a ubiquitous and fundamentally trusted component. It is the silent workhorse operating in the background, the central nervous system for patch management, ensuring that thousands of endpoints receive the critical security updates necessary to maintain cyber hygiene and defend against an ever-evolving threat landscape. Organisations across Australia and the globe depend on its reliable function to close vulnerabilities and fortify their digital estates. This report, however, addresses a critical and alarming scenario: what happens when this trusted defender becomes the ultimate insider threat?
The emergence of CVE-2025-59287 represents not merely another software flaw, but a fundamental breach of the trust relationship between an organisation's security posture and its core management tools. An adversary who gains control over a WSUS server does not just compromise a single machine; they seize the "keys to the kingdom." They command the very mechanism responsible for distributing security and integrity across the network. This privileged position allows an attacker to turn the entire update infrastructure into a weapon, capable of deploying malicious code disguised as legitimate patches to any and every connected system. The psychological impact of such a compromise on security teams is profound. It weaponizes a tool they rely upon for defence, forcing them into a state where their own infrastructure must be treated with suspicion. This erosion of trust complicates every facet of incident response and recovery, handing a significant advantage to the adversary before the battle has even begun.
The threat posed by CVE-2025-59287—a critical, remotely exploitable, unauthenticated vulnerability now being actively used by attackers—is therefore not a problem to be delegated solely to system administrators. Its potential for catastrophic business disruption, from widespread ransomware deployment to silent espionage, elevates it to a strategic risk that demands the immediate attention of technical and business leadership. This analysis will deconstruct the vulnerability, trace its alarming evolution from a flawed patch to a weaponized exploit, and argue that for Australian organisations, the only path to true resilience lies beyond reactive patching and in the realm of proactive, adversary-emulation-based security validation.
II. Deconstructing CVE-2025-59287: The Anatomy of a Critical Flaw
To fully grasp the severity of CVE-2025-59287, it is essential to understand both the role of WSUS in a typical enterprise environment and the precise technical mechanics of the vulnerability itself.
WSUS Architecture in the Enterprise
WSUS operates on a hierarchical model. A central "Upstream Server" connects to Microsoft's update servers over the internet to download patches. Internal "Downstream Servers" then connect to this upstream server to receive and distribute those patches to client workstations and servers within the local network. This architecture is designed for efficiency and control, but it creates a powerful central point of distribution. A compromise of the upstream server can have a cascading effect, potentially compromising every downstream server and, by extension, every client they manage. This structure makes WSUS an incredibly attractive target for adversaries seeking to bypass network segmentation and achieve widespread lateral movement.
Technical Deep Dive
The vulnerability is rooted in a classic but severe software security flaw known as "Deserialization of Untrusted Data," catalogued as CWE-502. The attack unfolds through a precise sequence of events targeting the WSUS reporting web services:
The Attack Vector: A remote, unauthenticated attacker sends a specially crafted network request to the WSUS server. This request targets the
GetCookie()endpoint and contains a maliciousAuthorizationCookieobject.The Mechanism: The WSUS server receives this malicious cookie. It proceeds to decrypt the cookie's data using an AES-128-CBC cipher and then deserializes the resulting object using the
BinaryFormattermethod. The critical failure occurs here: the server performs this deserialization without properly validating that the resulting data is safe or of an expected type.The Result: By providing a malicious object, the attacker tricks the server into executing arbitrary code in the context of the WSUS service, which typically runs with high-level SYSTEM privileges.
This exploit is particularly egregious because Microsoft itself has long deprecated the use of BinaryFormatter, explicitly warning developers that the method is inherently unsafe when used with untrusted input due to its inability to prevent this exact type of attack. Its continued presence in a critical, internet-facing component represents a significant and exploitable engineering oversight.
Quantifying the Risk
The technical details translate into a risk profile that represents a worst-case scenario for a network-based vulnerability. The Common Vulnerability Scoring System (CVSS) provides a clear, data-driven assessment of its severity.

CVE-2025-59287
The CVSS vector string is particularly telling for technical leaders:
Attack Vector: Network (AV:N): The vulnerability can be exploited remotely over a network.
Attack Complexity: Low (AC:L): It requires no special conditions or complex techniques to exploit.
Privileges Required: None (PR:N): The attacker does not need any credentials or prior access.
User Interaction: None (UI:N): The attack requires no action from a user, such as clicking a link or opening a file.
Impact: High (C:H, I:H, A:H): Successful exploitation leads to a complete loss of Confidentiality, Integrity, and Availability of the targeted WSUS server.
This combination confirms that CVE-2025-59287 is a remotely executable, unauthenticated, and trivial-to-exploit vulnerability that results in a full system compromise.
III. A Timeline of Crisis: From Flawed Patch to Active Exploitation
The story of CVE-2025-59287 is not just one of a critical vulnerability, but also a case study in the dangers of a flawed patching process and the rapid pace at which modern threats evolve. The timeline of events created a critical window of exposure, leaving even diligent organisations vulnerable.
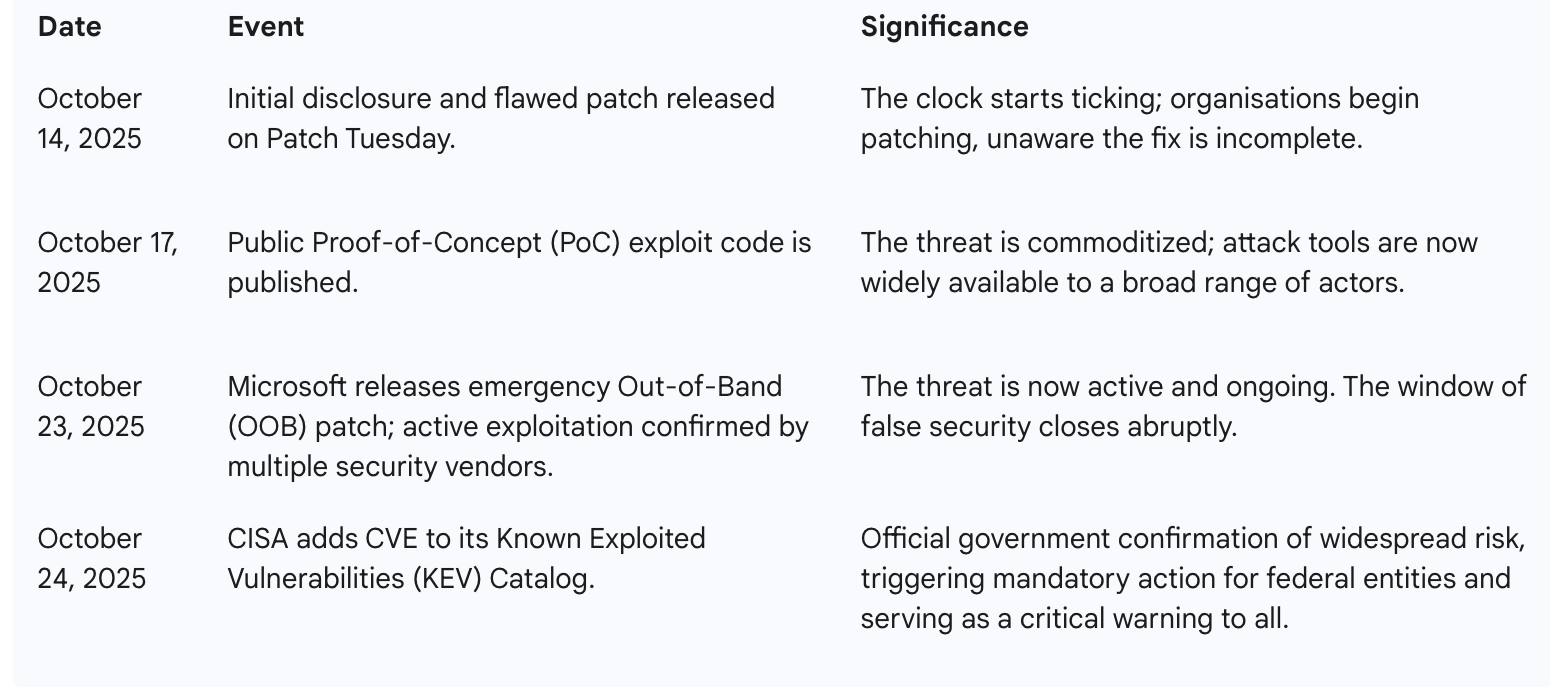
CVE-2025-59287 timeline
Official government confirmation of widespread risk, triggering mandatory action for federal entities and serving as a critical warning to all.
This sequence of events powerfully illustrates the "patching paradox" and the inherent weakness of a purely compliance-centric security model. An organisation that prides itself on its key performance indicators for patch deployment—for instance, applying all critical patches within a 14-day window—would have acted promptly after the October 14th Patch Tuesday. They would have deployed the initial update, and their vulnerability scanners and compliance reports would have marked CVE-2025-59287 as "remediated."
However, because that initial patch was incomplete, this state of compliance was a dangerous illusion. The organisation was, in fact, still completely vulnerable. The period between October 14 and the release of the emergency patch on October 23 was a window of false security. During this time, the publication of a PoC exploit on October 17 dramatically lowered the technical barrier for attackers.8 When active exploitation began on October 23, these "compliant" organisations were just as exposed as those who had not patched at all.
This real-world failure demonstrates that security cannot be measured by checklists or the speed of patch deployment alone. True security is not a theoretical state of compliance but an empirically validated state of resilience. It proves that mitigating controls must be tested to confirm they are actually effective, not just present. Without this validation, organisations are operating on faith—a faith that, in this case, was misplaced, leaving them exposed to a critical, actively exploited threat.
IV. The Attacker's Playbook: How CVE-2025-59287 is Being Weaponised
The theoretical risk of CVE-2025-59287 rapidly became a practical reality. Security researchers observed attackers exploiting the vulnerability in the wild, providing a clear view of their initial tactics and objectives.
In-the-Wild Exploitation
Initial reports from security firms like Huntress described the attacks as simple "point-and-shoot" techniques, underscoring the low complexity of the exploit following the release of the PoC. The observed post-exploitation activity focused on immediate reconnaissance. Attackers, having gained SYSTEM-level access on the WSUS server, were seen spawning Command Prompt and PowerShell processes directly from the IIS worker process (w3wp.exe) or the WSUS service binary (wsusservice.exe).
They executed basic commands to map the compromised environment, such as net user /domain to enumerate all user accounts in the Active Directory domain, and ipconfig /all to gather detailed network configuration data.1 The output of these commands was then exfiltrated to an attacker-controlled remote server.1 This behaviour is a clear indicator that attackers are using the initial WSUS compromise as a beachhead to understand the network's structure, identify high-value targets, and plan their next move.
The Red Team Perspective: Simulating the Full Attack Chain
While the observed attacks focused on reconnaissance, a sophisticated adversary—or a red team emulating one—would leverage the unique position of a compromised WSUS server to execute a far more devastating attack chain. The strategic goal is not just to compromise the WSUS server itself, but to use it as a master key to unlock the entire network. This is accomplished by abusing the core functionality of WSUS for lateral movement, a technique well-documented by offensive security researchers and encapsulated in tools like SharpWSUS.
The full attack chain would proceed as follows:
Initial Compromise: The attacker gains their initial foothold by exploiting CVE-2025-59287, achieving remote code execution with SYSTEM privileges on the primary WSUS server.
Internal Reconnaissance and Target Identification: From the compromised server, the attacker enumerates all computers managed by WSUS. This provides a comprehensive list of potential targets across the network, including domain controllers, database servers, and critical application hosts.
Target Isolation: To avoid detection and collateral damage, the attacker creates a new, innocuous-sounding update group on the WSUS server (e.g., "Critical Server Patching Pilot"). They then move their high-value target, such as a domain controller, into this isolated group.3
Malicious Update Creation: The attacker crafts a malicious "update" package. A key constraint of this technique is that the payload must be a legitimate, Microsoft-signed binary to avoid suspicion. However, this is a low hurdle, as numerous signed binaries can be used for malicious purposes (a technique known as Living-off-the-Land). The attacker can use a tool like
PsExec.exeorMsiExec.exeto execute a secondary payload, such as a command to create a new administrative user or deploy ransomware.Deployment and Execution: The attacker approves this malicious update for deployment only to the isolated group containing the high-value target. They then simply wait for the target machine's scheduled check-in time. When the domain controller connects to WSUS to request updates, it will download and execute the malicious package, believing it to be a legitimate patch from a trusted internal source.
The strategic impact of this attack path cannot be overstated. Modern network security is built on the principle of segmentation—separating critical assets into protected zones to contain breaches. However, WSUS, by its very nature, is designed to traverse these segments. Firewall rules are almost always configured to allow clients from all network zones to communicate with the central WSUS server on ports 8530 and 8531. An attacker who controls the WSUS server inherits this privileged network position. They can use the trusted WSUS protocol as a covert channel to push malicious code into otherwise inaccessible, highly secured network segments, rendering years of segmentation efforts completely useless. The WSUS server becomes a network chokepoint, where a single point of failure leads to the systemic compromise of the entire enterprise.
V. The Australian Imperative: Placing the WSUS Threat in Local Context
While CVE-2025-59287 is a global threat, its implications are particularly acute within the Australian cybersecurity landscape, which is characterized by increasing attacks and a stringent regulatory environment for critical infrastructure.
Connecting to the National Threat Landscape
The Australian Signals Directorate's (ASD) Australian Cyber Security Centre (ACSC) Annual Cyber Threat Report 2024-25 paints a stark picture of the environment in which Australian organisations operate. The report highlights a staggering 83% increase in notifications of potentially malicious cyber activity issued by the ACSC. It underscores the persistent and growing threat from both state-sponsored actors and sophisticated cybercriminals who are relentlessly targeting Australian governments, businesses, and critical infrastructure.13
Crucially, the report identifies "compromised assets, networks, or infrastructure" as the most frequently reported type of cybersecurity incident, accounting for 55% of incidents affecting critical infrastructure. The exploitation of CVE-2025-59287 aligns perfectly with this trend, providing adversaries with a direct and highly effective method for achieving widespread network compromise. The ability to gain control of a central management tool like WSUS is precisely the kind of high-impact capability that these threat actors seek.
Implications for Critical Infrastructure (SOCI Act)
For the growing number of Australian organisations governed by the Security of Critical Infrastructure (SOCI) Act 2018, this vulnerability poses a direct and significant challenge to their compliance and operational resilience obligations. The SOCI Act mandates that responsible entities establish and maintain a risk management program (RMP) that identifies and mitigates hazards, including cyber threats and supply chain vulnerabilities.
A vulnerability in a foundational software distribution platform like WSUS must be viewed as a critical software supply chain risk. An attacker who compromises WSUS can disrupt the integrity of the entire software update process, which is a cornerstone of cyber defence. For operators of essential services—in sectors like energy, healthcare, communications, and finance—a compromised WSUS server could be used to deploy disruptive malware, leading to significant operational downtime, service outages, and a clear failure to meet SOCI Act obligations. For entities responsible for Systems of National Significance (SoNS), the threat is even more severe. An adversary could use a compromised WSUS server to gain persistent access to the nation's most vital assets, directly threatening Australia's economic stability and national security.
This context transforms the WSUS vulnerability from a mere technical issue into a potential tool for "grey zone" warfare. The ACSC has explicitly warned that state-sponsored actors are actively working to position themselves for potential disruptive attacks at times of strategic advantage. A compromised WSUS server is the perfect vector for such an operation. An adversary could use it to deploy a dormant payload—such as a logic bomb, a wiper, or a persistent backdoor—disguised as a routine update. This malicious capability could be pre-positioned across an entire critical infrastructure network, remaining latent and undetected until activated. This scenario moves beyond data theft and cybercrime into the realm of national resilience and sovereignty, aligning directly with the most serious threats identified by the ASD.
VI. Your Strategic Response: Moving from Reactive Patching to Proactive Defence
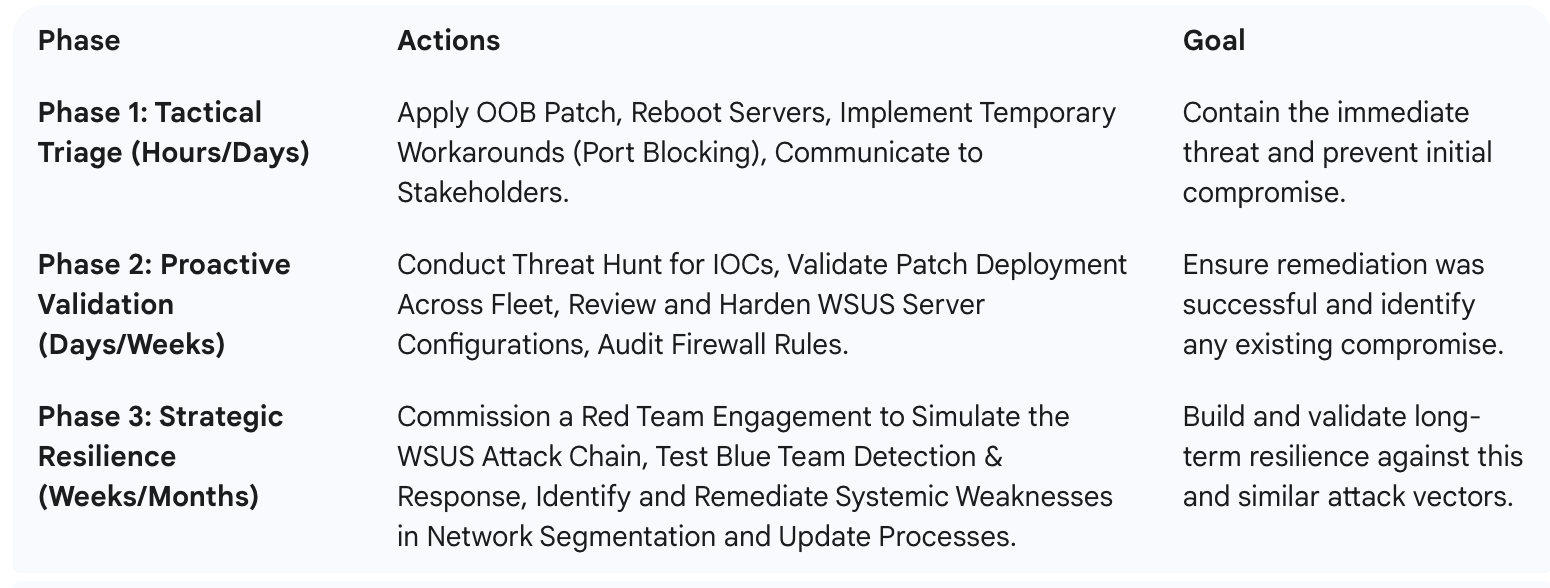
A threat of this magnitude requires a response that is layered, disciplined, and extends beyond immediate remediation. A comprehensive strategy must move from tactical triage to proactive validation and, ultimately, to the strategic resilience that can only be achieved through adversarial emulation.
Layer 1: Immediate Tactical Mitigation (The "Stop the Bleeding" Phase)
This phase is about immediate, decisive action to contain the threat, based on the official guidance from Microsoft and CISA. These steps are non-negotiable and must be treated with the highest priority.
Action 1: Patch Immediately. Apply the correct out-of-band (OOB) security update to all affected Windows Server versions. The relevant updates include KB5070881, KB5070882, KB5070883, KB5070884, and others corresponding to specific server versions. This OOB update supersedes the flawed patch from the October 14th Patch Tuesday.
Action 2: Reboot. A system reboot is required after the patch is installed to ensure the mitigation is fully applied and the system is protected.
Action 3: Use Workarounds if Patching is Delayed. In situations where immediate patching is not feasible due to operational constraints, Microsoft has provided temporary workarounds. These include completely disabling the WSUS Server Role on the affected server or, more surgically, blocking all inbound traffic to TCP ports 8530 and 8531 at the host firewall.1 It is critical to understand that these actions will render the WSUS server non-operational, preventing clients from receiving any updates.
Layer 2: Proactive Security Validation (The "Confirm and Harden" Phase)
Completing the tactical mitigation is only the first step. The "patch and pray" approach is insufficient given the active exploitation of this vulnerability. Technical leaders must challenge their teams with the critical follow-up question: "How do we know we are truly safe?"
Action 4: Hunt for Compromise. Operate under the assumption of a breach. Security teams must proactively hunt for Indicators of Compromise (IOCs) related to the observed in-the-wild attacks. This includes searching logs for suspicious PowerShell or Command Prompt execution originating from the
w3wp.exeorwsusservice.exeprocesses, and analyzing network traffic for unusual outbound connections from WSUS servers to unknown domains.1Action 5: Validate Patch Deployment and Configuration. Use vulnerability management and asset inventory systems to confirm that the correct OOB patch has been successfully deployed across the entire fleet of WSUS servers. This is also the time to conduct a thorough configuration review of all WSUS servers, ensuring that management access is restricted to trusted administrative networks and that host firewall rules are hardened to minimize the attack surface.
Layer 3: Adversary Emulation (The "Build True Resilience" Phase)
This is the most critical phase for achieving long-term, verifiable security. The only way to be certain that defences can withstand a sophisticated, multi-stage attack leveraging a compromised WSUS server is to simulate that exact attack in a controlled, objective-driven manner.
Action 6: Commission a Red Team Engagement. A specialized red team engagement provides empirical evidence of an organisation's security posture against this real-world threat.19 Such an exercise would not stop at a simple vulnerability scan. It would simulate the adversary's complete playbook, including:
Attempting to validate the patch's effectiveness against the known exploit for CVE-2025-59287.
Executing the post-exploitation tactics, techniques, and procedures (TTPs), specifically emulating the abuse of WSUS for lateral movement as described in the SharpWSUS methodology.
Testing the Security Operations Centre's (SOC) and blue team's ability to detect and respond to the specific artifacts of this attack, such as the creation of suspicious update groups, the deployment of non-standard update packages, or the presence of unexpected signed binaries in the WSUS content directory.
This process moves security from a theoretical state based on compliance to an empirically tested reality. It provides leadership with genuine, evidence-based confidence in their organisation's resilience against the threats they are most likely to face.
Adversary Emulation phases
VII. Executive Briefing: Key Actions for Australian Business Leaders
The critical vulnerability in the Windows Server Update Service, CVE-2025-59287, represents a clear and present danger to Australian organisations. This is not a routine security flaw; it is a strategic risk that weaponizes a core IT management asset, turning a trusted defender into a potential single point of catastrophic failure. Active exploitation in the wild, combined with a CVSS score of 9.8, necessitates an urgent and comprehensive response that goes beyond standard patching protocols. For business and technical leaders, the following actions are imperative.
Acknowledge the Severity: Recognise that CVE-2025-59287 is a critical, actively exploited threat that fundamentally undermines the trust in your core IT infrastructure. Direct your teams to treat this with the highest level of urgency.
Mandate Immediate and Correct Patching: Instruct your technical teams to apply Microsoft's specific emergency out-of-band patch for CVE-2025-59287 across all WSUS instances without delay. Ensure they understand that the initial October 14th patch was insufficient and must be superseded.
Question Your Assumptions: Move beyond a compliance mindset. The critical question is not simply "Did we patch?" but "How have we validated that the patch is effective and that no prior compromise occurred?" Demand evidence of proactive threat hunting and configuration validation.
Invest in Adversarial Validation: The weaponization of trusted infrastructure is a hallmark of sophisticated attacks. The only way to truly know if your defences, detection capabilities, and response procedures can withstand this attack is to test them. Commission an independent penetration test or red team engagement focused specifically on simulating this attack chain to gain empirical evidence of your organisation's security posture.
Review Your SOCI Act Obligations: If your organisation is a critical infrastructure operator under the SOCI Act, this vulnerability has direct implications for your mandated risk management program. Engage with your compliance and security teams to review how this software supply chain threat impacts your operational resilience and ensure your mitigation strategies are sufficient to meet your legal and regulatory obligations.

APIs Under Attack: Why Your Digital Core Needs Penetration Testing
API penetration testing helps Australian businesses protect sensitive data and strengthen resilience by identifying hidden weaknesses before attackers strike.
Every business today relies on digital connections. Applications share data, mobile services link to platforms, and cloud environments run operations. At the centre of this ecosystem are Application Programming Interfaces (APIs). They act as the channels through which your systems exchange data and deliver value to customers.
While APIs have become indispensable, they have also become attractive targets for attackers. They manage sensitive customer information, business transactions, and backend processes. A single weak API can act as a direct gateway into your most valuable systems. This risk makes API penetration testing one of the most important defences for modern organisations.
Why APIs Have Become Targets
Attackers are always looking for weaknesses. APIs provide them with opportunities because they are exposed, widely used, and often complex. In Australia, the Australian Cyber Security Centre (ACSC) receives thousands of incident reports each year, many of which involve applications or data breaches. APIs are often the underlying cause.
Some common reasons APIs attract attacks include:
● Data concentration: APIs often transmit sensitive customer data.
● Rapid integration: New features and third-party services are constantly added, increasing complexity.
● Misconfiguration: Poor authentication or access controls allow unauthorised entry.
● Lack of visibility: Many organisations underestimate how many APIs they have in operation.
This combination makes APIs the perfect target. Without structured testing, vulnerabilities remain hidden until exploited.
What is API Penetration Testing?
API penetration testing is the practice of simulating real-world attacks on your APIs to identify vulnerabilities before criminals can use them. It goes beyond automated scans. Skilled testers apply both tools and manual analysis to replicate the techniques attackers would use.
During testing, specialists attempt to:
● Break authentication and authorisation systems.
● Inject malicious input into endpoints.
● Exploit weak encryption or insecure communications.
● Chain small flaws across endpoints to create larger breaches.
The result is a clear picture of how secure your APIs truly are. Instead of relying on assumptions or surface-level checks, you receive evidence-based findings with practical steps for remediation.
Common API Weaknesses

APIs fail for many reasons, but testing frequently identifies the same categories of weaknesses:
Broken Authentication
When login processes are misconfigured, attackers may gain access with little resistance. Weak session handling, missing tokens, or default passwords are common errors.
Insecure Data Transmission
Unencrypted traffic allows attackers to intercept sensitive data. APIs that fail to use secure protocols expose customer and business information in transit.
Excessive Data Exposure
Poorly designed endpoints may return more data than required. Attackers can request additional fields, gaining access to confidential records.
Lack of Rate Limiting
APIs that do not restrict request volumes allow attackers to flood systems or attempt brute-force attacks without resistance.
Improper Error Handling
Detailed error messages may reveal database structures or configuration details. Attackers can use this information to refine their attacks.
Each weakness alone may appear minor. Together, they provide attackers with a path to compromise your systems.
How API Penetration Testing is Performed
The process of API penetration testing follows a structured approach designed to provide clarity, safety, and measurable results.
Scoping
The first step defines what will be tested. This includes identifying the APIs, the level of access provided, and the objectives.
Reconnaissance
Testers map the API, reviewing documentation, endpoints, and parameters. This creates a blueprint of how the system functions.
Exploitation
Simulated attacks are performed against authentication, input handling, and data processes. Testers attempt to exploit flaws in the same way an attacker would.
Post-Exploitation
If access is gained, testers assess how deep the compromise can go. This stage demonstrates the potential impact on business operations.
Reporting
You receive a plain-English report that explains each issue, its risk rating, and steps for remediation. The report is not only technical but also tied to business consequences.
Why Automated Scans Fall Short
Automated tools have value, but they are not enough. Scanners may identify obvious issues, but they cannot understand business logic or exploit chained vulnerabilities.
For example, a scanner may report missing input validation. Only human-led testing can demonstrate how this flaw allows attackers to bypass authorisation and extract entire customer datasets. API penetration testing bridges this gap by combining automation with expertise.
The Business Impact of API Security
Weak APIs do not only represent technical problems, but they also affect your entire business.
● Reputation: Customers lose trust when their data is exposed.
● Financial loss: Breaches may lead to compensation costs, downtime, and recovery expenses.
● Compliance: Failure to protect data may result in fines under Australian regulations.
● Operations: Attacks that disrupt APIs can bring core services to a halt.
Testing provides visibility over these risks. By identifying weaknesses early, you control the narrative, not the attacker.
Benefits of Regular Testing
The value of API penetration testing is not just in identifying vulnerabilities but in strengthening your long-term security posture. Regular testing allows you to:
● Detect new weaknesses introduced by updates or integrations.
● Verify that previous issues have been remediated.
● Provide assurance to customers, investors, and regulators.
● Support continuous improvement in your security program.
In short, testing becomes part of your ongoing defence strategy, rather than a one-time project.
Why Australian Businesses Should Act Now

Cybercrime in Australia is growing in scale and cost. The ACSC reported an average of one cybercrime incident every six minutes in 2023–24. With APIs driving mobile apps, e-commerce platforms, and other services, attackers are increasingly targeting them.
Businesses that delay testing place themselves at unnecessary risk. By investing in API penetration testing, you protect customer trust and demonstrate responsible governance. In a competitive environment, security becomes not only a defence but a market differentiator.
Building Security into Strategy
Your APIs will continue to grow in number and complexity as your business expands. Each new service, integration, or mobile application adds more endpoints. Security must grow alongside this expansion.
Embedding API penetration testing into your development cycle helps detect weaknesses before they reach production. This reduces remediation costs and prevents incidents that damage your reputation.
Security is not a barrier to innovation. It is the foundation that allows you to innovate with confidence. Strong security practices also build trust with stakeholders, strengthen compliance efforts, and provide long-term resilience. By maintaining a consistent testing program, you create stability across your technology environment. Ultimately, protecting APIs becomes a continuous process that supports both business growth and digital reliability.
Lean Security: Your Partner in API Protection
APIs are your digital core, and their protection requires more than automated scans. Regular API penetration testing helps safeguard your systems, customer trust, and compliance position. By combining network penetration testing, mobile application security testing, managed internal vulnerability scanning, and broader web security testing, you build a resilient defence against real-world threats.
As a Sydney-based penetration testing company, Lean Security delivers more than reports. We provide human-led testing, clear explanations, and actionable solutions. Our team specialises in penetration testing methods, application security testing, web security audit, and advanced services.
Contact Lean Security to discuss how our penetration testing company can protect your APIs, applications, and networks.

IT Security Audit Services: Turning Compliance into a Competitive Advantage
IT security audit services help Australian businesses build trust, credibility, and compliance. See how audits strengthen reputation and provide lasting business advantage.
In a digital-first economy, customers, regulators, and investors expect organisations to guard sensitive data. Compliance obligations in Australia are strict, with frameworks such as the Privacy Act 1988 and the Notifiable Data Breaches (NDB) scheme, as well as industry-specific rules, including APRA CPS 234, for financial institutions. While these regulations set minimum requirements, many businesses still see compliance as a burden.
In reality, IT security audit services are more than a checklist. They are a tool for building customer trust, protecting brand reputation, and creating a competitive edge. By turning compliance into a strength, businesses can position themselves as reliable, transparent, and security-focused in a crowded market.
What IT Security Audits Involve
IT security audit services evaluate your organisation’s technology, policies, and processes against industry standards and regulatory frameworks. In Australia, this often includes alignment with ISO/IEC 27001, PCI DSS, and the Australian Government’s Information Security Manual (ISM).
A security audit checks:
● Access controls and identity management
● Network and system configurations
● Incident response procedures
● Encryption standards and data handling policies
● Vendor and third-party risk management
● Compliance with Australian data protection requirements
Audits are not only about identifying gaps. They also provide recommendations to improve resilience and demonstrate to stakeholders that you are serious about security.
Compliance as the Starting Point
Regulatory compliance is mandatory for many Australian organisations. Financial firms must adhere to APRA CPS 234, while healthcare providers face obligations under the My Health Records Act. Retailers handling credit card payments must follow PCI DSS.
IT security audit services provide documented proof that compliance obligations are being met. For example, PCI DSS audits verify whether your systems handle payment data securely. This reduces the risk of penalties, legal issues, or reputational harm from breaches.
But compliance alone does not guarantee safety. Audits that go beyond minimum requirements help organisations prepare for threats that regulations may not fully address.
Why Australian Businesses Should Treat Audits as a Strategic Investment
1. Building Customer Trust
Australians are increasingly concerned about privacy. According to the Office of the Australian Information Commissioner (OAIC), privacy complaints and data breach notifications have risen steadily in recent years. Customers want assurance that their data is handled responsibly.
By using IT security audit services, you send a clear message: protecting data is a priority. This transparency builds trust and can directly influence customer loyalty and retention. Strong privacy protection through regular audits also shows regulators and partners that your organisation respects national compliance standards. This strengthens your position in the market.
2. Strengthening Business Credibility
Audits provide evidence of security maturity. Displaying compliance with standards like ISO/IEC 27001 or PCI DSS can differentiate your business from competitors. In industries where contracts depend on supplier security posture, such as government procurement or large enterprise supply chains, passing an audit can be the deciding factor in winning work. When your audit results are presented clearly, they become a business credential that demonstrates reliability and professionalism to customers and stakeholders alike.
3. Reducing Business Risks
Audits help identify weaknesses before attackers do. For example, infrastructure vulnerability scanning and managed internal vulnerability scanning are often part of audit processes. They detect misconfigurations or outdated software that criminals could exploit. Fixing these issues early reduces the risk of costly breaches. This limits downtime, reduces incident response costs, and prevents reputational damage that could otherwise impact customer trust and business continuity.
Types of Audits and Security Assessments

Australian businesses can access different types of audits depending on their industry and risks.
● Web security audit: Evaluates websites and applications for weaknesses like injection flaws or insecure authentication.
● Application security testing: Reviews both web and mobile applications, ensuring they are resistant to attacks. This includes mobile application security testing.
● Network penetration testing: Simulates an attacker trying to break into company networks. It assesses how well defences hold up under real-world attacks.
● Web application penetration testing: Focuses on critical customer-facing platforms. This often involves a web application scanner and manual testing by experts.
● Source code security assessment in the cloud: Reviews code for hidden flaws in applications hosted on AWS, Azure, or GCP.
These assessments go beyond compliance. They show whether your security controls work in practice.
IT Security Audits and Managed Services
Many Australian firms combine audits with managed security services for ongoing protection. A one-off audit provides a snapshot, but risks change constantly. New vulnerabilities appear daily, and attackers adapt their methods.
By partnering with a managed services provider, businesses can complement audits with:
● Managed web vulnerability scanning to track new threats
● Managed network services for secure connectivity
● Continuous vulnerability scanning service that detects risks in real time
This combination allows businesses to prove compliance and maintain a strong defence long after the audit ends.
Audits as a Tool for Continuous Improvement
An audit report is not just a certificate. It is a guide for improvement. The recommendations may include:
● Updating authentication methods
● Implementing stronger encryption
● Conducting regular risk assessment
● Adopting security testing techniques that simulate attacker behaviour
Organisations that treat audit reports as a roadmap for progress see long-term benefits. They improve resilience, avoid repeated incidents, and create a culture where security is part of everyday operations.
Turning Compliance into Competitive Advantage
The Australian market is competitive across industries. From financial services to healthcare, customers and partners have choices. Security can be a deciding factor.
For example:
● A retailer that demonstrates strong website security testing will win more consumer trust than one that barely meets compliance.
● A software provider offering web security testing and proof of regular web security scanning will be more attractive to enterprise buyers.
● A financial services firm that invests in managed security testing can prove to regulators and clients that it takes its obligations seriously.
Audits provide the evidence needed to showcase these strengths. By embedding security into brand identity, compliance becomes a competitive asset, not just a requirement.
How to Select the Right Audit Partner in Australia

When choosing a partner for IT security audit services, look for:
1. Local expertise: A provider based in Australia understands local compliance requirements and threat conditions.
2. Certified professionals: Certifications such as CREST, OSCP, and CISSP demonstrate capability.
3. Manual and automated testing: Automated tools like a vulnerability scanner are helpful, but manual analysis is needed to catch complex flaws.
4. Clear reporting: The best audit partners deliver findings in plain English, not technical jargon.
5. Ongoing support: Beyond the audit, support with remediation strengthens outcomes.
Sydney-based firms like Lean Security combine these elements, offering a partnership that prioritises clarity, results, and trust.
Trust Lean Security for Lasting Business Credibility
At Lean Security, we believe that compliance should be more than a box-ticking exercise. With the right approach, IT security audit services become a foundation for credibility and competitive strength. By combining audits with advanced testing, organisations protect their reputation, satisfy regulators, and build lasting trust with customers.
Our Sydney-based team of experts conducts penetration testing to simulate real-world attacks. As one of the trusted penetration testing companies in Australia, we also provide application security testing, web application penetration testing, and infrastructure vulnerability scanning services.
Contact us today to discuss how our auditing and testing services can help your organisation turn compliance into a competitive advantage!