

Managed Internal Vulnerability Scanning: Your Business’s First Line of Defence Against Insider Threats
Discover how managed internal vulnerability scanning protects your business from insider threats by detecting weaknesses before attackers exploit them.
When most businesses think of cyber threats, they imagine external hackers trying to break through firewalls or exploit weak passwords. But what about the risks that come from inside your organisation? Insider threats, whether from careless employees, misconfigured systems, or malicious actors with access to your network, often pose the most immediate danger.
This is where managed internal vulnerability scanning(MIVS) comes in. Acting as your business’s first line of defence, internal scans detect weaknesses from within before attackers can exploit them. By identifying misconfigurations, outdated software, and overlooked security gaps, MIVS helps companies strengthen their defences proactively rather than waiting for a costly breach.
Let’s break down why internal vulnerability scanning is essential, common mistakes businesses make without it, and how it protects your organisation from insider-driven risks.
1. Understanding Insider Threats: The Hidden Risk Within
External attacks make the headlines, but insider threats are equally dangerous. These risks often come from:
· Negligent employees who click on phishing links or reuse weak passwords.
· Misconfigured systems that grant more access than intended.
· Disgruntled staff who intentionally misuse their privileges.
Without proper scanning, these vulnerabilities go unnoticed until it’s too late. Managed internal vulnerability scanning provides visibility where it matters most — inside your walls.
2. What Is Managed Internal Vulnerability Scanning?
MIVS is an automated, continuous process where internal systems are scanned for weaknesses. Unlike traditional penetration tests that simulate external attacks, MIVS focuses on threats that arise from inside the organisation.
It identifies:
· Weak or misconfigured user accounts.
· Outdated software and unpatched systems.
· Poorly secured endpoints and devices.
· Access rights that don’t align with business needs.
By managing this process for you, a trusted security partner ensures vulnerabilities are flagged, reported, and remediated before insiders or attackers can exploit them.
3. Why Internal Scanning Matters More Than Ever
Today’s businesses operate in complex environments, like hybrid workplaces, cloud-based platforms, and distributed teams. This opens up more internal vulnerabilities than ever before.
Key reasons internal scanning is vital:
Remote Work Expansion: Employees accessing corporate systems from unsecured home networks create new risks.
Cloud Growth: Misconfigured cloud storage or permissions often go undetected.
Third-Party Access: Vendors, contractors, and partners often have more access than they need.
Internal vulnerability scanning provides a safety net against these risks, ensuring you don’t overlook the weak points inside your ecosystem.
4. Common Vulnerabilities Found Through Internal Scans
You might think your systems are secure until an internal scan reveals otherwise. Some of the most common issues discovered include:
· Unpatched software vulnerabilities left open for months.
· Excessive user privileges that allow employees to access data they don’t need.
· Shadow IT — devices or applications installed without IT’s knowledge.
· Weak internal passwords reused across multiple systems.
· Misconfigured firewalls and access points that expose sensitive data.
Each of these vulnerabilities is a potential doorway for insider threats or external attackers who gain access through stolen credentials.
5. The Role of Managed Services in Vulnerability Scanning
While businesses can attempt internal scans themselves, managing the process in-house is resource-intensive and often inconsistent. That’s why outsourcing to a managed internal vulnerability scanning provider makes sense.
Managed services bring:
Expertise: Security professionals know what to look for and how to interpret results.
Consistency: Scans are run on schedule without relying on stretched IT staff.
Actionable Reporting: Instead of a long technical report, you get clear remediation steps.
Proactive Alerts: Vulnerabilities are flagged as soon as they appear.
This ensures nothing slips through the cracks, even as your IT environment evolves.
6. How Internal Scanning Fits into Your Security Strategy
MIVS is not a standalone solution — it works best as part of a broader cybersecurity framework. Together with:
· Penetration Testing for simulating real-world attacks.
· Endpoint Security to safeguard devices.
· Network Monitoring for real-time threat detection.
· Employee Training to reduce human error.
Internal vulnerability scanning provides the visibility you need to patch weak points before they’re exploited.
7. The Cost of Ignoring Internal Scanning
What happens if you overlook internal vulnerabilities? The risks are costly:
Data Breaches: Sensitive data falls into the wrong hands.
Regulatory Fines: Non-compliance with standards like GDPR, HIPAA, or PCI DSS.
Operational Disruption: Insider threats can halt operations, costing thousands per day.
Reputation Damage: Clients and partners lose trust after a breach.
The cost of proactive scanning is far less than the fallout from ignoring insider threats.
8. Best Practices for Effective Internal Vulnerability Scanning
To get the most out of MIVS, businesses should:
Schedule Regular Scans — vulnerabilities change as systems evolve.
Prioritise Risks — not all vulnerabilities pose equal danger. Focus on high-impact issues first.
Integrate With Patch Management — quickly update software and systems after scans.
Review User Access — reduce unnecessary privileges to limit insider threats.
Partner With Specialists — a managed provider ensures accuracy and consistency.
When done right, internal vulnerability scanning becomes a proactive shield against insider-driven risks.
9. How Lean Security Helps
At Lean Security, we specialise in helping organisations uncover and remediate hidden vulnerabilities before they turn into costly breaches. Our managed internal vulnerability scanning service is designed to:
· Provide continuous, automated detection of internal weaknesses.
· Deliver clear, actionable reports your team can act on immediately.
· Ensure compliance with industry regulations and standards.
· Reduce the burden on in-house IT staff.
By combining cutting-edge scanning tools with expert guidance, we give businesses the confidence that their internal security posture is strong and resilient.
10. Future-Proofing Against Insider Threats
Cybersecurity threats evolve, but insider risks remain constant. Whether caused by error, neglect, or malicious intent, they can only be mitigated with proactive detection. Managed internal vulnerability scanning ensures your business is never blindsided by weaknesses hidden in plain sight.
The best defence against insider threats isn’t reacting after the damage is done — it’s preventing them altogether.
Choose Lean Security
Don’t leave your organisation exposed to insider threats and overlooked vulnerabilities. At Lean Security, we make internal protection simple, effective, and proactive with our managed internal vulnerability scanning service. By continuously monitoring your internal systems, identifying hidden weaknesses, and providing clear remediation strategies, we help you prevent insider-driven risks before they escalate.
Whether you’re aiming to stay compliant, protect sensitive data, or safeguard your reputation, our penetration testing company gives you the tools and expertise to stay ahead of threats. Strengthen your first line of defence today — contact us to schedule your managed security testing now.

Oracle EBS Zero-Day CVE-2025-61882: Australian Threat
Critical Oracle EBS zero-day CVE-2025-61882 actively exploited. Australian firms face data theft. Move beyond patching to proactive red teaming & security.
Crown Jewels Under Siege: Deconstructing the Oracle EBS Zero-Day and the New Reality for Australian Enterprises
The Illusion of the Secure Core
For decades, Enterprise Resource Planning (ERP) systems have been the digital heart of major organisations—the secure, centralised vaults for finance, human resources, and supply chain logistics. Systems like Oracle E-Business Suite (EBS) are not just applications; they are the operational nervous system, the presumed-impenetrable core behind layers of perimeter defence. In late 2025, that illusion was shattered.
A critical zero-day vulnerability, later designated CVE-2025-61882, demonstrated that these digital fortresses were not only vulnerable but could be compromised from the public internet without so much as a password. The perpetrators were the notorious Cl0p ransomware group, but their attack was not a typical disruptive encryption campaign. Instead, they executed a stealthy, months-long operation focused on a single objective: the exfiltration of corporate crown jewels for the purpose of extortion.
This incident is a stark illustration of a strategic evolution in cyber extortion. While some threat actors continue to focus on operational disruption through encryption, sophisticated groups now recognise that the sensitive data within ERP systems is often far more valuable than any ransom they could demand for a decryption key. The primary business risk is no longer system downtime but catastrophic data breach, leading to severe regulatory fines under legislation like the Privacy Act , loss of competitive advantage, and irreparable brand damage.
The most critical detail for security leaders is the timeline. The attackers began exploiting this vulnerability as a zero-day as early as August 2025. Oracle, the vendor, did not release an emergency patch until October 4, 2025. For at least two months, Australian organisations were exposed to a critical, actively exploited vulnerability for which no defence, no patch, and no signature existed. This reality check invalidates outdated security models and forces a difficult question upon every CISO: if patching and prevention failed, what would it take to detect and respond to such an attack?
Anatomy of a Sophisticated Compromise: A Technical Deep Dive into CVE-2025-61882
To comprehend the strategic implications of this breach, it is essential to understand the technical elegance of the exploit. The compromise was not a brute-force attack but a multi-stage chain of vulnerabilities that allowed attackers to bypass defences and gain complete control of the target system. This deep technical understanding reveals the attacker's mindset and demonstrates why traditional, signature-based defences were rendered ineffective.
The vulnerability, CVE-2025-61882, resides within the BI Publisher Integration module of Oracle EBS, affecting versions 12.2.3 through 12.2.14. It carries a CVSS 3.1 base score of 9.8 (Critical), a rating reserved for the most severe flaws. The vector string, AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H, translates to a nightmare scenario for defenders: it can be exploited remotely over a network (AV:N), requires low technical complexity (AC:L), needs no prior privileges or authentication (PR:N), requires no interaction from a user (UI:N), and results in a complete loss of confidentiality (C:H), integrity (I:H), and availability (A:H).
The attack unfolded through a sophisticated exploit chain:
Initial Foothold via SSRF and CRLF Injection: The attackers first targeted public-facing web components of the EBS suite. They used a Server-Side Request Forgery (SSRF) vulnerability, which essentially tricks the server into making web requests to arbitrary destinations on the attacker's behalf. By combining this with Carriage-Return Line-Feed (CRLF) Injection, they could manipulate the headers of these server-initiated requests. This is analogous to tricking a trusted internal mailroom clerk into crafting and sending a malicious package to a sensitive internal department, bypassing all external security checks. This technique allowed them to reach internal endpoints that were never intended to be exposed to the internet.
Payload Delivery via XSL Template Injection: Once they established this internal communication channel, the attackers abused a legitimate function within the BI Publisher: the XDO Template Manager. They used their SSRF-forged request to instruct the system to fetch and process an Extensible Stylesheet Language (XSL) file from an attacker-controlled server. Because the XSLT engine within EBS is powerful and can execute code, this malicious template acted as the payload delivery mechanism, ultimately leading to Remote Code Execution (RCE) on the underlying server.
Stealthy Persistence in the Database: To maintain long-term access, the attackers did not simply drop files on the disk, which might be detected by endpoint security tools. Instead, they used the application's own functionality to write their malicious templates directly into the EBS database, specifically within the
XDO_TEMPLATES_BandXDO_LOBStables. This made their foothold extremely difficult to detect, as it resided within the application's data layer, and allowed them to re-execute their payload at will.
This multi-stage process highlights a critical weakness in many security postures: a failure to inspect and validate traffic that appears to be internal or originates from a trusted application component. The attackers turned the system's own features against it, bypassing perimeter controls and leaving minimal forensic evidence.
| Attribute | Detail |
|---|---|
| CVE Identifier | CVE-2025-61882 |
| Vulnerability Type | Unauthenticated Remote Code Execution (RCE) |
| Affected Component | Oracle Concurrent Processing (BI Publisher Integration) |
| Affected Versions | Oracle E-Business Suite 12.2.3 – 12.2.14 |
| CVSS 3.1 Score | 9.8 (Critical) |
| CVSS Vector | $AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H$ |
| Key Attack Primitives | Server-Side Request Forgery (SSRF), CRLF Injection, XSL Template Injection |
| Added to CISA KEV Catalog | October 6, 2025 |
The Australian Fallout: Why This Is a Local Crisis, Not Just a Global Headline
While CVE-2025-61882 was a global event, its implications are particularly acute for Australia. The Australian government, through the Australian Signals Directorate's Australian Cyber Security Centre (ASD's ACSC), issued a critical alert on October 7, 2025, explicitly warning Australian organisations of the threat and urging them to apply the emergency patch. This official validation underscores the severity and relevance of the vulnerability to the national interest.
This single alert does not exist in a vacuum. It lands within a national threat landscape that is already at a heightened state of alert. ASIO's 2025 annual threat assessment warns that espionage and foreign interference are at "extreme levels" and that the threat of high-impact sabotage against the nation's critical infrastructure is likely to worsen over the next five years. With the ASD reporting that one in every ten cybersecurity incidents already targets critical infrastructure, the compromise of a foundational ERP system like Oracle EBS represents a materialisation of these exact fears.
The attack on Oracle EBS systems represents a dangerous convergence of threats. Although perpetrated by a financially motivated cybercrime group, the target—core enterprise systems that underpin critical infrastructure—is identical to the targets of sophisticated state-sponsored Advanced Persistent Threat (APT) groups. The tactics, techniques, and procedures (TTPs) are also blurring; the use of a zero-day exploit, a long dwell time for reconnaissance, and stealthy data exfiltration are hallmarks of nation-state operations. For an Australian CISO at a financial institution, utility provider, or healthcare organisation, the line between defending against cybercriminals and defending against state actors has effectively vanished. The attack vectors are converging, and a successful extortion attack could be just as damaging to national security as a dedicated espionage campaign.
This convergence is occurring against a backdrop of surging hostile activity. Data breaches involving Australian organisations surged by 48% in the first ten months of 2025 compared to the previous year, with 71% of these breaches attributed to ransomware and extortion groups. The sectors most frequently targeted—Professional Services, IT, Healthcare, Finance, and Energy & Utilities—are precisely those most reliant on the integrity and availability of large-scale ERP systems like Oracle EBS. For Australian security leaders, this is not a distant threat; it is a clear and present danger aimed directly at their core operations.
Beyond Emergency Patching: The Dangerous Gap Between Compliance and Resilience
The immediate response to the CVE-2025-61882 disclosure was a global scramble to apply Oracle's emergency patch. While necessary, this reactive measure obscures a far more dangerous truth: for the organisations breached, patching was irrelevant. The exploitation began in August, while the patch only became available in October. For over two months, compromised organisations were technically "compliant"—no patch was available to be deployed—but they were profoundly insecure, actively bleeding their most sensitive data.
This incident exposes the "Compliance Mirage": the dangerous gap between an organisation's security posture as measured by compliance metrics and its actual resilience against a determined adversary. Modern attackers deliberately weaponise this gap. They seek out zero-day vulnerabilities or abuse legitimate system functions precisely because these methods bypass the signature-based scanners and compliance checklists that dominate many security programs.
The two-month dwell time in the Oracle incident is a compressed, high-velocity example of a much larger systemic failure within the Australian cybersecurity landscape. According to the CyberCX 2025 Threat Report, the average time-to-detect (TTD) for espionage-related incidents in Australia has now reached a staggering 404 days. This is not an accident; it is the result of a deliberate attacker strategy. This extended dwell time is the goal, providing an unrestricted period for reconnaissance, privilege escalation, lateral movement, and the methodical exfiltration of data, all while remaining beneath the radar of compliance-focused security tools.
This systemic weakness in detection and response is deeply felt by the nation's security leaders. A recent report from Proofpoint found that an alarming 76% of Australian CISOs admit their organisations are unprepared to respond to a material cyberattack. They are operating with a significant visibility gap, and the 404-day TTD is the direct consequence. The Oracle EBS breach proves that an organisation can have a green dashboard on its vulnerability scanner while its crown jewels are being stolen. The focus must shift from a periodic, compliance-driven checklist to a continuous, evidence-based validation of defensive capabilities.
Hardening the Core: A Proactive Framework for Defending Business-Critical Applications
The lessons from CVE-2025-61882 demand a fundamental shift in mindset: from a futile attempt to prevent every breach to a strategy of "assuming breach" and engineering for resilience. This requires moving beyond reactive patching and embracing a proactive framework of continuous security validation. For business-critical applications like Oracle EBS, this framework must include several layers of proactive defence.
1. Continuous Attack Surface Management (ASM): The Oracle EBS vulnerability was exploitable because the affected component was accessible from the internet. The first principle of modern defence is that you cannot protect what you do not know exists. Continuous ASM provides a real-time, attacker's-eye view of an organisation's internet-facing assets, identifying exposed systems, forgotten legacy applications, and misconfigured cloud services before adversaries can exploit them.
2. Adversary Emulation and Red Teaming: It is no longer sufficient to ask if a system is patched. The critical question is whether your security operations can detect and respond to the TTPs of a group like Cl0p. Adversary emulation exercises simulate the exact, multi-stage attack chains used in the wild—from initial SSRF exploitation to data exfiltration—to test the efficacy of the entire security ecosystem, including people, processes, and technology.
3. In-Depth Application Penetration Testing: Automated scanners and periodic infrastructure tests are not enough to secure complex, bespoke applications like ERPs. Deep-dive application penetration testing moves beyond searching for known CVEs to actively probing for business logic flaws, authentication bypasses, and unique, "zero-day" vulnerabilities in the application's code and configuration. This is the only way to find the unknown flaws before attackers do.
4. Proactive Threat Hunting: Waiting for a SIEM alert means the defence is already behind. Proactive threat hunting assumes attackers are already inside the network and actively searches for the faint signals of their presence. In the case of the Oracle breach, a proactive hunt could have involved querying the EBS database for the creation of anomalous templates in the XDO_TEMPLATES_B table, as recommended by incident responders. This is a tangible, proactive step that could have identified the compromise during the long dwell time.
5. Incident Response Preparedness: With 76% of Australian CISOs feeling unprepared for a major incident, bolstering response capabilities is paramount. This involves more than just having a plan on paper. It requires regular tabletop exercises, playbook development for critical systems like ERPs, and retaining expert incident response teams to ensure that when a breach occurs, the reaction is swift, decisive, and effective at minimising business impact.
| Challenge Highlighted by CVE-2025-61882 | Outdated Reactive Approach (Compliance-Focused) | Modern Proactive Solution (Resilience-Focused) |
|---|---|---|
| Unknown Internet Exposure | Annual, point-in-time vulnerability scans. | Continuous Attack Surface Management to maintain a real-time inventory of exposed assets. |
| Exploitation of Unknown (Zero-Day) Flaws | Waiting for vendor patches and CVE alerts. | In-depth Application Penetration Testing to discover business logic flaws and unknown vulnerabilities. |
| Long Attacker Dwell Time | Relying on EDR/SIEM alerts based on known signatures. | Proactive Threat Hunting for IOCs and Adversary Emulation to test detection of novel TTPs. |
| Inability to Respond to a Major Incident | Ad-hoc incident response, developing the plan during a crisis. | Incident Response Readiness, including tabletop exercises and pre-defined playbooks for critical systems. |
| Sophisticated, Multi-Stage Attacks | Siloed security tools and perimeter-based defences. | Red Teaming to test the entire security ecosystem's ability to withstand a determined, multi-stage attack. |
The CISO's Mandate: From Reactive Firefighting to Strategic Resilience
The compromise of Oracle E-Business Suite via CVE-2025-61882 is more than a technical failure; it is a strategic inflection point for Australian security leaders. It serves as a powerful, board-level case study that encapsulates the primary challenges of the modern threat landscape: sophisticated adversaries, the weaponisation of zero-days, and the inadequacy of a compliance-only security posture.
The core lessons are undeniable. Business-critical ERP systems are high-value targets. Patching, while essential, is not a strategy against zero-day threats. The true measure of security is not the strength of the perimeter but the speed of detection and response, and the long attacker dwell times prevalent in Australia indicate a systemic failure on this front.
This reality lands on the shoulders of Australian CISOs who are already under immense pressure. They navigate an increasingly complex web of regulations, from the Security of Critical Infrastructure Act to new rules for smart devices and ransomware reporting. They also face a crisis of burnout within their teams, with 78% of organisations reporting issues driven by increased threat activity and a lack of resources.
Yet, this incident also provides a catalyst for change. With 80% of Australian organisations planning to increase their cybersecurity budgets, CISOs have an opportunity to argue for a strategic reallocation of resources. The narrative of CVE-2025-61882 provides the perfect justification to shift investment away from purely preventative, compliance-based tools and toward proactive validation services that build genuine, measurable resilience.
The mandate for the modern CISO is clear. The defining question is no longer "Are we patched and compliant?" but "How quickly would we detect and respond to an attack like the one that compromised Oracle EBS?" Answering that question requires moving beyond assumptions and embracing a culture of continuous testing, validation, and preparedness. It requires partnering with experts who can simulate real-world attacks and provide an unvarnished assessment of an organisation's true defensive capabilities. The next zero-day is not a matter of if, but when. The time to prepare is now.

Scanning Smarter: How Managed Web Vulnerability Scanning Detects What Traditional Tools Miss
Discover how Lean Security’s managed web vulnerability scanning detects threats traditional tools miss, delivering stronger protection for businesses.
When it comes to protecting your business from cyber threats, knowing where you’re vulnerable is half the battle. Many organisations rely on traditional web vulnerability scanners to uncover weaknesses in their applications. While these tools can be useful, they often produce incomplete results, leaving blind spots that hackers are eager to exploit.
This is where managed web vulnerability scanning changes the game. Instead of relying on automated tools alone, managed scanning combines cutting-edge technology with expert oversight, ensuring threats are identified, validated, and prioritised with far greater accuracy.
This blog will discuss the shortcomings of traditional vulnerability scanners, what makes managed scanning different, and why businesses serious about cybersecurity are shifting toward a managed approach.
1. The Limitations of Traditional Vulnerability Scanners
Automated scanners are often the first line of defence for businesses because they are:
· Easy to deploy
· Relatively inexpensive
· Capable of scanning large volumes of assets quickly
However, they are far from foolproof. Common problems include:
False Positives and Negatives: Automated tools frequently flag harmless issues as critical while overlooking real vulnerabilities that don’t fit their signature patterns.
Surface-Level Analysis: Many scanners only scratch the surface, missing vulnerabilities hidden deeper in the application architecture.
One-Size-Fits-All Results: Reports are often generic, leaving IT teams with long lists of vulnerabilities but no clear guidance on prioritisation.
For organisations that depend solely on these tools, the result is often wasted time chasing non-issuesora false sense of security.
2. What Managed Web Vulnerability Scanning Offers
Managed security services elevate the process by combining automated scanning with expert analysis, contextual insights, and actionable reporting. Rather than leaving teams overwhelmed with raw scan data, managed services provide clarity and direction.
Key benefits include:
Expert Validation: Human experts review scan results to confirm real vulnerabilities and weed out false positives.
Prioritisation: Instead of a laundry list of issues, businesses receive clear guidance on which vulnerabilities pose the most risk.
Continuous Monitoring: Threats evolve quickly. Managed scanning ensures new vulnerabilities are detected as they emerge, not just during scheduled scans.
This approach transforms vulnerability scanning from a checklist item into a proactive defence mechanism.
3. Detecting What Traditional Tools Miss
So, what exactly does managed scanning catch that traditional tools overlook?
Business Logic Flaws: Automated scanners aren’t great at identifying vulnerabilities in workflows, like checkout processes or user authentication flows, which attackers can exploit.
Context-Specific Risks: Managed services understand your business environment, allowing them to assess vulnerabilities within the context of your applications, users, and data.
Emerging Threats: Experts keep pace with new attack techniques and can update scanning approaches faster than static tools.
Configuration Weaknesses: Automated tools often miss subtle misconfigurations in servers, APIs, or third-party integrations that could expose sensitive data.
By pairing automation with human intelligence, managed scanning uncovers the risks that would otherwise slip through the cracks.
4. Reducing Noise with Actionable Reporting
One of the biggest frustrations with traditional scanning tools is the overwhelming amount of raw data they generate. IT teams are left with:
· Dozens (or even hundreds) of findings
· Unclear risk levels
· No actionable next steps
Managed scanning solves this by providing tailored reporting. Instead of handing you a generic PDF full of technical jargon, managed services deliver concise, actionable insights:
· Which vulnerabilities are critical right now
· What steps are needed to remediate them
· How issues map to compliance requirements
This level of clarity empowers businesses to act faster and more confidently.
5. The Role of Human Expertise
Cybersecurity isn’t just a technology problem—it’s a people problem. Attackers exploit human error, misconfigurations, and overlooked vulnerabilities that machines can’t always catch.
Managed vulnerability scanning integrates the expertise of seasoned security professionals who:
· Stay updated on the latest threats and techniques
· Interpret scan results in the context of your environment
· Advise on both quick fixes and long-term strategies
In other words, you don’t just get a scan—you get a partner who understands your business and helps you stay secure.
6. Compliance and Regulatory Benefits
For many organisations, compliance is just as important as security. Regulatory frameworks like PCI DSS, HIPAA, and GDPR require regular vulnerability assessments.
Traditional scanners may check the box, but managed scanning ensures you:
· Generate audit-ready reports
· Demonstrate due diligence with expert validation
· Align vulnerability management with industry regulations
This not only helps avoid fines but also builds trust with customers, partners, and stakeholders.
7. Scaling Security with Your Business
As businesses grow, so does their attack surface. More applications, more integrations, and more data mean more opportunities for attackers.
Traditional scanners struggle to scale effectively in dynamic environments. Managed scanning, however, adapts seamlessly by:
· Providing flexible scanning schedules
· Covering cloud-based, hybrid, and on-premises environments
· Adjusting priorities as your business evolves
This ensures security isn’t left behind as your company scales.
8. Cost vs. Value: The Real ROI
At first glance, traditional vulnerability scanners may seem cheaper than managed services. But when you factor in:
· The cost of wasted time chasing false positives
· Potential losses from overlooked vulnerabilities
· Regulatory fines for compliance failures
The real return on investment favours managed scanning. By reducing risk and saving internal resources, managed services often pay for themselves many times over.
9. Why Lean Security’s Managed Web Vulnerability Scanning Stands Out
Not all managed services are created equal. At Lean Security, our approach goes beyond basic scanning:
Advanced Detection Tools: We leverage leading-edge technology to identify vulnerabilities that traditional tools miss.
Expert Analysis: Our team validates results to eliminate noise and highlight what matters most.
Tailored Reporting: Actionable insights help you focus on real threats, not false alarms.
Ongoing Support: We partner with you every step of the way, from detection to remediation.
Our mission is to provide smarter scanning that empowers businesses to stay secure in an ever-changing digital landscape.
Take Your Business to the Next Level
Don’t let traditional tools leave blind spots in your security strategy. Lean Security’s managed web vulnerability scanning combines advanced automation with expert oversight to uncover threats other scanners miss. From business logic flaws to configuration weaknesses, we provide actionable insights that protect your applications and your reputation.

Discover how managed web vulnerability scanning enhances cybersecurity by detecting flaws traditional tools miss. This infographic highlights expert oversight, real threat validation, actionable reporting, regulatory compliance, and human expertise—helping businesses reduce risks and secure systems with continuous monitoring.
Whether you’re aiming for stronger compliance or simply want peace of mind, our team ensures vulnerabilities are identified, validated, and addressed before attackers can exploit them. Secure your applications smarter with our penetration testing services. Contact Lean Security today and take the guesswork out of vulnerability scanning.

The Rise of Managed Security Services: Why DIY Cybersecurity No Longer Works
Discover why DIY cybersecurity no longer works and how managed security services deliver advanced protection, compliance, and 24/7 monitoring.
Nowadays, cyber threats evolve faster than most businesses can keep up. Hackers are no longer lone actors experimenting in basements — they’re highly organised, well-funded groups leveraging advanced techniques. For small and mid-sized businesses, trying to handle cybersecurity with a DIY approach has become not only impractical but downright dangerous.
The truth is simple: the stakes are higher, the risks are greater, and cybercriminals are more sophisticated than ever. Businesses that rely on in-house patchwork solutions often find themselves underprepared when faced with ransomware attacks, phishing campaigns, or data breaches.
This is why companies are increasingly turning to managed security services providers(MSSPs). These experts bring advanced tools, 24/7 monitoring, and deep industry expertise to safeguard businesses against modern threats. Let’s break down why DIY cybersecurity no longer works and why the rise of managed security services is no coincidence.
1. The Growing Sophistication of Cyber Threats
Cyberattacks today aren’t just random brute-force attempts. Threat actors now use artificial intelligence, machine learning, and automation to exploit vulnerabilities at lightning speed. A single weak password, an unpatched system, or an overlooked misconfiguration can give attackers an entry point.
For businesses relying on DIY cybersecurity, it’s nearly impossible to match the sophistication of these attackers. Even with antivirus software or firewalls in place, gaps remain, and those gaps are exactly where hackers strike.
MSSPs specialise in identifying and neutralising these advanced threats before they cause damage, using threat intelligence feeds and proactive monitoring that most businesses can’t maintain on their own.
2. The Hidden Costs of DIY Security
At first glance, handling security in-house might look like a way to save money. But in reality, the hidden costs of DIY cybersecurity can be overwhelming:
· Downtime expenses when systems are compromised.
· Regulatory fines for non-compliance with data protection laws.
· Reputational damage that drives customers away.
· Recovery costs for breach investigations and system rebuilds.
MSSPs help businesses avoid these financial pitfalls by reducing risk, improving compliance, and ensuring that breaches are detected and contained quickly.
3. Shortage of Skilled Cybersecurity Talent
Cybersecurity isn’t something any IT generalist can handle anymore. With more than 3.5 million unfilled cybersecurity jobs worldwide, finding and retaining top talent is harder than ever. For small businesses, hiring a full-time security operations team is simply unrealistic.
MSSPs solve this problem by giving businesses access to highly trained professionals who live and breathe cybersecurity. This way, companies get enterprise-level expertise without the cost and stress of recruiting, training, and retaining specialists.
4. Compliance and Regulatory Pressures
From GDPR in Europe to HIPAA in healthcare and PCI DSS in finance, compliance requirements are growing stricter across industries. Businesses that fail to meet these standards face heavy fines and legal consequences.
DIY security often misses the mark when it comes to compliance because most in-house teams lack the depth of knowledge required to meet evolving standards. MSSPs bring structured processes, compliance reporting, and audit support, helping businesses stay ahead of regulations and avoid penalties.
5. The Importance of 24/7 Monitoring
Cybercriminals don’t work 9-to-5. Attacks can strike at midnight, during holidays, or over weekends, the times when in-house IT staff aren’t watching. That’s when breaches go unnoticed and damages multiply.
MSSPs operate Security Operations Centres (SOCs) that monitor client environments around the clock. Every unusual activity is flagged, investigated, and acted upon immediately, reducing response times and minimising the impact of attacks.
6. Scalability and Flexibility
As businesses grow, so do their cybersecurity needs. A DIY setup that works for a small office can quickly crumble under the weight of new devices, cloud environments, and remote workers.
MSSPs scale effortlessly. Whether your business expands to new locations, adopts hybrid work models, or migrates to the cloud, managed security services adapt and evolve without requiring huge investments in new infrastructure or staff.

7. Proactive vs. Reactive Security
DIY cybersecurity often means reacting to problems after they happen, patching vulnerabilities once they’re exploited or cleaning up after a phishing attack succeeds.
MSSPs flip the script with a proactive approach. Using threat hunting, advanced analytics, and continuous vulnerability assessments, they identify risks before they turn into incidents. This shift from reaction to prevention is what keeps modern businesses safe.
8. Advanced Tools Beyond DIY Budgets
Sophisticated security tools, like endpoint detection and response (EDR), Security Information and Event Management (SIEM) systems, and threat intelligence platforms, are costly and complex to manage.
Most small to mid-sized businesses can’t afford these solutions on their own. MSSPs, however, spread the cost across clients, making cutting-edge technology accessible to businesses of all sizes.
9. The Human Element: Training and Awareness
Cybersecurity isn’t just about firewalls and software; human error is still one of the top causes of breaches. Employees click on phishing emails, download malicious attachments, or reuse weak passwords.
MSSPs often include employee training and phishing simulations as part of their service, ensuring that people, not just technology, become a strong line of defence.
10. Business Continuity and Incident Response
When a breach happens, response time is everything. Businesses without a clear incident response plan often lose valuable hours (or days) figuring out what to do.
MSSPs provide structured incident response strategies, forensic investigations, and business continuity planning. This ensures downtime is minimised, systems are restored quickly, and evidence is preserved for compliance or legal requirements.
11. Rising Ransomware Threats
Ransomware has exploded in recent years, targeting businesses of all sizes. Attackers don’t just encrypt data anymore — they also steal it and threaten to leak it unless payment is made.
DIY defences like basic backups aren’t enough against these sophisticated double-extortion tactics. MSSPs combine layered defences, secure backup strategies, and rapid recovery capabilities to protect against ransomware and minimise damage.
12. Why Businesses Are Making the Shift
Ultimately, businesses are recognising that DIY security is too risky, too costly, and too limited in scope. The rise of Managed Security Services reflects a broader reality: cybersecurity has become mission-critical.
With MSSPs, companies gain not only better protection but also peace of mind. Instead of constantly worrying about the next breach, leaders can focus on growth, innovation, and serving customers, knowing their security is in expert hands.
Lean Security: Your Trusted Partner in Managed Security
At Lean Security, we understand that the cybersecurity landscape is evolving at a pace businesses can’t match on their own. That’s why we provide comprehensive managed security services tailored to your unique environment. From 24/7 monitoring and compliance support to advanced threat detection and incident response, our team of experts ensures you’re always one step ahead of cybercriminals.
Don’t let outdated DIY approaches put your business at risk. With Lean Security as your managed services provider, you gain a dedicated partner focused on protecting your operations, your reputation, and your bottom line.
Ready to leave DIY behind and embrace a smarter, safer approach to cybersecurity? Contact Lean Security today to learn how our penetration testing services can transform your business’s defences.

Inside a Penetration Testing Company: What to Expect Before, During, and After an Engagement
Discover what happens before, during, and after penetration testing. Learn how penetration testing companies strengthen defences.
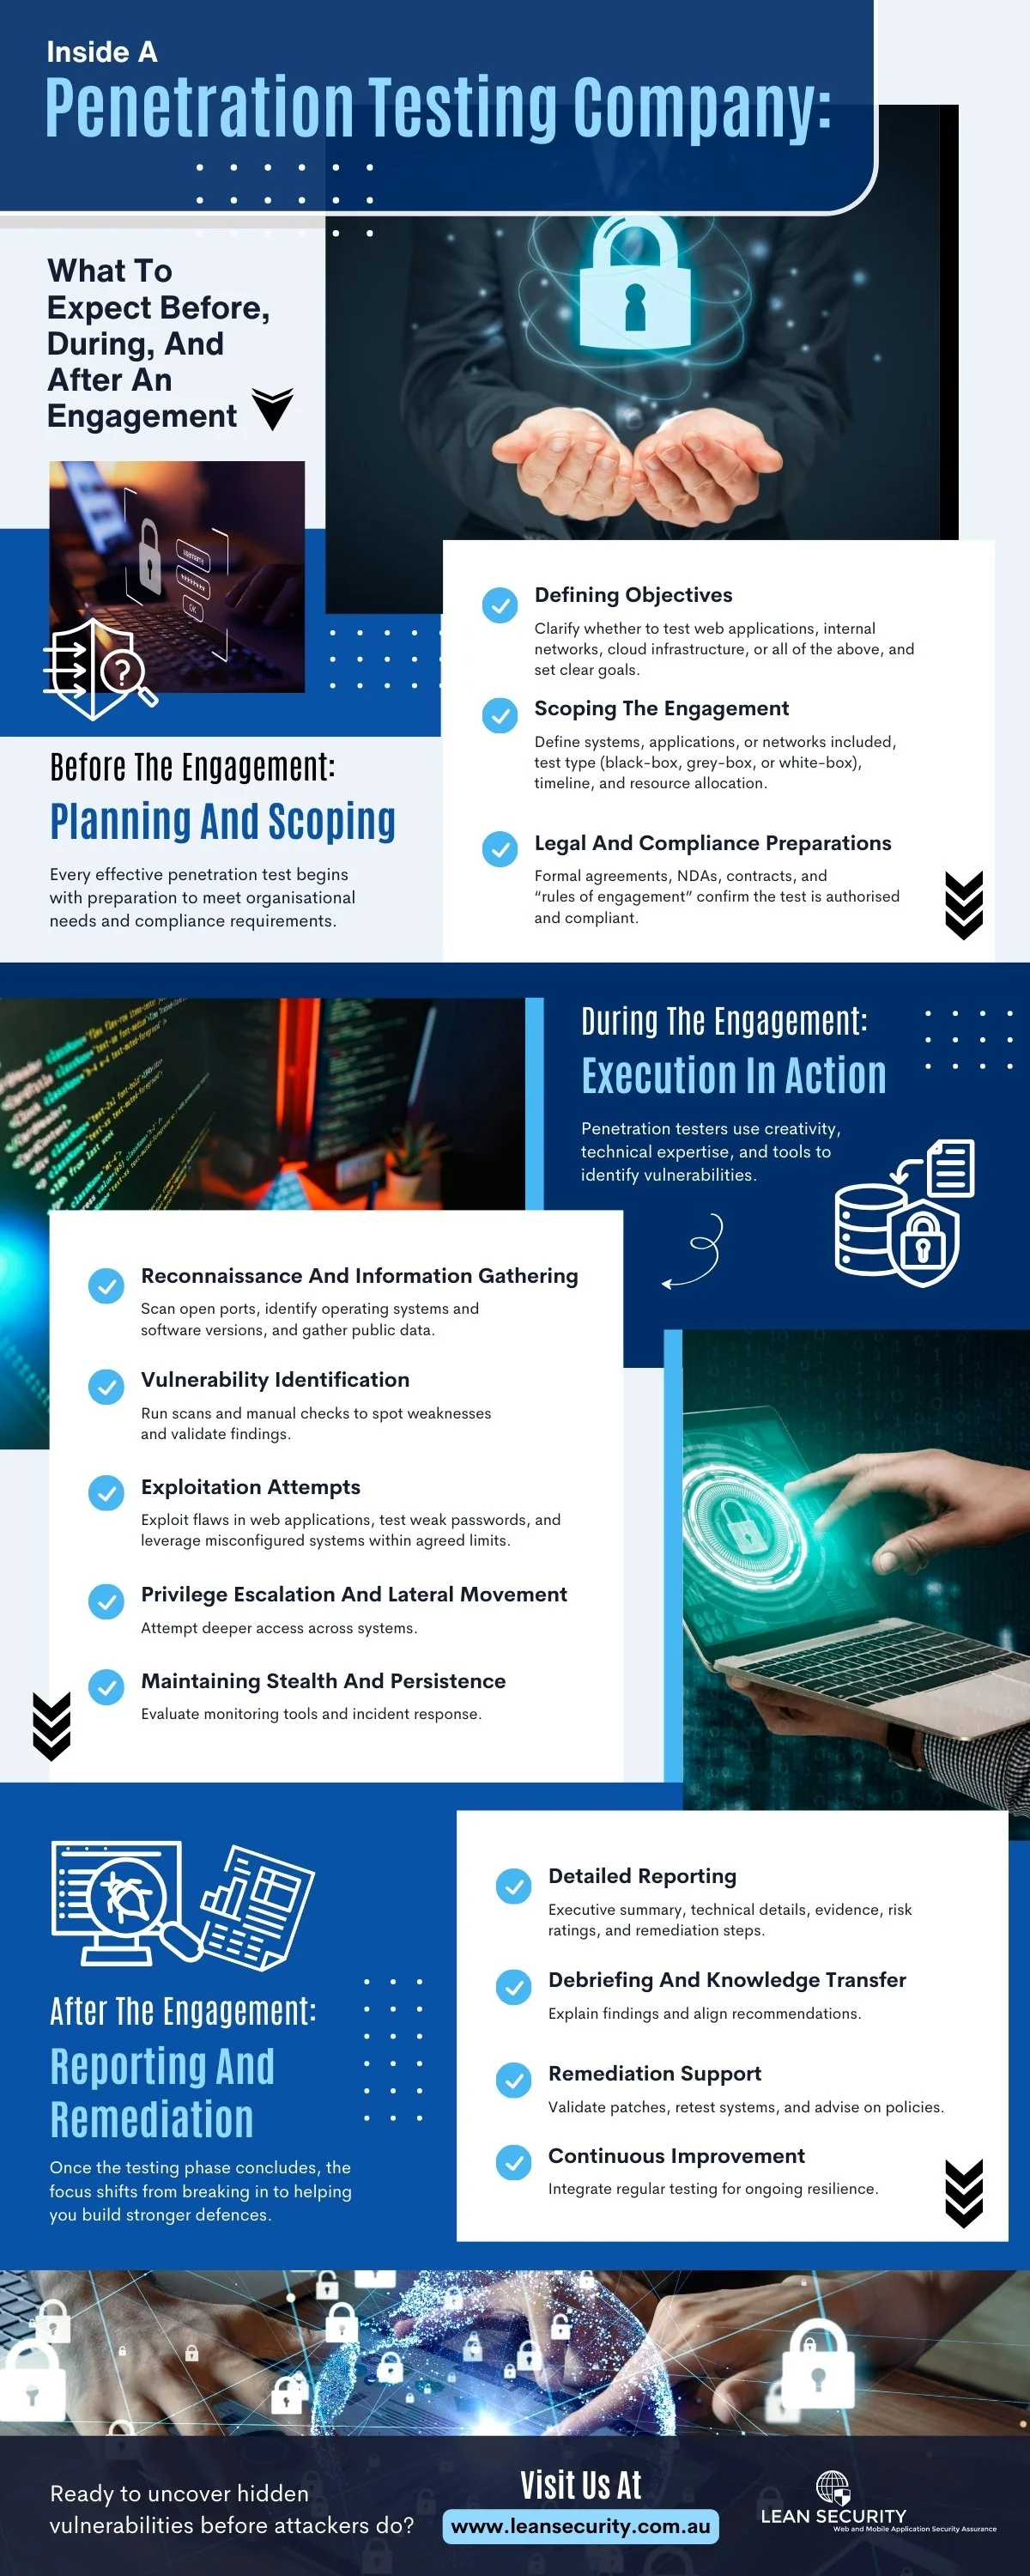
When it comes to enhancing cybersecurity, penetration testing isn’t just a checkbox — it’s a critical process that reveals how secure your digital environment really is. Many businesses know the term “pen test,” but few understand what actually goes on behind the scenes at a penetration testing company.
So, what should you expect when you partner with a penetration testing provider? Let’s break down the process step by step, before, during, and after the engagement, so you know exactly how these companies work to safeguard your systems.
Before the Engagement: Planning and Scoping
Every effective penetration test begins with preparation. This stage ensures the engagement aligns with your organisation’s needs and compliance requirements.
1. Defining Objectives
The company will work closely with you to clarify the goals of the test. Do you want to test your web applications, internal network, cloud infrastructure, or all of the above? Are you aiming for compliance or strengthening defences proactively? Clear objectives drive the scope.
2. Scoping the Engagement
A detailed scope ensures the test targets relevant systems without disrupting business operations. Expect to define:
· The systems, applications, or networks included
· Whether the test will be black-box (no prior knowledge), grey-box (partial knowledge), or white-box (full access)
· Timeline and resource allocation
3. Legal and Compliance Preparations
Penetration testing requires formal agreements to avoid misunderstandings. Non-disclosure agreements (NDAs), contracts, and “rules of engagement” documents protect both the company and the client. This step confirms the test is authorised and compliant with regulatory standards.
During the Engagement: Execution in Action
This is where the real work begins. Penetration testers combine creativity, technical expertise, and industry tools to identify vulnerabilities just as an attacker would.
4. Reconnaissance and Information Gathering
Pen testers start by collecting as much information as possible. This may include:
· Scanning open ports
· Identifying operating systems and software versions
· Gathering publicly available data
Recon is about mapping the attack surface before attempting to breach it.
5. Vulnerability Identification
Next, testers run scans and manual checks to spot weaknesses. Automated tools flag potential issues, but skilled testers validate findings to avoid false positives.
6. Exploitation Attempts
Here’s where the engagement gets interesting. Testers attempt to exploit vulnerabilities to gain access. This may involve:
· Exploiting web application flaws (SQL injection, XSS, and authentication bypass)
· Testing weak password policies
· Leveraging misconfigured systems
While real-world attack techniques are used, testers operate within agreed boundaries to prevent actual damage.
7. Privilege Escalation and Lateral Movement
If access is achieved, testers often attempt to escalate privileges or move laterally across systems. This demonstrates how an attacker could deepen their control within your environment.
8. Maintaining Stealth and Persistence
Some engagements include testing whether attackers could remain undetected. This evaluates monitoring tools, intrusion detection systems, and incident response capabilities.
After the Engagement: Reporting and Remediation
Once the testing phase concludes, the focus shifts from breaking in to helping you build stronger defences.
9. Detailed Reporting
Expect a comprehensive report that includes:
· Executive summary for leadership teams
· Technical details for IT staff
· Evidence of exploited vulnerabilities
· Risk ratings for each issue
· Actionable remediation steps
The best penetration testing companies translate complex technical findings into clear, prioritised insights for decision-makers.
10. Debriefing and Knowledge Transfer
A good provider doesn’t just hand you a report and walk away. They schedule a debriefing session to explain findings, answer questions, and align recommendations with your business context.
11. Remediation Support
After identifying weaknesses, companies often support remediation efforts. This could mean validating patches, retesting systems, or advising on security policies. The goal is to ensure fixes are not only applied but also effective.
12. Continuous Improvement
Penetration testing isn’t a one-time exercise. Leading companies encourage clients to integrate regular testing into their security strategy, aligning with compliance requirements (like PCI DSS or ISO 27001) and evolving cyber threats.
Behind the Scenes: What Sets Penetration Testing Companies Apart
Not all penetration testing providers are the same. Here are qualities that separate the best from the rest:
Expertise Beyond Tools: While automated tools help, skilled testers rely on creativity, experience, and human insight.
Industry-Specific Knowledge: Financial, healthcare, and retail sectors face different risks. Specialised knowledge ensures testing is relevant.
Clear Communication: The best firms simplify technical details, making results actionable for executives and IT teams alike.
Adaptability: Cyber threats evolve quickly. Strong companies continuously update methodologies to mimic current attack techniques.
Why This Process Matters
Understanding what happens before, during, and after a penetration test gives you confidence in the process. It also highlights why working with an experienced penetration testing company is so valuable: they don’t just find vulnerabilities; they help you close them and strengthen your overall security posture.
The Role of Collaboration Between Client and Tester
Penetration testing is not a one-sided effort. While the testers bring technical expertise and attacker-like creativity, the client’s role is equally important in shaping the outcome. Effective collaboration begins during the scoping stage and continues throughout the engagement. Your IT and security teams provide valuable insights into business priorities, critical systems, and operational concerns that help testers focus their efforts.
Clear communication also ensures the testing process doesn’t disrupt normal business operations. For example, scheduling tests during off-peak hours or identifying systems that cannot be interrupted minimises operational risks. When clients and testers work hand in hand, the results are not only more accurate but also more relevant to the organisation’s unique environment.
Turning Insights Into Long-Term Security Strategy
The end of a penetration test should mark the beginning of a stronger security journey. Too often, organisations view the final report as a checklist of fixes. In reality, the findings provide a roadmap for building long-term resilience.
By analysing recurring vulnerabilities and common weaknesses, businesses can identify patterns that point to deeper issues, such as insufficient staff training, outdated patching processes, or weak access controls. Penetration testing companies often highlight these themes and advise on preventative measures that go beyond immediate remediation.
When leveraged strategically, penetration test insights can influence policy decisions, guide investments in new technologies, and strengthen incident response readiness. Instead of reacting to individual vulnerabilities, organisations build a proactive security culture that evolves with the threat landscape.
Leading Penetration Testing Company
At Lean Security, we believe penetration testing should be more than a technical exercise — it should empower your business with clarity, protection, and confidence. Our expert team guides you through every stage of the process, from vulnerability scanning to web application security, ensuring your systems are tested against real-world attack techniques without unnecessary disruption.
Whether you’re preparing for compliance, defending sensitive data, or strengthening customer trust, Lean Security delivers results that go beyond reports. Don’t leave your organisation exposed to unknown risks. Partner with Lean Security today and take proactive steps toward a more resilient security posture.
Reach out now.