

Australian Cyber Threat Briefing: Critical RCEs and Ransomware Targeting SaaS & Education
As we wrap up the year, the Australian cyber threat landscape has intensified significantly over the last 24 hours. Critical vulnerabilities in widely used network appliances and targeted ransomware campaigns against key sectors—specifically Education, Healthcare, and SaaS providers—demand immediate attention from security teams.
As we wrap up the year, the Australian cyber threat landscape has intensified significantly over the last 24 hours. Critical vulnerabilities in widely used network appliances and targeted ransomware campaigns against key sectors—specifically Education, Healthcare, and SaaS providers—demand immediate attention from security teams.
Here is your daily briefing on the most critical threats impacting Australian organisations.
🚨 Critical Vulnerability Alert: WatchGuard Firebox (CVE-2025-14733)
Severity: Critical (CVSS 9.3) Status: Active Exploitation
A critical Remote Code Execution (RCE) vulnerability has been discovered in WatchGuard Firebox appliances. The flaw, tracked as CVE-2025-14733, resides in the iked process responsible for IKEv2 VPN negotiations.
- The Threat: Unauthenticated, remote attackers can exploit an out-of-bounds write condition to execute arbitrary code with root privileges. No user interaction is required.
- Impact: Full system compromise, allowing attackers to pivot into internal networks, intercept VPN traffic, or deploy ransomware.
- Action Required: Patch immediately to Fireware OS versions 2025.1.4, 12.11.6, or 12.5.15. CISA added this to its Known Exploited Vulnerabilities (KEV) catalog on 19 December, mandating urgent remediation.
Sector-Specific Threat Intelligence
🎓 Education / EdTech: University of Sydney Breach
The University of Sydney has confirmed a significant data breach impacting over 13,000 individuals, including current staff, alumni, and donors.
- Attack Vector: Threat actors accessed an internal online code library used for software development. While the system was non-critical, it contained historical datasets that were improperly stored.
- Exfiltrated Data: Names, dates of birth, residential addresses, phone numbers, and employment details.
- Analysis: This incident highlights the risk of "shadow data" in development environments. DevOps teams must ensure production data is never used in testing or coding repositories without sanitisation.
☁️ SaaS & Government: Netstar Australia Ransomware Attack
Melbourne-based Netstar Australia, a major provider of GPS telematics and fleet management solutions, has been hit by the Blackshrantac ransomware group.
- The Incident: The group claims to have exfiltrated 800GB of sensitive data and has listed the company on their dark web leak site.
- Criticality: Netstar’s client base includes government agencies and critical infrastructure operators. The compromise of real-time location data and fleet telemetry poses a severe national security and operational risk.
- Threat Actor Profile: Blackshrantac is a newer, aggressive group first observed in late 2025, known for double-extortion tactics and targeting mid-sized technology providers.
🏥 Healthcare: Harbour Town Doctors Data Leak
The Rhysida ransomware gang has claimed responsibility for an attack on Harbour Town Doctors, a Queensland medical centre.
- Status: The group has published samples of patient summaries, referral letters, and administrative records, demanding a ransom of 5 Bitcoin (~AUD 200,000).
- Sector Trend: Healthcare remains a primary target due to the high value of medical records (PHI) and the critical need for uptime. Small to medium clinics are increasingly targeted as "soft" entry points into the broader health ecosystem.
🛍️ eCommerce / Retail: BECKS Jewellery
Australian luxury jeweller BECKS has confirmed a cyber incident after the SafePay ransomware group listed them as a victim.
- Impact: Preliminary investigations suggest customer data and internal designs may have been compromised. Retailers are reminded that high-value brand reputation is a key lever used by extortionists.
Emerging Vulnerabilities & Exploits
Beyond WatchGuard, security teams should be vigilant regarding:
- Fortinet FortiCloud (CVE-2025-59718): A critical authentication bypass vulnerability allowing attackers to hijack sessions. Ensure all Fortinet SaaS integrations are reviewed.
- AI System Exploitation: We are observing an uptick in "prompt injection" attacks against customer-facing AI chatbots in the FinTech sector, used to bypass controls and elicit unauthorised account details.
Recommendations for the Weekend
- Audit Edge Devices: specifically WatchGuard and Fortinet appliances. If you cannot patch immediately, disable IKEv2 VPN services where possible.
- Review Code Repositories: Scan GitHub/GitLab instances for hardcoded secrets or production data (as seen in the USYD breach).
- Supplier Risk Management: If you utilise Netstar for fleet tracking, assess the sensitivity of the data they hold and prepare for potential operational visibility loss.
Contact us for a quote for penetration testing service or adversary simulation.

Daily Threat Briefing: Critical WatchGuard Exploits & Holiday Ransomware Spikes – 24 December 2025
As we head into the Christmas break, the Australian cyber threat landscape has escalated significantly over the last 24 hours. The Australian Signals Directorate’s Australian Cyber Security Centre (ASD's ACSC) has issued a critical alert regarding active exploitation of WatchGuard Firebox devices. This comes alongside a surge in ransomware activity targeting the education and government sectors, with threat actors looking to capitalise on reduced staffing levels during the holiday period.
Executive Summary
As we head into the Christmas break, the Australian cyber threat landscape has escalated significantly over the last 24 hours. The Australian Signals Directorate’s Australian Cyber Security Centre (ASD's ACSC) has issued a critical alert regarding active exploitation of WatchGuard Firebox devices. This comes alongside a surge in ransomware activity targeting the education and government sectors, with threat actors looking to capitalise on reduced staffing levels during the holiday period.
For security teams, the priority today is patching edge devices and ensuring on-call rotations are robust for the next 48 hours.
Sector-Specific Updates
Government
- ACT IT Systems Exposed: A scathing report released yesterday (23 December) by the ACT Audit Office has highlighted severe IT control weaknesses across multiple government agencies. The audit found that 68% of identified issues related to information security controls, specifically user access management and logging. This leaves agencies highly susceptible to fraud and unauthorised data exfiltration, a critical concern given the sensitive citizen data held.
- Critical Infrastructure Alert: The ASD has reiterated warnings regarding Salt Typhoon, a sophisticated state-sponsored actor targeting telecommunications infrastructure. Australian gov-tech providers are urged to review logs for "living off the land" techniques, particularly involving Cisco and Fortinet edge devices.
Education & EdTech
- Ransomware Hits Schools: The Fog ransomware gang has claimed responsibility for an attack on Waverley Christian College in Victoria. This follows a trend of late-year attacks on educational institutions when IT resources are often winding down.
- SaaS Platform Targeted: Australian educational support platform 'Thanks For the Help' (TFTH) has been listed as a victim by the KillSec ransomware group. This highlights the growing risk to EdTech SaaS providers who hold aggregated student data.
Healthcare
- Persistent Targeting: Following the CyberCX 2025 Threat Report, healthcare remains the most targeted non-government sector in Australia.
- Data Integrity Risks: Recent incidents involving Funksec (who targeted the Fresh Produce Safety Centre) demonstrate that even peripheral health-related non-profits are in the crosshairs. While the data leaks have been minor so far, the entry vectors often involve unpatched web applications and third-party API integrations.
eCommerce & FinTech
- API Security Crisis: New data indicates that 95% of Australian organisations experienced an API security incident this year. For eCommerce platforms bracing for Boxing Day sales, Broken Object Level Authorisation (BOLA) remains the top vulnerability.
- Gaming Sector Breach: Ainsworth Game Technology has been targeted by the Medusa ransomware group, with claims of over 800GB of data stolen. FinTechs and gaming operators should be on high alert for similar extortion attempts.
Emerging Vulnerabilities: Web, Cloud & AI
1. WatchGuard Firebox (CVE-2025-14733) – CRITICAL
- Status: Active Exploitation.
- Details: A critical authentication bypass vulnerability allows unauthenticated remote attackers to gain administrative access to the device.
- Action: Apply the hotfix immediately. If patching is not possible, restrict WAN access to the management interface.
2. Fortinet FortiCloud (CVE-2025-59718 & CVE-2025-59719)
- Status: High Risk.
- Details: These vulnerabilities allow for SSO Login Authentication Bypass. Attackers can hijack sessions to gain entry into cloud management consoles.
- Action: Verify all admin accounts have MFA enforced and review audit logs for suspicious logins from unknown IPs.
3. AI System Threats
- Adversarial AI: We are observing an uptick in "deepfake" social engineering attempts targeting finance teams for end-of-year invoice payments. Generative AI is being used to craft highly convincing phishing lures that bypass traditional email filters.
Threat Actor Activity
- Funksec: This group is currently active and opportunistic, targeting small to medium Australian enterprises (SMEs) with "double extortion" tactics—encrypting data and threatening to leak it.
- Pro-Russia Hacktivists: As flagged by the ACSC, these groups are conducting low-sophistication but high-impact DDoS attacks against critical infrastructure to disrupt holiday operations.
- Magecart / Digital Skimmers: With the Boxing Day sales approaching, eCommerce providers must ensure their Content Security Policies (CSP) are strict to prevent malicious JavaScript injection into checkout pages.
Recommendation
The "skeleton crew" approach to holiday staffing is a known vulnerability that adversaries exploit. Ensure your incident response plans are accessible and that key personnel are reachable.
Contact us for a quote for penetration testing service or adversary simulation.

Daily Threat Briefing: React2Shell Crisis & Aussie Healthcare Under Fire
The last 24 hours have been critical for Australian cyber defenders. A new maximum-severity vulnerability in the React framework, dubbed "React2Shell," is being actively exploited by state-sponsored actors, sending shockwaves through the SaaS and FinTech sectors. Simultaneously, the Australian healthcare and education sectors are grappling with fresh ransomware extortion attempts and significant data leaks.
Executive Summary
The last 24 hours have been critical for Australian cyber defenders. A new maximum-severity vulnerability in the React framework, dubbed "React2Shell," is being actively exploited by state-sponsored actors, sending shockwaves through the SaaS and FinTech sectors. Simultaneously, the Australian healthcare and education sectors are grappling with fresh ransomware extortion attempts and significant data leaks.
Vulnerability Spotlight: The "React2Shell" Crisis
CVE-2025-55182 (CVSS 10.0): React Server Components RCE The Australian Signals Directorate's Australian Cyber Security Centre (ASD's ACSC) has issued an "act now" alert regarding a critical Unauthenticated Remote Code Execution (RCE) flaw in React Server Components.
- The Threat: This vulnerability affects React 19 and widely used frameworks like Next.js. It allows attackers to execute arbitrary code on the server by sending a single malicious HTTP request, bypassing authentication entirely.
- Active Exploitation: Intelligence indicates that China-nexus threat actors, including Earth Lamia and Jackpot Panda, are weaponising this flaw to deploy persistent backdoors and XMRig cryptocurrency miners into cloud environments.
- Action: Engineering teams must upgrade to React versions 19.0.1+ or Next.js patched releases immediately. WAF rules should be tuned to block suspicious serialisation payloads.
CVE-2025-68613 (CVSS 9.9): n8n Workflow Automation RCE A critical flaw in the popular workflow automation tool n8n has been disclosed. Attackers can inject malicious expressions into workflows to gain full control over the underlying server. This is particularly dangerous for SaaS providers and FinTech firms relying on n8n for backend automation.
WooCommerce Store API Vulnerability A critical privacy flaw affecting WooCommerce (versions 8.1 to 10.4.2) was patched yesterday. The vulnerability allowed logged-in users to access the sensitive order details (PII) of guest customers via the Store API. While an auto-update has been rolled out to many stores, eCommerce administrators should manually verify their version is 10.4.3 or higher.
Sector-Specific Intelligence
Healthcare: Genea Targeted by Termite Ransomware
The Termite ransomware gang has claimed responsibility for a cyber attack on Genea, one of Australia's leading fertility service providers. The group alleges they have exfiltrated 700GB of highly sensitive data, including patient medical histories and diagnostic results. This incident reinforces the healthcare sector's position as the primary target for extortion in late 2025.
Education: University of Sydney Data Breach
The University of Sydney has notified stakeholders of a significant data breach affecting approximately 27,000 individuals, including staff, alumni, and students.
- Root Cause: A "DevSecOps" failure where production data was improperly stored in a non-production development environment—an unprotected online IT code library.
- Lesson: Educational institutions must enforce strict data sanitisation policies for test environments.
Government: Muswellbrook Shire Council Data Dump
Following a ransomware incident last month, the SafePay gang has reportedly published 175GB of stolen data from the Muswellbrook Shire Council. The dump includes internal correspondence and resident data, highlighting the catastrophic failure of "pay or we leak" negotiations.
IoT: Solar Inverters & Smart Homes
New research from Bitdefender and NETGEAR indicates a sharp rise in attacks targeting Australian smart homes, with a specific focus on solar inverters. These devices are being probed for vulnerabilities that could allow attackers to destabilise local power grids or pivot into home networks.
Strategic Recommendations
- Patch React & Next.js Stacks: Prioritise CVE-2025-55182. If immediate patching is impossible, isolate affected services from the public internet.
- Sanitise Non-Prod Environments: Review all development and staging environments to ensure no live PII is present. The USyd breach demonstrates that "obscurity" is not security.
- Review Third-Party Integrations: With the n8n and WooCommerce vulnerabilities, audit all third-party automation and eCommerce plugins for recent security updates.
- Healthcare Vigilance: Medical providers should urgently review egress filtering and backup immutability, as Termite ransomware is actively hunting in the region.
Contact us for a quote for penetration testing service or adversary simulation.

Daily Threat Briefing: Critical Cisco & React Zero-Days + NSW Health Risks
As we kick off the week leading into the holiday season, Australian security teams face a heightened threat landscape. Over the weekend, active exploitation of maximum-severity vulnerabilities in Cisco infrastructure and modern web frameworks has been confirmed. Additionally, fresh reports highlight significant cyber risks within the NSW healthcare sector and a major data breach impacting the tertiary education sector.
Executive Summary
As we kick off the week leading into the holiday season, Australian security teams face a heightened threat landscape. Over the weekend, active exploitation of maximum-severity vulnerabilities in Cisco infrastructure and modern web frameworks has been confirmed. Additionally, fresh reports highlight significant cyber risks within the NSW healthcare sector and a major data breach impacting the tertiary education sector.
Vulnerability Spotlight: The "React2Shell" & Cisco Crisis
Two critical vulnerabilities have dominated the threat landscape in the last 48 hours, demanding immediate attention from SaaS, Government, and Enterprise sectors.
Cisco AsyncOS Zero-Day (CVE-2025-20393):
- Severity: Critical (CVSS 10.0).
- Impact: A remote code execution (RCE) flaw in Cisco Secure Email Gateway is being actively exploited by a China-linked APT group tracked as UAT-9686.
- Attack Vector: Threat actors are using this flaw to deploy custom tunnelling tools ("AquaTunnel") and backdoors to maintain persistence. If your organisation relies on Cisco Secure Email, immediate patching is non-negotiable.
React Server Components "React2Shell" (CVE-2025-55182):
- Severity: Critical (CVSS 10.0).
- Impact: A pre-authentication RCE vulnerability affecting Next.js and React Server Components.
- Relevance: This is particularly dangerous for SaaS providers, eCommerce platforms, and EdTech solutions built on modern JavaScript stacks. Attackers can execute arbitrary code via a single malicious HTTP request. Asian-nexus threat groups have been observed integrating this exploit into their scanning routines.
Supply Chain Alert – ASUS Live Update (CVE-2025-59374):
- CISA has added this to its Known Exploited Vulnerabilities (KEV) catalog. It involves malicious code embedded directly into the update mechanism—a classic supply chain attack vector targeting IoT and consumer endpoints.
Sector-Specific Threat Intelligence
Healthcare
The NSW Auditor-General released a concerning report late last week, exposing significant cyber security maturity gaps across NSW Local Health Districts. Vulnerabilities in identity management and legacy systems have left critical public health infrastructure exposed.
- Incident: Reports have surfaced of a patient data breach at Harbour Town Doctors, alongside older data from the Genea Fertility hack circulating on the dark web.
- Action: Healthcare CISOs must prioritise network segmentation and review third-party access privileges immediately.
Education & EdTech
Sydney University is managing a cyber incident reportedly impacting over 13,000 individuals. While details are emerging, this reinforces the trend of ransomware groups targeting the education sector for high-volume PII (Personally Identifiable Information).
- Advisory: EdTech platforms using React/Next.js must audit their codebases for CVE-2025-55182 immediately to prevent student data exfiltration.
FinTech
Privacy concerns are front and centre following a finding against Regional Australia Bank for a breach involving third-party provider Biza. Even with patches applied, "co-mingled" consumer data highlighted the risks of complex supply chains in the Open Banking era.
- Threat Actor: Financial institutions should also be alert to SonicWall SMA 1000 exploitation (CVE-2025-40602), often used for secure remote access in this sector.
Government
With the Cambridge Analytica compensation registration deadline approaching (31 December), scammers are likely to ramp up phishing campaigns impersonating government refund portals. Agencies should anticipate a spike in brand impersonation attacks.
Adversary Tactics: AI & Cloud
We are observing a shift in how threat actors leverage AI systems. Recent intelligence suggests active probing of AI-driven web applications for "prompt injection" vulnerabilities that can lead to backend execution. Furthermore, the React2Shell vulnerability demonstrates how "cloud-native" frameworks are becoming prime targets for automated botnets seeking quick entry into cloud environments.
Recommendations
- Patch Immediately: Prioritise Cisco AsyncOS and SonicWall SMA appliances.
- Audit Web Stacks: Developers must verify their Next.js/React versions and apply mitigations for CVE-2025-55182.
- Review Supply Chain: Verify the integrity of update mechanisms for IoT fleets (ASUS).
- Heightened Monitoring: specific to NSW Health entities and University networks for anomalous data egress.
Contact us for a quote for penetration testing service or adversary simulation.

Fortinet "Ghost Logins": How Authentication Bypass Attacks Expose Gaps in Your Penetration Testing Strategy
Critical authentication bypass vulnerabilities in Fortinet FortiGate and related products (CVE-2025-59718 and CVE-2025-59719) are now under active attack, allowing "ghost" SSO logins that completely sidestep normal controls and logs. For Australian organisations, this is more than a VPN or firewall problem – it is a board-level exposure that directly tests whether your external penetration testing, internal penetration testing, and red team assessment services are capable of simulating SSO abuse, identity takeovers, and lateral movement across hybrid networks.
Executive summary:
Critical authentication bypass vulnerabilities in Fortinet FortiGate and related products (CVE-2025-59718 and CVE-2025-59719) are now under active attack, allowing "ghost" SSO logins that completely sidestep normal controls and logs. For Australian organisations, this is more than a VPN or firewall problem – it is a board-level exposure that directly tests whether your external penetration testing, internal penetration testing, and red team assessment services are capable of simulating SSO abuse, identity takeovers, and lateral movement across hybrid networks.
What just happened: Fortinet SSO auth-bypass under active attack
Fortinet has disclosed critical authentication bypass vulnerabilities (CVE-2025-59718 and CVE-2025-59719) affecting FortiOS, FortiProxy and FortiSwitchManager, impacting FortiCloud SSO flows into FortiGate and related appliances. These flaws allow attackers to forge or replay SSO artefacts and gain administrative access to appliances without valid credentials, effectively walking straight past login prompts and MFA.
Threat intelligence providers report malicious SSO logins and active exploitation "in the wild", with attackers using the bypass to obtain root-level control of VPN gateways and security appliances. Once an attacker owns the FortiGate, your perimeter, VPN trust boundary and network segmentation controls can be silently rewritten from the inside, turning your firewall into the attacker's beachhead.
Key takeaways for boards and CISOs:
- This is not a theoretical CVE; exploitation has already started.
- Compromise of the FortiGate tier effectively neutralises network security controls.
- Traditional penetration testing methods that only "scan and report" will miss SSO-centric and identity-abuse paths.
Why this incident reframes "what is penetration testing" for modern enterprises
At board level, "what is penetration testing" is changing from a narrow view of port scanning and basic exploitation to a broader application security assessment across identity, SSO, and cloud edge devices. Attacks on Fortinet SSO show how real adversaries chain weaknesses across VPNs, SAML/OIDC flows, RBAC misconfigurations and internal lateral movement to achieve business impact.
Modern penetration testing services in Australia must therefore validate not just internet-facing ports, but also:
- The integrity of SSO and identity federation to VPNs, admin portals and cloud consoles.
- Whether a compromised VPN appliance or identity token can be used to bypass network segmentation and reach crown-jewel systems.
For Australian organisations subject to PCI DSS, GDPR, or the Cyber Security Act 2024, boards need assurance that penetration testing is aligned to real-world attack paths – especially those starting at identity and VPN infrastructure.
How Fortinet SSO attacks actually work (and why scanners alone won't save you)
Authentication bypass through SSO flows
The Fortinet flaws centre on improper verification of SSO tokens and cryptographic assertions in FortiCloud SSO, enabling authentication bypass on FortiOS, FortiProxy and related components. In practice this means an attacker can submit crafted or replayed SAML/OIDC-style artefacts or exploit validation gaps to appear as a legitimate SSO user – often with administrator-level rights.
Once logged in as a "ghost" admin, attackers can:
- Change VPN and firewall policies to open backdoors and exfiltration paths.
- Create new trusted SSO configurations or local admin accounts that persist beyond patching.
- Disable logging, alter log destinations, or route logs to attacker-controlled collectors.
From VPN edge to complete network takeover
Observed exploitation patterns show a two-stage progression: first, auth bypass to gain control of the management plane; second, pivoting from the appliance into internal networks and management tools. With root-level control of a VPN gateway, an attacker can impersonate users, inject routes, and access internal services as if they were a trusted remote employee.
This adversary behaviour is beyond what a basic vulnerability assessment or simple penetration testing tool list will detect, because:
- Scanners tend to focus on version detection and known signatures, not subtle SSO state logic.
- Many organisations treat VPNs and firewalls as "out of scope" for application security assessment, leaving a blind spot between network penetration testing and web application penetration testing.
Vulnerability assessment vs pen test: why boards must care
Many organisations still use "vulnerability assessment vs pen test" interchangeably, but Fortinet SSO exploitation demonstrates why the distinction matters at the governance level.
| Aspect | Vulnerability Assessment | Penetration Testing |
|---|---|---|
| Approach | Automated scanning for known CVEs and misconfigurations. | Manual exploitation of authentication flows, SSO logic, and chained weaknesses. |
| Output | Point-in-time lists of issues, ranked by CVSS but often without business context. | Evidence-based scenarios demonstrating how an attacker could turn a Fortinet auth bypass into data theft, ransomware spread, or regulatory breach. |
| Board Value | Inventory of risks. | Proof of realistic breach paths and mitigation priorities. |
For CISOs, vulnerability assessment vs pen test is no longer a technical nuance; it is a question of whether the organisation has realistic evidence on how its identity and VPN stack would withstand a modern attack.
Mapping Fortinet SSO risk to penetration testing methods
To address this class of exposure, organisations should revisit penetration testing methodology and ensure it explicitly covers identity and SSO-driven threats.
External penetration testing
A modern external penetration testing engagement should now:
- Enumerate VPN, SSO, and edge appliances (FortiGate, Citrix, Palo Alto, ZTNA, CASB) as first-class targets.
- Attempt controlled abuse of SAML/OIDC, FortiCloud SSO and other federation mechanisms, not just open ports.
Internal penetration testing
Internal penetration testing then assumes the Fortinet layer has been compromised and asks, "What happens next?"
- Can a fake "VPN user" pivot from remote access networks to core AD, ERP and OT segments?
- Are EDR, NAC and micro-segmentation controls effective once an attacker is "inside the wire" with legitimate-looking network paths?
Web and API penetration testing
Because FortiGate typically fronts critical web applications and APIs, web application penetration testing and API penetration testing should be integrated into the same scenario.
- Test whether compromised VPN or reverse-proxy tiers weaken rate-limiting, WAF rules, or API authentication.
- Validate that tokens and sessions issued behind the VPN comply with least privilege and cannot be abused to escalate across tenants or environments.
Red team assessment services: simulating SSO and VPN abuse
Where penetration testing stops at enumeration and exploitation of specific hosts, red team assessment services simulate a persistent adversary who will chain multiple weaknesses to reach strategic objectives.
A mature red team scenario for Fortinet SSO risk should include:
- Phishing or credential theft to obtain low-privilege SSO accounts, followed by attempts to exploit auth-bypass flaws.
- Use of compromised FortiGate to reconfigure VPN split-tunnelling, routing, and DNS to quietly access backup networks, directory services and cloud control planes.
- Emulation of data staging, exfiltration and ransomware deployment pathways that start from the VPN tier rather than a traditional desktop compromise.
Regulatory and compliance implications for Australian organisations
Australia's Cyber Security Act 2024 and the new mandatory ransomware and cyber extortion payment reporting obligations mean that poorly secured VPN and SSO infrastructure now has regulatory as well as technical consequences.
- From 30 May 2025, Australian businesses above a $3 million turnover must report ransomware and cyber-extortion payments to ASD within 72 hours, regardless of payment size.
- Failure to report can attract civil penalties, and regulatory scrutiny is increasingly focused on whether "reasonable steps" were taken to protect networks and data before the incident.
For PCI DSS penetration testing and GDPR penetration testing obligations, a compromised VPN or firewall that exposes cardholder or personal data would be viewed as a preventable control failure if critical auth-bypass patches were missed or if testing scope excluded SSO and VPN infrastructure.
Board-level implications:
- Penetration testing for cloud security and VPN/SSO must be explicitly in scope for compliance attestations.
- Penetration testing price in Australia should be evaluated against the potential cost of a reportable ransomware event and associated regulatory penalties.
Building a modern penetration testing roadmap around identity and VPN risk
CISOs and IT Directors should use the Fortinet incident as a forcing function to modernise their penetration testing roadmap.
Prioritise identity-aware testing
- Integrate web application penetration testing, API penetration testing, and SSO abuse scenarios into core testing programmes, not as add-ons.
- Ensure penetration testing methods include manual review of SSO logic, JWT/SAML validation, RBAC enforcement and session management beyond automated scanning.
Cover the full technology stack
Your roadmap should explicitly call out:
- Network penetration testing that includes VPNs, firewalls, and SD-WAN controllers as high-value assets, not "plumbing".
- Internal penetration testing focused on lateral movement from VPN and privileged network zones into Active Directory, databases, and cloud management environments.
- Cloud penetration testing for IaaS, PaaS and SaaS, ensuring misconfigured SSO and conditional access policies are identified early.
- Mobile application penetration testing and IoT penetration testing for scenarios where remote staff, field devices or OT gateways rely on FortiGate or similar VPN infrastructure.
Make it accessible for small and mid-market businesses
Fortinet is widely deployed in small and mid-market Australian organisations, not just large enterprises. Penetration testing for small business therefore needs:
- Right-sized packages that still include VPN/SSO testing, not just a basic external scan.
- Clear penetration testing quote options that show what is covered (and what is not) so boards can make informed risk decisions.
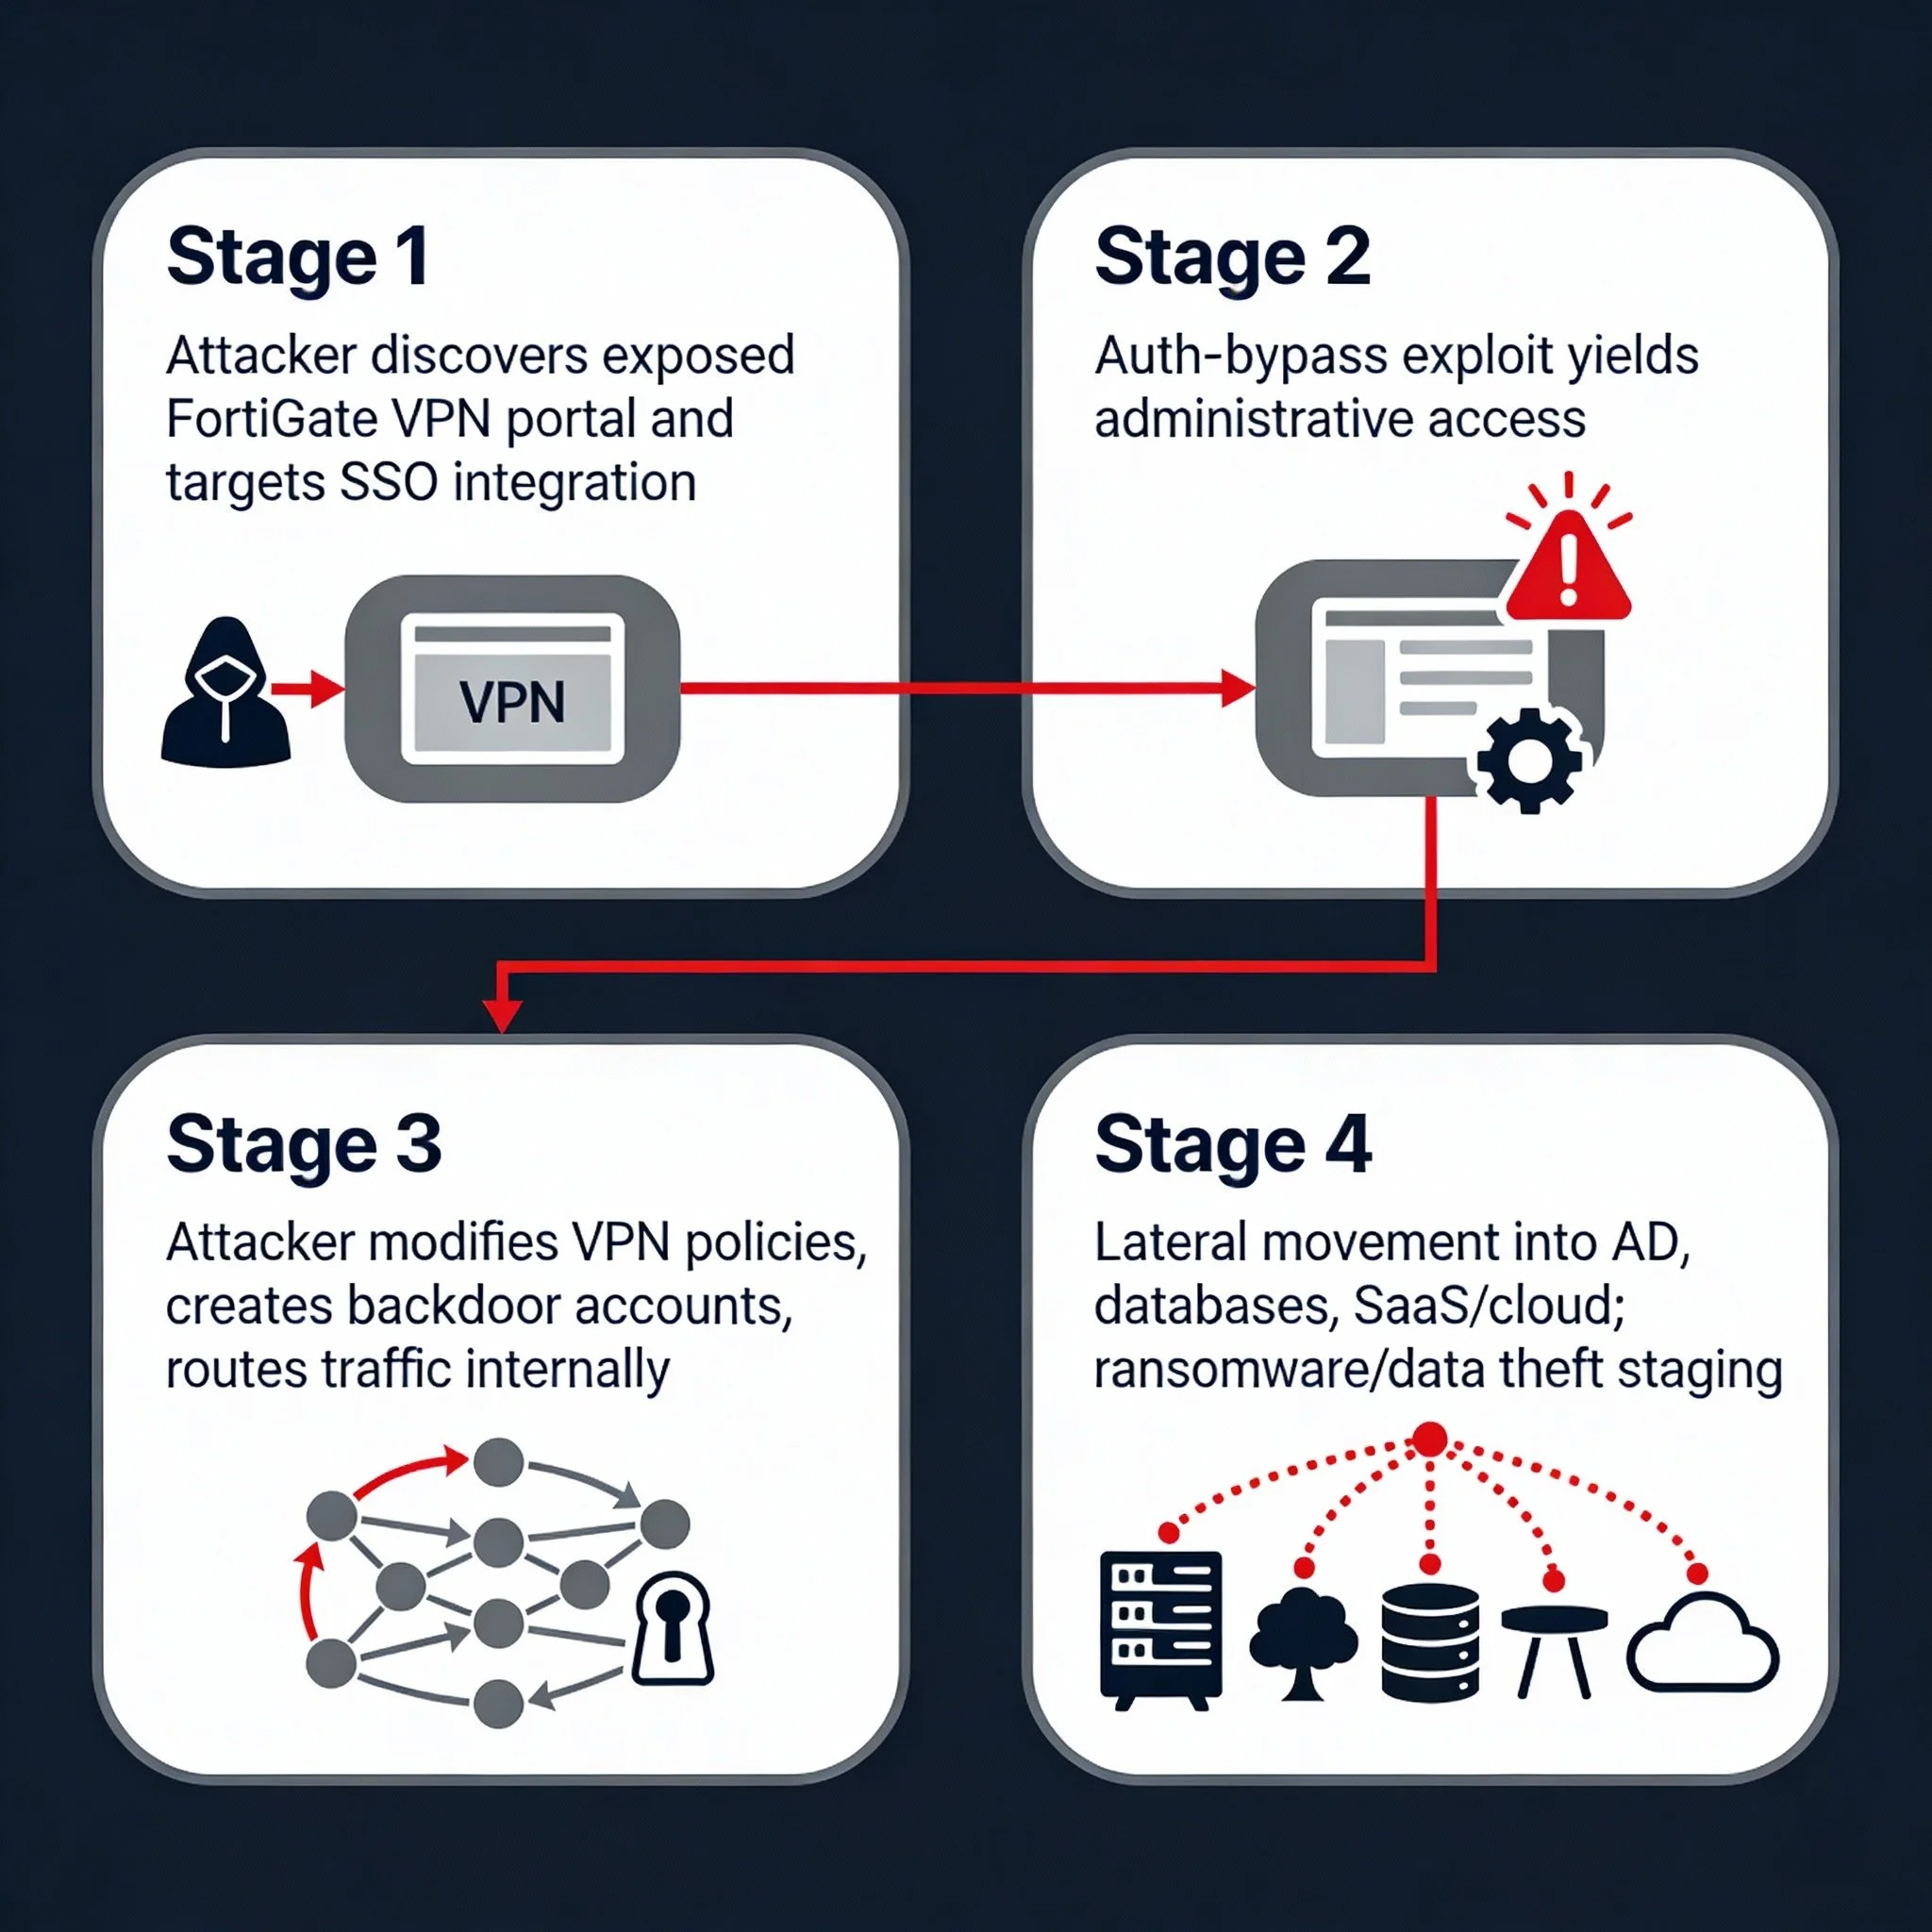
Visualising the attack path: from FortiGate to data loss
Below is a simple conceptual diagram that helps boards understand the Fortinet SSO attack chain:
Stage 1: Attacker discovers exposed FortiGate VPN portal and targets SSO integration.
Stage 2: Auth‑bypass exploit yields administrative access to FortiGate management.
Stage 3: Attacker modifies VPN policies, creates backdoor accounts, and routes traffic into internal networks.
Stage 4: Lateral movement into AD, databases, SaaS and cloud consoles; staging for ransomware or data theft.
How to engage: penetration testing services Australia should be demanding
In light of these Fortinet SSO vulnerabilities and the broader ransomware reporting landscape in Australia, organisations should look to hire a penetration tester or penetration testing company Australia that can demonstrate:
- Proven experience testing VPNs, SSO, and identity-centric attack paths – not just generic web testing.
- A clear penetration testing methodology that covers external penetration testing, internal penetration testing, cloud penetration testing, and application security assessment in a single, cohesive programme.
- Transparent guidance on penetration testing services Australia-wide, including realistic penetration testing price Australia figures and options to book a pen test aligned to your financial year and regulatory deadlines.
For boards, the question is no longer "penetration testing vs vulnerability assessment", but "are we testing the systems attackers are actually targeting – our VPNs, SSO, and cloud edge – with realistic adversary techniques?"
Call to action:
If your organisation relies on Fortinet or similar VPN and SSO infrastructure, now is the right time to schedule an integrated external, internal and application penetration testing engagement focused on identity and VPN abuse scenarios. Engage a specialist penetration testing company in Australia that can provide a tailored penetration testing roadmap, a clear penetration testing quote, and red team assessment services to validate your readiness against the next wave of SSO-driven attacks.