

Daily Threat Briefing: AI-Driven Phishing & The Machine Identity Crisis
In the last 24 hours, the Australian cyber threat landscape has been dominated by the rapid weaponisation of Generative AI and the escalation of "non-human" identity compromises. Following the patterns identified earlier this year in the ACSC's Annual Cyber Threat Report, we are seeing a shift from traditional credential stuffing to sophisticated, AI-enhanced social engineering and API-based attacks. Today's briefing highlights a coordinated campaign targeting the Healthcare and FinTech sectors, leveraging deepfake technology to bypass biometric verification. Additionally, new intelligence suggests state-sponsored actors are actively exploiting "shadow AI" implementations in Government supply chains.
Executive Summary
In the last 24 hours, the Australian cyber threat landscape has been dominated by the rapid weaponisation of Generative AI and the escalation of "non-human" identity compromises. Following the patterns identified earlier this year in the ACSC's Annual Cyber Threat Report, we are seeing a shift from traditional credential stuffing to sophisticated, AI-enhanced social engineering and API-based attacks.
Today's briefing highlights a coordinated campaign targeting the Healthcare and FinTech sectors, leveraging deepfake technology to bypass biometric verification. Additionally, new intelligence suggests state-sponsored actors are actively exploiting "shadow AI" implementations in Government supply chains.
Sector-Specific Updates
Healthcare: Intelligence indicates a surge in "Deepfake Vishing" (Voice Phishing) campaigns targeting hospital administration and procurement teams. Threat actors are using cloned voices of senior executives to authorise urgent fund transfers. This follows the industry's struggle with identity data leaks (reminiscent of the MediSecure incident), with attackers now using that historical data to craft hyper-personalised lures.
- Recommendation: Implement strict out-of-band verification for all urgent financial requests and review biometric authentication resilience.
FinTech: A major threat actor has been observed targeting "Machine Identities"—specifically, API keys and service account tokens used by automated trading bots and payment gateways. Unlike human credentials, these machine identities often lack MFA. We are seeing attempts to exploit logic flaws in SaaS financial platforms to exfiltrate these high-privilege tokens.
- Recommendation: Audit all service accounts and rotate long-lived API keys immediately.
Government: Adversaries linked to the "Salt Typhoon" group (and their successors) are reportedly probing private cloud infrastructure used by state agencies. The focus has shifted to "Data Poisoning"—altering datasets used to train regional AI models—potentially to sabotage decision-making algorithms in critical infrastructure.
- Recommendation: Verify the integrity of all data lakes and restrict write-access to AI training pipelines.
eCommerce: A new strain of "API Skimming" malware has been detected on several mid-sized Australian retail platforms. Instead of injecting JavaScript into the checkout page (Magecart style), this malware sits on the API gateway, silently copying payment payloads before they are tokenised.
- Recommendation: Implement aggressive API monitoring and behavioural analysis on all payment endpoints.
Education / EdTech: Ransomware groups are targeting unpatched VR/AR headsets and classroom management software. With the "Bring Your Own Device" (BYOD) policy expanding to include immersive tech, these devices have become a soft entry point into wider school networks.
IoT: A critical vulnerability in a popular "Smart Energy" protocol is being scanned for by botnets. Attackers are attempting to manipulate smart meter readings or cause denial-of-service conditions in residential energy grids.
Vulnerability Spotlight: Cloud & AI Systems
Critical RCE in Vector Databases (AI Infrastructure): Security researchers have disclosed a critical Remote Code Execution (RCE) vulnerability in a widely used open-source Vector Database, which is the backbone for many corporate RAG (Retrieval-Augmented Generation) AI systems.
- Impact: An unauthenticated attacker can send a malicious query that forces the database to execute arbitrary system commands, effectively granting full control over the AI cluster.
- Action: Patch your AI infrastructure immediately and isolate vector stores from the public internet.
SaaS API Broken Object Level Authorization (BOLA): We are tracking active exploitation of a BOLA vulnerability in a popular HR SaaS platform used by Australian enterprises. This flaw allows an authenticated user (e.g., a junior employee) to access the payslips and tax records of any other user by simply manipulating the
user_idparameter in API calls.
Conclusion
The events of the last 24 hours confirm that the perimeter has dissolved. The new battleground is identity—both human and machine. As organisations rush to deploy AI, they are inadvertently widening the attack surface. We strongly advise Australian organisations to move beyond "compliance" and adopt an aggressive "assume breach" mindset, particularly regarding their API and AI dependencies.
Contact us for a quote for penetration testing service or adversary simulation.

Australia’s Cyber Siege: Healthcare Ransomware, API Exploits, and the Holiday Scam Surge
The last 24 hours have underscored a critical reality for Australian CISOs and security teams: the separation between "sector-specific" threats is vanishing. From the 15.72 Tbps DDoS attack aimed at Australian infrastructure to the targeted ransomware campaigns crippling regional healthcare, the tempo of operations is accelerating as we approach the holiday season. As a penetration testing team, we are closely monitoring active exploitation in the wild. Below is your deep-dive briefing on the threats shaping the Australian landscape today.
The last 24 hours have underscored a critical reality for Australian CISOs and security teams: the separation between "sector-specific" threats is vanishing. From the 15.72 Tbps DDoS attack aimed at Australian infrastructure to the targeted ransomware campaigns crippling regional healthcare, the tempo of operations is accelerating as we approach the holiday season.
As a penetration testing team, we are closely monitoring active exploitation in the wild. Below is your deep-dive briefing on the threats shaping the Australian landscape today.
Sector Intelligence: Healthcare & Government in the Crosshairs
Healthcare: The "Beast" Claims a Victim Regional healthcare remains a primary target. The Outback Pharmacies group has been listed as a victim by the "Beast" (aka Gigakick) ransomware gang. Threat actors claim to have exfiltrated 150GB of sensitive data, including patient treatment plans, medical history, and financial records. This incident aligns with the broader trend of attackers targeting regional providers who may lack the Tier-1 security architecture of metropolitan hospitals.
- Strategic Shift: In response to this escalation, the Federal Government has announced a $6.4 million grant to establish a dedicated Healthcare Information Sharing and Analysis Centre (CI-ISAC). The goal is clear: stop the "spillover" effect where breaches in healthcare pivot to energy or transport sectors.
Government: Geopolitics & Massive DDoS Mitigation Yesterday, Australia officially listed the Islamic Revolutionary Guard Corps (IRGC) as a state sponsor of terrorism following intelligence on orchestrated attacks in Sydney and Melbourne. This geopolitical move often precipitates retaliatory cyber campaigns; government agencies and critical infrastructure providers should remain on high alert for hacktivist activity.
On the infrastructure front, Microsoft confirmed the mitigation of a record-breaking 15.72 Tbps DDoS attack targeting an Australian endpoint. The attack was attributed to the Aisuru botnet, a TurboMirai-class IoT botnet. This confirms that adversaries are weaponising compromised IoT devices at an unprecedented scale to attempt brute-force disruptions of Australian cloud resources.
Education: The Western Sydney University Saga Continues The situation at Western Sydney University (WSU) offers a sobering lesson in threat persistence. Despite the arrest of a former student on 20 cybercrime charges, attacks against the university have continued. This suggests WSU is battling multiple threat actors simultaneously—potentially an insider threat acting independently of external ransomware groups. This highlights the complexity of attribution and the necessity of "zero trust" internal architectures.
Vulnerability Spotlight: Active Exploitation in the Wild
For security engineers and penetration testers, the following vulnerabilities require immediate attention. Exploits are circulating, and we are seeing active scanning against Australian IP ranges.
1. Critical FortiWeb Exploits (Web Application Firewalls) Fortinet has patched two severe vulnerabilities in its Web Application Firewall (WAF) that are being chained by attackers:
- CVE-2025-64446 (CVSS 9.1): A critical path traversal vulnerability allowing unauthenticated remote code execution (RCE).
- CVE-2025-58034 (CVSS 6.7): An OS command injection flaw.
- Attack Vector: We are observing campaigns where attackers use the path traversal flaw to bypass authentication and then pivot to command injection to gain root access. Patch immediately to version 8.0.2 or higher.
2. Oracle Identity Manager API Bypass (CVE-2025-61757)
This CVSS 9.8 vulnerability is a textbook example of API insecurity. Attackers are bypassing authentication by simply appending specific strings like ;.wadl or ?WSDL to API endpoints.
- The Threat: This allows adversaries to manipulate identity governance flows and escalate privileges without valid credentials. If you rely on Oracle for IAM, verify your exposure immediately.
3. NPM Supply Chain Attack ("Shai-Hulud 2.0")
A sophisticated supply chain attack has been detected targeting developers using popular packages like Zapier and Postman. The "Shai-Hulud 2.0" campaign injects malicious code during the preinstall phase, exfiltrating CI/CD secrets and developer credentials.
- Action: Audit your development pipelines and lock dependency versions to known good states.
FinTech & eCommerce: The AI-Driven Holiday Scam Wave
As the Black Friday/Cyber Monday window opens, AI-driven fraud is surging. A new report indicates Australian shoppers are losing an average of AUD $445 per incident. The new vector? AI-generated "deal sites" that mimic legitimate brands with perfect spelling and high-quality graphics, specifically targeting users of "Buy Now, Pay Later" services.
Simultaneously, a massive phishing campaign impersonating Centrelink and Medicare (MyGov) is hitting inboxes, aiming to harvest credentials during this high-traffic period.
Summary & Mitigation
The threat landscape is currently dominated by extortion (Ransomware) and infrastructure stress tests (DDoS).
- Patch FortiWeb and Oracle IAM interfaces immediately.
- Geo-block traffic from high-risk regions if your business logic allows, particularly to mitigate botnet volumes.
- Adversary Simulation: With the WSU incident proving that "insiders" and "outsiders" can attack simultaneously, validating your detection capabilities against a multi-vector attack is crucial.
Contact us for a quote for penetration testing service or adversary simulation.

SessionReaper & BFCM: Why Penetration Testing Services Are Critical (CVE-2025-54236)
A critical vulnerability in Adobe Commerce and Magento (CVE-2025-54236), dubbed "SessionReaper," is being ruthlessly exploited by threat actors using AI-driven tools to automate attacks at machine speed. With the Australian holiday trading season in full swing, this unauthenticated remote code execution (RCE) flaw poses an immediate existential threat to retail and B2B organizations. This alert outlines the mechanics of the attack, the role of AI in its weaponization, and the urgent defensive actions required to prevent a catastrophic data breach.
The SessionReaper Ultimatum: Why Penetration Testing Services Are Vital to Surviving the 'Code Freeze'
Executive Summary: Hackers are exploiting a critical Adobe Commerce flaw, CVE-2025-54236 (SessionReaper). This threat endangers Australian e-commerce during the Black Friday peak. New Privacy Act fines make the traditional "Code Freeze" risky. This report explains the threat. It shows why penetration testing services are key to securing your store without stopping sales.
The Convergence of Critical Vulnerability and Law
Q4 2025 brings two major threats. First, SessionReaper attacks the Adobe Commerce ecosystem. Second, strict Australian laws now change the cost of a data breach.
For Australian CISOs, the rules have changed. Legal and financial risks now outweigh the risk of patching during a peak.
The Threat: SessionReaper (CVE-2025-54236)
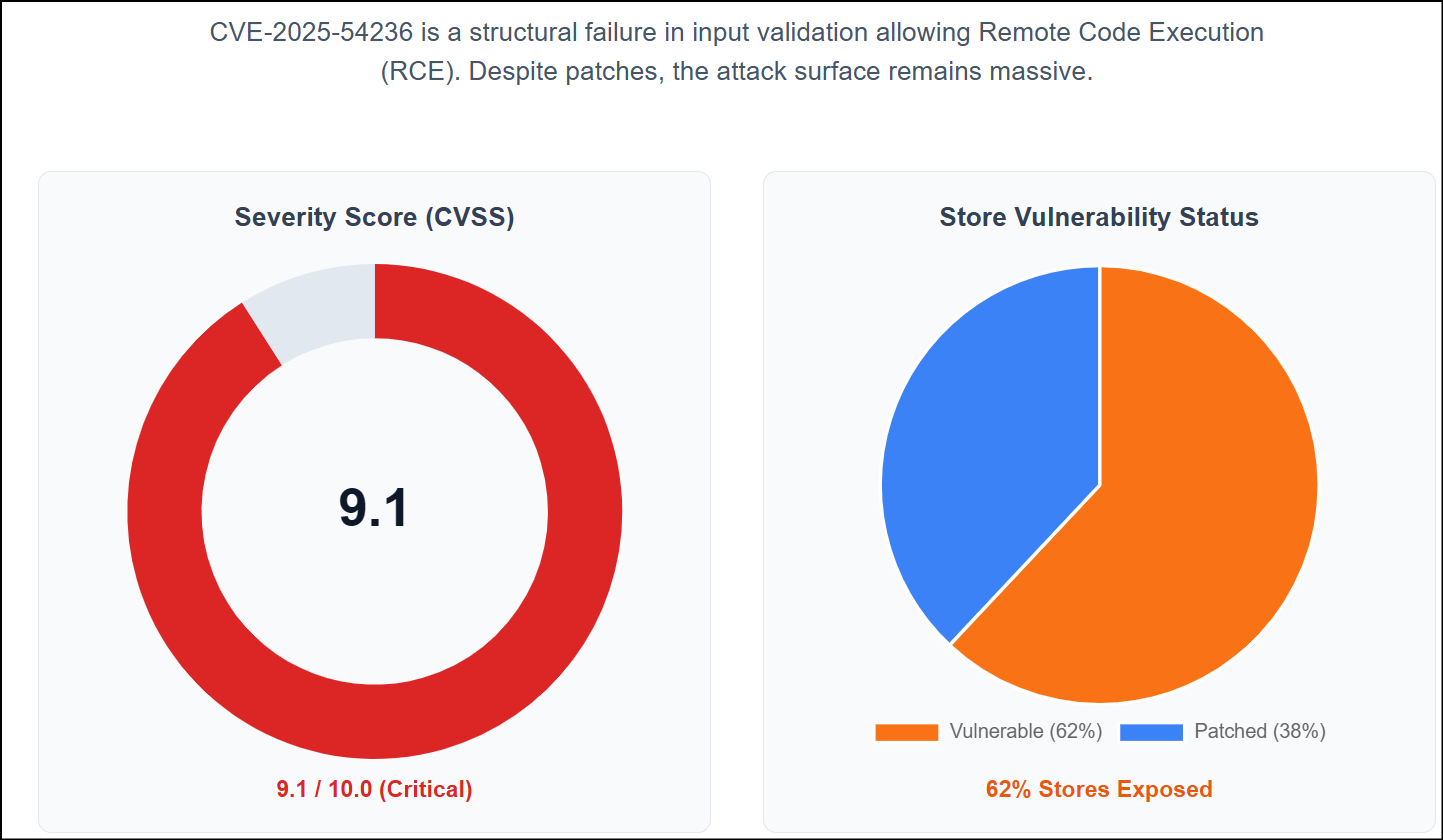
SessionReaper is a major flaw in how Adobe Commerce handles data. It lets attackers run code on your server without a login.
CVSS Score: 9.1 (Critical)
Vector: Remote Code Execution (RCE) via PHP Object Injection
Authentication: None required
Impact: Full server takeover, data theft, ransomware.
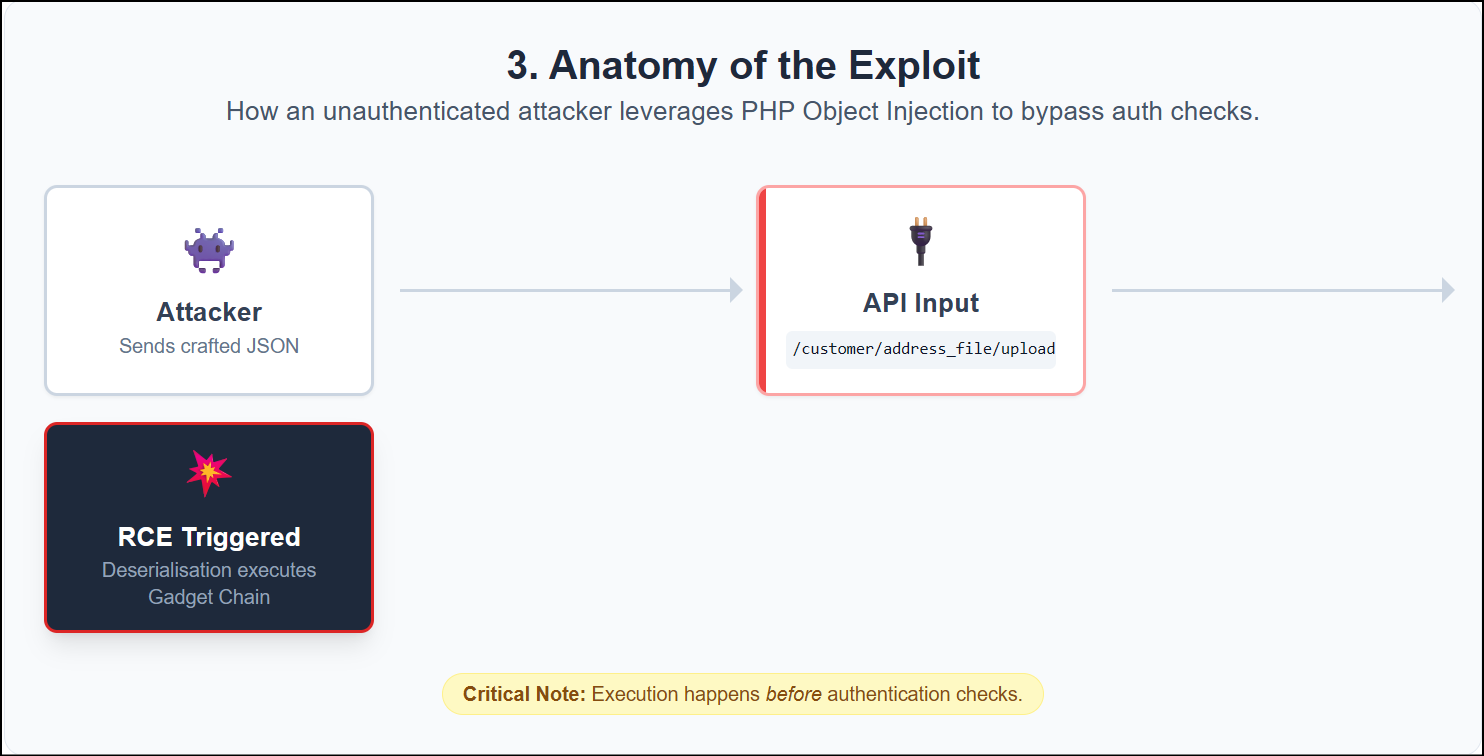
Attackers send fake data to specific API endpoints (like /customer/address_file/upload). The system trusts this input. It then runs malicious commands hidden inside the data.
The Australian Regulatory Minefield
You cannot ignore this threat just to keep the site stable.
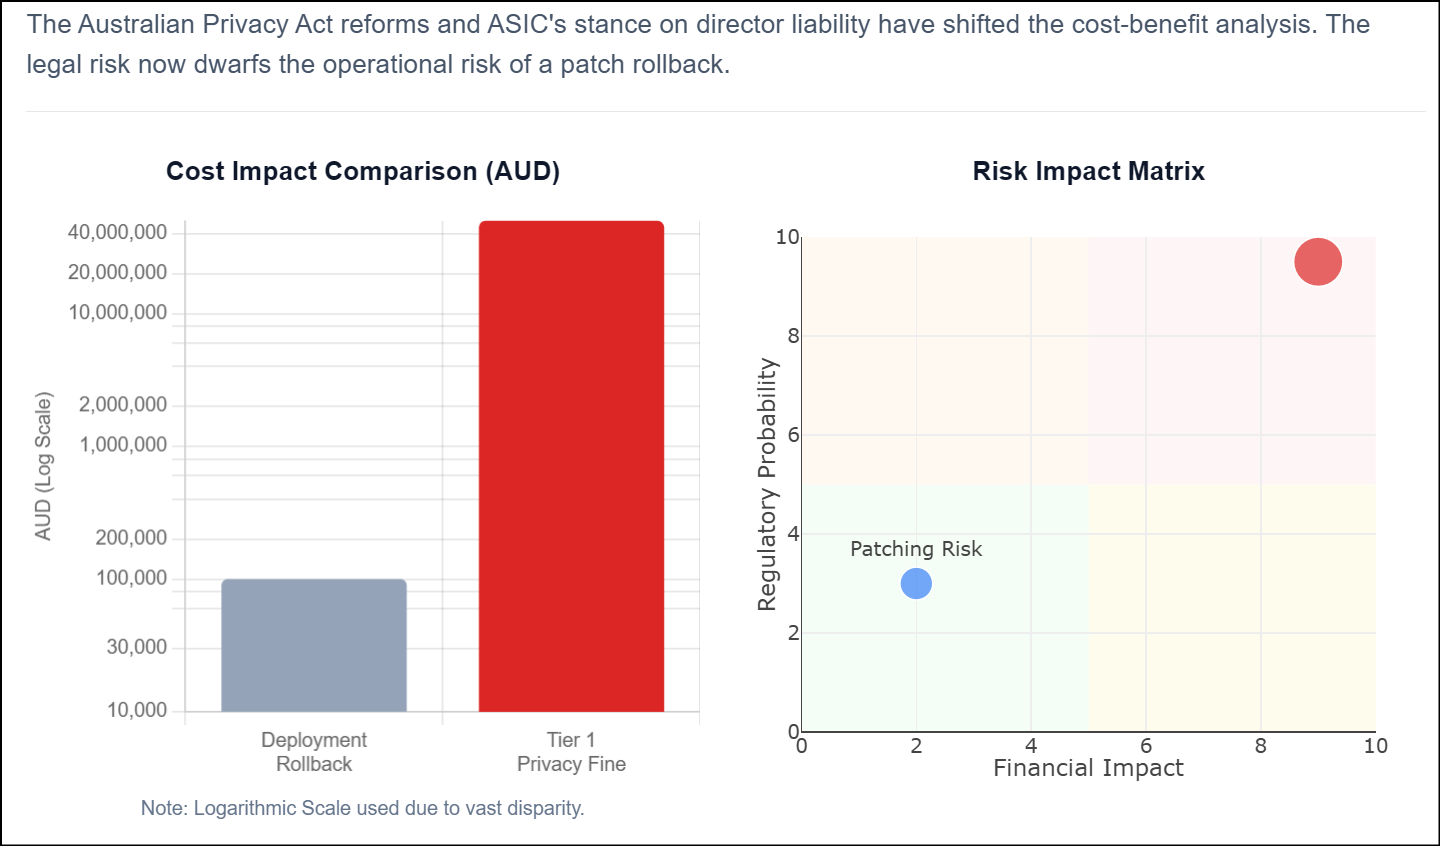
Privacy Act Reforms: "Serious interference" with privacy now costs $50 million. This penalty also applies to 30% of adjusted turnover. SessionReaper exposes customer data, creating this exact risk.
ASIC Director Liability: ASIC states that cyber resilience is a duty. Directors face personal liability for low care. Ignoring this flaw due to a "Code Freeze" helps prove negligence.
The Black Friday Dilemma: Freeze or Patch?
The "Hard Freeze" used to be standard. No changes during sales events ensured stability.
SessionReaper destroys this logic.
Sansec reports that 62% of Magento stores are unsafe. Attackers scan for these systems. A breach means attackers steal credit cards via Magecart. They could also lock your database with ransomware on Cyber Monday.
Key Takeaway: A deployment error costs money. A Tier 1 Privacy fine threatens your business survival.
Technical Deep Dive: How the Exploit Works
To understand the risk, we must look at the code. SessionReaper exploits PHP Object Injection.
The Mechanics of Failure
Data Packing: Apps turn complex data (objects) into strings to store them.
The Flaw: Adobe Commerce accepts this data from the API without checking it.
The Trigger: When the app reads (unpacks) this string, it wakes up the data object.
Gadget Chains: Attackers chain together code snippets (gadgets) already on your system.
Attackers change these gadgets to trick the server. This lets them delete files or run commands. This happens before the system checks for a login.
Why Standard Defences Fail
Firewalls often miss this. The attack looks like valid data. Your security controls must specifically check packed strings to stop it.
Strategic Response: The "Monitored Thaw"
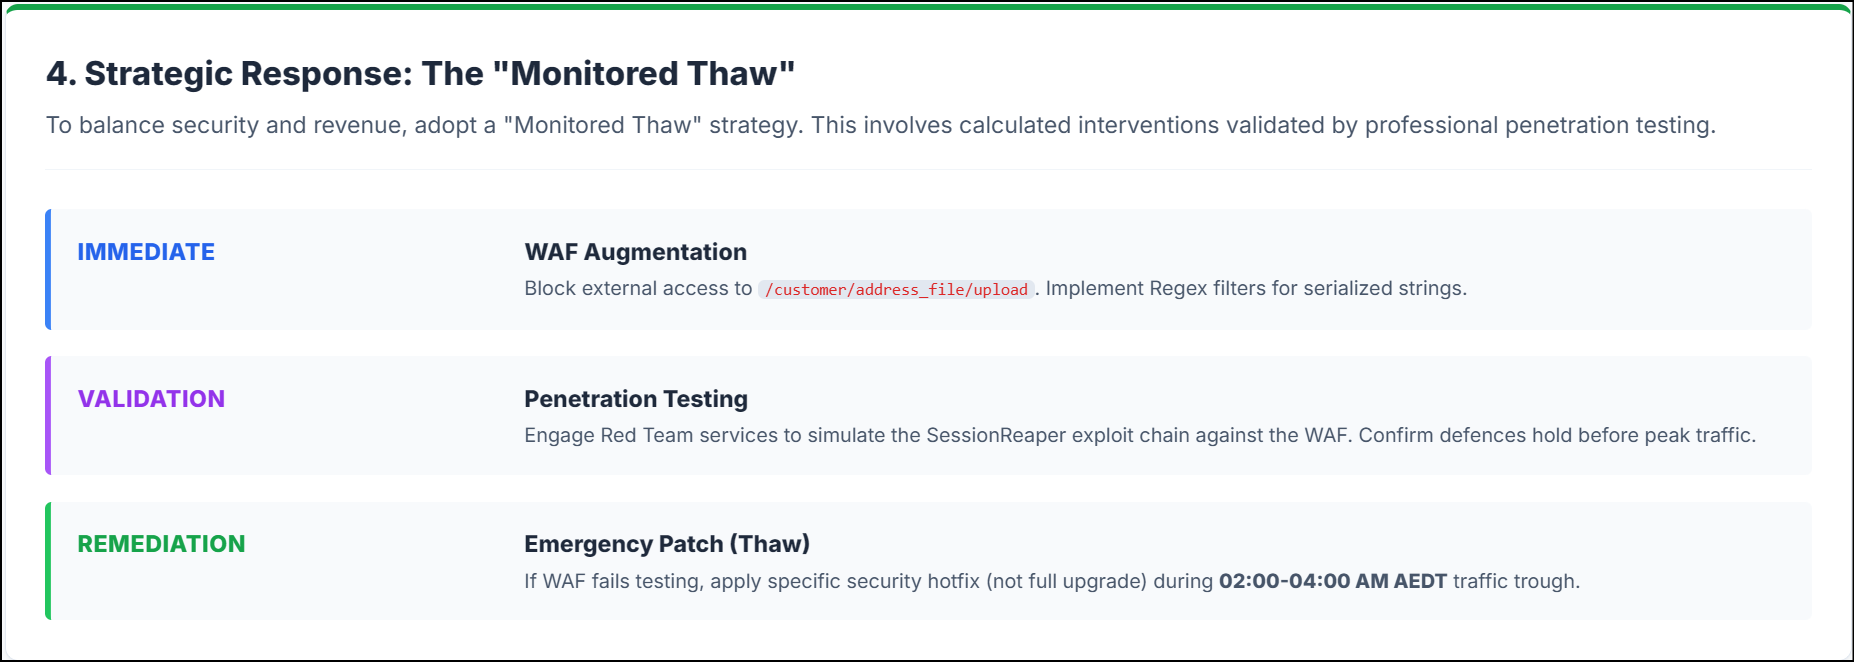
You cannot afford to ignore this. Yet, you cannot break your store during the busiest week. We recommend a "Monitored Thaw" strategy.
1. WAF Update (Immediate)
If you cannot patch now, block the attack. Configure your Web Application Firewall (WAF) to:
Block outside access to
/customer/address_file/upload.Filter requests that look like packed data (e.g., regex matching
O:\d+:).
2. Validate with Penetration Testing Services
Applying a rule is not enough; you must check if it works. Penetration testing services are vital here. A Red Team should:
Simulate real world attacks using the SessionReaper exploit.
Test if attackers can bypass your WAF rules.
Find other security weaknesses exposed by rushed changes.
Types of penetration tests needed include API testing. This proves your shields work against determined attackers.
3. The Emergency Patch
If the WAF fails, you must patch.
Isolate the Fix: Apply only the security patch. Do not upgrade the full version.
Timing: Deploy when traffic is low (typically 02:00 - 04:00 AM AEST).
Verification: Use automated tests to check checkout functions immediately.
4. Governance and Documentation
Document your choices. If a breach happens, you must prove you managed the cyber security risk. A test report proves you took reasonable steps.
Conclusion: Silence is not Security
"SessionReaper" is a clear danger. Attackers are automated. Regulators are watching.
Do not let an old "Code Freeze" policy cause a $50 million fine.
Is your WAF actually blocking SessionReaper? Are you sure?
Contact our Red Team today for a targeted web application assessment. We will validate your defences against CVE-2025-54236. We help secure your revenue without risking your reputation.

Daily Threat Briefing: Australia – 26 November 2025
The last 24 hours have seen a significant escalation in the Australian cyber threat landscape, characterised by a convergence of AI-driven offensive operations and high-impact data breaches. The Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC) and private sector intelligence indicate a sharp rise in automated attacks targeting the Healthcare, FinTech, and Government sectors. Of particular concern is the emergence of AI agents capable of automating complex attack chains, reducing the time from vulnerability discovery to exploitation to near zero.
Executive Summary
The last 24 hours have seen a significant escalation in the Australian cyber threat landscape, characterised by a convergence of AI-driven offensive operations and high-impact data breaches. The Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC) and private sector intelligence indicate a sharp rise in automated attacks targeting the Healthcare, FinTech, and Government sectors.
Of particular concern is the emergence of AI agents capable of automating complex attack chains, reducing the time from vulnerability discovery to exploitation to near zero.
Top Story: The Rise of AI-Driven Offensive Campaigns
Threat Actor Activity: A sophisticated campaign, tracked as GTG-1002, has been identified targeting Australian finance and government sectors. Unlike traditional attacks, this campaign utilises an AI agent to automate reconnaissance, exploit writing, and lateral movement.
- Impact: The window for patching has effectively closed for some zero-day vulnerabilities.
- Sector Risk: High for Government and Critical Infrastructure.
Sector-Specific Updates
1. Healthcare
The healthcare sector remains the primary target for ransomware and data extortion.
- Incident: Point Lonsdale Medical Group in Victoria has disclosed a cyber attack resulting in unauthorised access to personal information. This follows closely on the heels of the Genea breach, where the Termite ransomware group (an offshoot of Babuk) claimed responsibility for exfiltrating 700GB of patient data.
- Threat: Attackers are aggressively targeting patient management systems and third-party integrations.
2. Aviation & eCommerce
- Major Incident: Qantas Airways is reportedly investigating a significant data compromise affecting customer personal data. Threat intelligence suggests potential involvement from the Scattered Spider group, known for sophisticated social engineering and targeting large helpdesks.
- Implication: Organisations with large customer databases must urgently review their identity verification processes for customer support channels.
3. FinTech & SaaS
- Vulnerability: A critical flaw in WhatsApp’s Contact Discovery API has been exposed, potentially allowing the enumeration of active accounts. While Meta has implemented fixes, this highlights a broader risk for FinTech apps relying on similar contact syncing features.
- Trend: API Security is a critical failure point. Financial services are currently facing a wave of API-layer DDoS attacks and credential stuffing, exploiting endpoints that lack adaptive multi-factor authentication (MFA).
- SaaS Alert: A "Loan Management System" source code leak has been detected, compromising API keys and database credentials. SaaS providers are urged to rotate secrets immediately.
4. Education & EdTech
- Ongoing Threat: Following the Western Sydney University breach, threat actors are leveraging stolen credentials to target other educational institutions. Phishing campaigns impersonating university IT support are currently active.
5. IoT & Critical Infrastructure
- Advisory: A new report from Semperis highlights that 52% of ransomware attacks in Australia now occur on weekends or holidays, exploiting reduced staffing in Security Operations Centres (SOCs).
- Vulnerability: Unpatched IoT devices in critical infrastructure are being targeted by state-sponsored actors to maintain persistence.
Critical Vulnerabilities & Exploits (Last 24 Hours)
- Microsoft WSUS (CVE-2025-59287): A critical vulnerability allowing privilege escalation. The ACSC has issued a high-priority alert for immediate patching.
- Citrix NetScaler (CVE-2025-5777): "Citrix Bleed 2" is being actively exploited in the wild to bypass authentication.
- Cisco ISE (CVE-2025-20337): Exploited as a zero-day to deploy custom malware.
- Samsung (CVE-2025-21042): A zero-day in image processing libraries is being used in targeted spyware campaigns via instant messaging apps.
Recommendations
- Patch Immediately: Prioritise Microsoft WSUS and Citrix NetScaler updates.
- API Hardening: Review all external API endpoints for rate limiting and broken object level authorisation (BOLA).
- Enhance Monitoring: Increase SOC vigilance during the upcoming weekend to counter "holiday-timed" ransomware attacks.
- AI Defence: Begin evaluating AI-enabled defensive tools to counter the speed of automated AI attacks.
Contact us for a quote for penetration testing service or adversary simulation.

Daily Threat Briefing: Record DDoS Hits Australia & Critical Fortinet Flaws
In the last 24 hours, the Australian cyber threat landscape has been dominated by a record-breaking Distributed Denial of Service (DDoS) attack targeting local cloud infrastructure, alongside critical alerts for widely used enterprise edge devices. The Australian Securities and Investments Commission (ASIC) has also signalled a major shift in regulatory enforcement regarding cyber resilience in the financial sector.
Executive Summary In the last 24 hours, the Australian cyber threat landscape has been dominated by a record-breaking Distributed Denial of Service (DDoS) attack targeting local cloud infrastructure, alongside critical alerts for widely used enterprise edge devices. The Australian Securities and Investments Commission (ASIC) has also signalled a major shift in regulatory enforcement regarding cyber resilience in the financial sector.
Top Story: Australian Cloud Endpoint Hit by Record 15.72 Tbps DDoS Microsoft has disclosed the mitigation of the largest DDoS attack ever observed in the cloud, targeting a single endpoint in Australia. The attack peaked at a staggering 15.72 Terabits per second (Tbps).
- Attack Vector: The assault originated from a "TurboMirai-class" IoT botnet known as AISURU, comprising approximately 300,000 infected devices (routers, cameras, and DVRs).
- Pentester Insight: This incident highlights the critical volatility of insecure IoT devices. For organisations relying on cloud infrastructure, this underscores the necessity of stress-testing DDoS mitigation strategies and ensuring upstream providers can handle volumetric attacks of this magnitude.
Vulnerability Watch: Active Exploitation in the Wild Two critical vulnerability sets have emerged that require immediate patching and threat hunting.
Fortinet FortiWeb (Web Application Firewall):
- CVE-2025-64446 (Critical): A path-traversal flaw allowing unauthenticated administrative access.
- CVE-2025-58034 (Medium - Actively Exploited): An OS Command Injection vulnerability.
- The Threat: Attackers are chaining these vulnerabilities to bypass authentication and execute arbitrary code on the underlying system. Given FortiWeb's position at the network edge, compromise here grants threat actors deep visibility into decrypted web traffic.
- Action: Patch to version 8.0.2 immediately.
7-Zip (RCE):
- CVE-2025-11001: A Remote Code Execution (RCE) vulnerability in the ubiquitous 7-Zip file archiver is under active exploitation.
- Risk: This client-side vulnerability is a prime vector for phishing campaigns targeting corporate endpoints.
Sector-Specific Intelligence
Government: Security protocols at Parliament House have been tightened significantly during the current visit by a Chinese delegation. Politicians and staff have been instructed to power down devices and disable Wi-Fi to mitigate the risk of close-access cyber espionage. This serves as a stark reminder of the physical proximity risks to mobile devices in sensitive environments.
FinTech & SaaS: ASIC Enforcement Shift: ASIC is suing financial advice firm Fortnum Private Wealth for "licensee failures to have adequate cyber security protections." This marks a pivot where regulatory bodies are moving from guidance to prosecution for poor cyber hygiene. API Security: New data reveals that financial services now account for 27% of API-specific DDoS traffic. Attackers are moving beyond simple volumetric attacks to application-layer exhaustion, targeting specific expensive API endpoints to disrupt operations.
Healthcare: The sector remains Australia's most targeted industry, sustaining 17% of all reported cyber attacks. The focus continues to be on data extortion via ransomware, leveraging the high sensitivity of patient data (PII/PHI).
AI Systems: Research released today indicates that AI coding assistants, specifically DeepSeek, have been observed generating code with introduced vulnerabilities when prompted with specific political triggers. This "poisoning" of the development lifecycle introduces a new vector for supply chain attacks in software development.
Recommendation for Defenders Organisations should immediately audit their external attack surface for exposed Fortinet appliances and verify the integrity of their 7-Zip installations. Furthermore, FinTech entities must review their API rate-limiting configurations to defend against the rising tide of application-layer DDoS attacks.
Contact us for a quote for penetration testing service or adversary simulation.