
Scanning Smarter: How Managed Web Vulnerability Scanning Detects What Traditional Tools Miss
Discover how Lean Security’s managed web vulnerability scanning detects threats traditional tools miss, delivering stronger protection for businesses.
When it comes to protecting your business from cyber threats, knowing where you’re vulnerable is half the battle. Many organisations rely on traditional web vulnerability scanners to uncover weaknesses in their applications. While these tools can be useful, they often produce incomplete results, leaving blind spots that hackers are eager to exploit.
This is where managed web vulnerability scanning changes the game. Instead of relying on automated tools alone, managed scanning combines cutting-edge technology with expert oversight, ensuring threats are identified, validated, and prioritised with far greater accuracy.
This blog will discuss the shortcomings of traditional vulnerability scanners, what makes managed scanning different, and why businesses serious about cybersecurity are shifting toward a managed approach.
1. The Limitations of Traditional Vulnerability Scanners
Automated scanners are often the first line of defence for businesses because they are:
· Easy to deploy
· Relatively inexpensive
· Capable of scanning large volumes of assets quickly
However, they are far from foolproof. Common problems include:
False Positives and Negatives: Automated tools frequently flag harmless issues as critical while overlooking real vulnerabilities that don’t fit their signature patterns.
Surface-Level Analysis: Many scanners only scratch the surface, missing vulnerabilities hidden deeper in the application architecture.
One-Size-Fits-All Results: Reports are often generic, leaving IT teams with long lists of vulnerabilities but no clear guidance on prioritisation.
For organisations that depend solely on these tools, the result is often wasted time chasing non-issuesora false sense of security.
2. What Managed Web Vulnerability Scanning Offers
Managed security services elevate the process by combining automated scanning with expert analysis, contextual insights, and actionable reporting. Rather than leaving teams overwhelmed with raw scan data, managed services provide clarity and direction.
Key benefits include:
Expert Validation: Human experts review scan results to confirm real vulnerabilities and weed out false positives.
Prioritisation: Instead of a laundry list of issues, businesses receive clear guidance on which vulnerabilities pose the most risk.
Continuous Monitoring: Threats evolve quickly. Managed scanning ensures new vulnerabilities are detected as they emerge, not just during scheduled scans.
This approach transforms vulnerability scanning from a checklist item into a proactive defence mechanism.
3. Detecting What Traditional Tools Miss
So, what exactly does managed scanning catch that traditional tools overlook?
Business Logic Flaws: Automated scanners aren’t great at identifying vulnerabilities in workflows, like checkout processes or user authentication flows, which attackers can exploit.
Context-Specific Risks: Managed services understand your business environment, allowing them to assess vulnerabilities within the context of your applications, users, and data.
Emerging Threats: Experts keep pace with new attack techniques and can update scanning approaches faster than static tools.
Configuration Weaknesses: Automated tools often miss subtle misconfigurations in servers, APIs, or third-party integrations that could expose sensitive data.
By pairing automation with human intelligence, managed scanning uncovers the risks that would otherwise slip through the cracks.
4. Reducing Noise with Actionable Reporting
One of the biggest frustrations with traditional scanning tools is the overwhelming amount of raw data they generate. IT teams are left with:
· Dozens (or even hundreds) of findings
· Unclear risk levels
· No actionable next steps
Managed scanning solves this by providing tailored reporting. Instead of handing you a generic PDF full of technical jargon, managed services deliver concise, actionable insights:
· Which vulnerabilities are critical right now
· What steps are needed to remediate them
· How issues map to compliance requirements
This level of clarity empowers businesses to act faster and more confidently.
5. The Role of Human Expertise
Cybersecurity isn’t just a technology problem—it’s a people problem. Attackers exploit human error, misconfigurations, and overlooked vulnerabilities that machines can’t always catch.
Managed vulnerability scanning integrates the expertise of seasoned security professionals who:
· Stay updated on the latest threats and techniques
· Interpret scan results in the context of your environment
· Advise on both quick fixes and long-term strategies
In other words, you don’t just get a scan—you get a partner who understands your business and helps you stay secure.
6. Compliance and Regulatory Benefits
For many organisations, compliance is just as important as security. Regulatory frameworks like PCI DSS, HIPAA, and GDPR require regular vulnerability assessments.
Traditional scanners may check the box, but managed scanning ensures you:
· Generate audit-ready reports
· Demonstrate due diligence with expert validation
· Align vulnerability management with industry regulations
This not only helps avoid fines but also builds trust with customers, partners, and stakeholders.
7. Scaling Security with Your Business
As businesses grow, so does their attack surface. More applications, more integrations, and more data mean more opportunities for attackers.
Traditional scanners struggle to scale effectively in dynamic environments. Managed scanning, however, adapts seamlessly by:
· Providing flexible scanning schedules
· Covering cloud-based, hybrid, and on-premises environments
· Adjusting priorities as your business evolves
This ensures security isn’t left behind as your company scales.
8. Cost vs. Value: The Real ROI
At first glance, traditional vulnerability scanners may seem cheaper than managed services. But when you factor in:
· The cost of wasted time chasing false positives
· Potential losses from overlooked vulnerabilities
· Regulatory fines for compliance failures
The real return on investment favours managed scanning. By reducing risk and saving internal resources, managed services often pay for themselves many times over.
9. Why Lean Security’s Managed Web Vulnerability Scanning Stands Out
Not all managed services are created equal. At Lean Security, our approach goes beyond basic scanning:
Advanced Detection Tools: We leverage leading-edge technology to identify vulnerabilities that traditional tools miss.
Expert Analysis: Our team validates results to eliminate noise and highlight what matters most.
Tailored Reporting: Actionable insights help you focus on real threats, not false alarms.
Ongoing Support: We partner with you every step of the way, from detection to remediation.
Our mission is to provide smarter scanning that empowers businesses to stay secure in an ever-changing digital landscape.
Take Your Business to the Next Level
Don’t let traditional tools leave blind spots in your security strategy. Lean Security’s managed web vulnerability scanning combines advanced automation with expert oversight to uncover threats other scanners miss. From business logic flaws to configuration weaknesses, we provide actionable insights that protect your applications and your reputation.

Discover how managed web vulnerability scanning enhances cybersecurity by detecting flaws traditional tools miss. This infographic highlights expert oversight, real threat validation, actionable reporting, regulatory compliance, and human expertise—helping businesses reduce risks and secure systems with continuous monitoring.
Whether you’re aiming for stronger compliance or simply want peace of mind, our team ensures vulnerabilities are identified, validated, and addressed before attackers can exploit them. Secure your applications smarter with our penetration testing services. Contact Lean Security today and take the guesswork out of vulnerability scanning.

The Rise of Managed Security Services: Why DIY Cybersecurity No Longer Works
Discover why DIY cybersecurity no longer works and how managed security services deliver advanced protection, compliance, and 24/7 monitoring.
Nowadays, cyber threats evolve faster than most businesses can keep up. Hackers are no longer lone actors experimenting in basements — they’re highly organised, well-funded groups leveraging advanced techniques. For small and mid-sized businesses, trying to handle cybersecurity with a DIY approach has become not only impractical but downright dangerous.
The truth is simple: the stakes are higher, the risks are greater, and cybercriminals are more sophisticated than ever. Businesses that rely on in-house patchwork solutions often find themselves underprepared when faced with ransomware attacks, phishing campaigns, or data breaches.
This is why companies are increasingly turning to managed security services providers(MSSPs). These experts bring advanced tools, 24/7 monitoring, and deep industry expertise to safeguard businesses against modern threats. Let’s break down why DIY cybersecurity no longer works and why the rise of managed security services is no coincidence.
1. The Growing Sophistication of Cyber Threats
Cyberattacks today aren’t just random brute-force attempts. Threat actors now use artificial intelligence, machine learning, and automation to exploit vulnerabilities at lightning speed. A single weak password, an unpatched system, or an overlooked misconfiguration can give attackers an entry point.
For businesses relying on DIY cybersecurity, it’s nearly impossible to match the sophistication of these attackers. Even with antivirus software or firewalls in place, gaps remain, and those gaps are exactly where hackers strike.
MSSPs specialise in identifying and neutralising these advanced threats before they cause damage, using threat intelligence feeds and proactive monitoring that most businesses can’t maintain on their own.
2. The Hidden Costs of DIY Security
At first glance, handling security in-house might look like a way to save money. But in reality, the hidden costs of DIY cybersecurity can be overwhelming:
· Downtime expenses when systems are compromised.
· Regulatory fines for non-compliance with data protection laws.
· Reputational damage that drives customers away.
· Recovery costs for breach investigations and system rebuilds.
MSSPs help businesses avoid these financial pitfalls by reducing risk, improving compliance, and ensuring that breaches are detected and contained quickly.
3. Shortage of Skilled Cybersecurity Talent
Cybersecurity isn’t something any IT generalist can handle anymore. With more than 3.5 million unfilled cybersecurity jobs worldwide, finding and retaining top talent is harder than ever. For small businesses, hiring a full-time security operations team is simply unrealistic.
MSSPs solve this problem by giving businesses access to highly trained professionals who live and breathe cybersecurity. This way, companies get enterprise-level expertise without the cost and stress of recruiting, training, and retaining specialists.
4. Compliance and Regulatory Pressures
From GDPR in Europe to HIPAA in healthcare and PCI DSS in finance, compliance requirements are growing stricter across industries. Businesses that fail to meet these standards face heavy fines and legal consequences.
DIY security often misses the mark when it comes to compliance because most in-house teams lack the depth of knowledge required to meet evolving standards. MSSPs bring structured processes, compliance reporting, and audit support, helping businesses stay ahead of regulations and avoid penalties.
5. The Importance of 24/7 Monitoring
Cybercriminals don’t work 9-to-5. Attacks can strike at midnight, during holidays, or over weekends, the times when in-house IT staff aren’t watching. That’s when breaches go unnoticed and damages multiply.
MSSPs operate Security Operations Centres (SOCs) that monitor client environments around the clock. Every unusual activity is flagged, investigated, and acted upon immediately, reducing response times and minimising the impact of attacks.
6. Scalability and Flexibility
As businesses grow, so do their cybersecurity needs. A DIY setup that works for a small office can quickly crumble under the weight of new devices, cloud environments, and remote workers.
MSSPs scale effortlessly. Whether your business expands to new locations, adopts hybrid work models, or migrates to the cloud, managed security services adapt and evolve without requiring huge investments in new infrastructure or staff.

7. Proactive vs. Reactive Security
DIY cybersecurity often means reacting to problems after they happen, patching vulnerabilities once they’re exploited or cleaning up after a phishing attack succeeds.
MSSPs flip the script with a proactive approach. Using threat hunting, advanced analytics, and continuous vulnerability assessments, they identify risks before they turn into incidents. This shift from reaction to prevention is what keeps modern businesses safe.
8. Advanced Tools Beyond DIY Budgets
Sophisticated security tools, like endpoint detection and response (EDR), Security Information and Event Management (SIEM) systems, and threat intelligence platforms, are costly and complex to manage.
Most small to mid-sized businesses can’t afford these solutions on their own. MSSPs, however, spread the cost across clients, making cutting-edge technology accessible to businesses of all sizes.
9. The Human Element: Training and Awareness
Cybersecurity isn’t just about firewalls and software; human error is still one of the top causes of breaches. Employees click on phishing emails, download malicious attachments, or reuse weak passwords.
MSSPs often include employee training and phishing simulations as part of their service, ensuring that people, not just technology, become a strong line of defence.
10. Business Continuity and Incident Response
When a breach happens, response time is everything. Businesses without a clear incident response plan often lose valuable hours (or days) figuring out what to do.
MSSPs provide structured incident response strategies, forensic investigations, and business continuity planning. This ensures downtime is minimised, systems are restored quickly, and evidence is preserved for compliance or legal requirements.
11. Rising Ransomware Threats
Ransomware has exploded in recent years, targeting businesses of all sizes. Attackers don’t just encrypt data anymore — they also steal it and threaten to leak it unless payment is made.
DIY defences like basic backups aren’t enough against these sophisticated double-extortion tactics. MSSPs combine layered defences, secure backup strategies, and rapid recovery capabilities to protect against ransomware and minimise damage.
12. Why Businesses Are Making the Shift
Ultimately, businesses are recognising that DIY security is too risky, too costly, and too limited in scope. The rise of Managed Security Services reflects a broader reality: cybersecurity has become mission-critical.
With MSSPs, companies gain not only better protection but also peace of mind. Instead of constantly worrying about the next breach, leaders can focus on growth, innovation, and serving customers, knowing their security is in expert hands.
Lean Security: Your Trusted Partner in Managed Security
At Lean Security, we understand that the cybersecurity landscape is evolving at a pace businesses can’t match on their own. That’s why we provide comprehensive managed security services tailored to your unique environment. From 24/7 monitoring and compliance support to advanced threat detection and incident response, our team of experts ensures you’re always one step ahead of cybercriminals.
Don’t let outdated DIY approaches put your business at risk. With Lean Security as your managed services provider, you gain a dedicated partner focused on protecting your operations, your reputation, and your bottom line.
Ready to leave DIY behind and embrace a smarter, safer approach to cybersecurity? Contact Lean Security today to learn how our penetration testing services can transform your business’s defences.
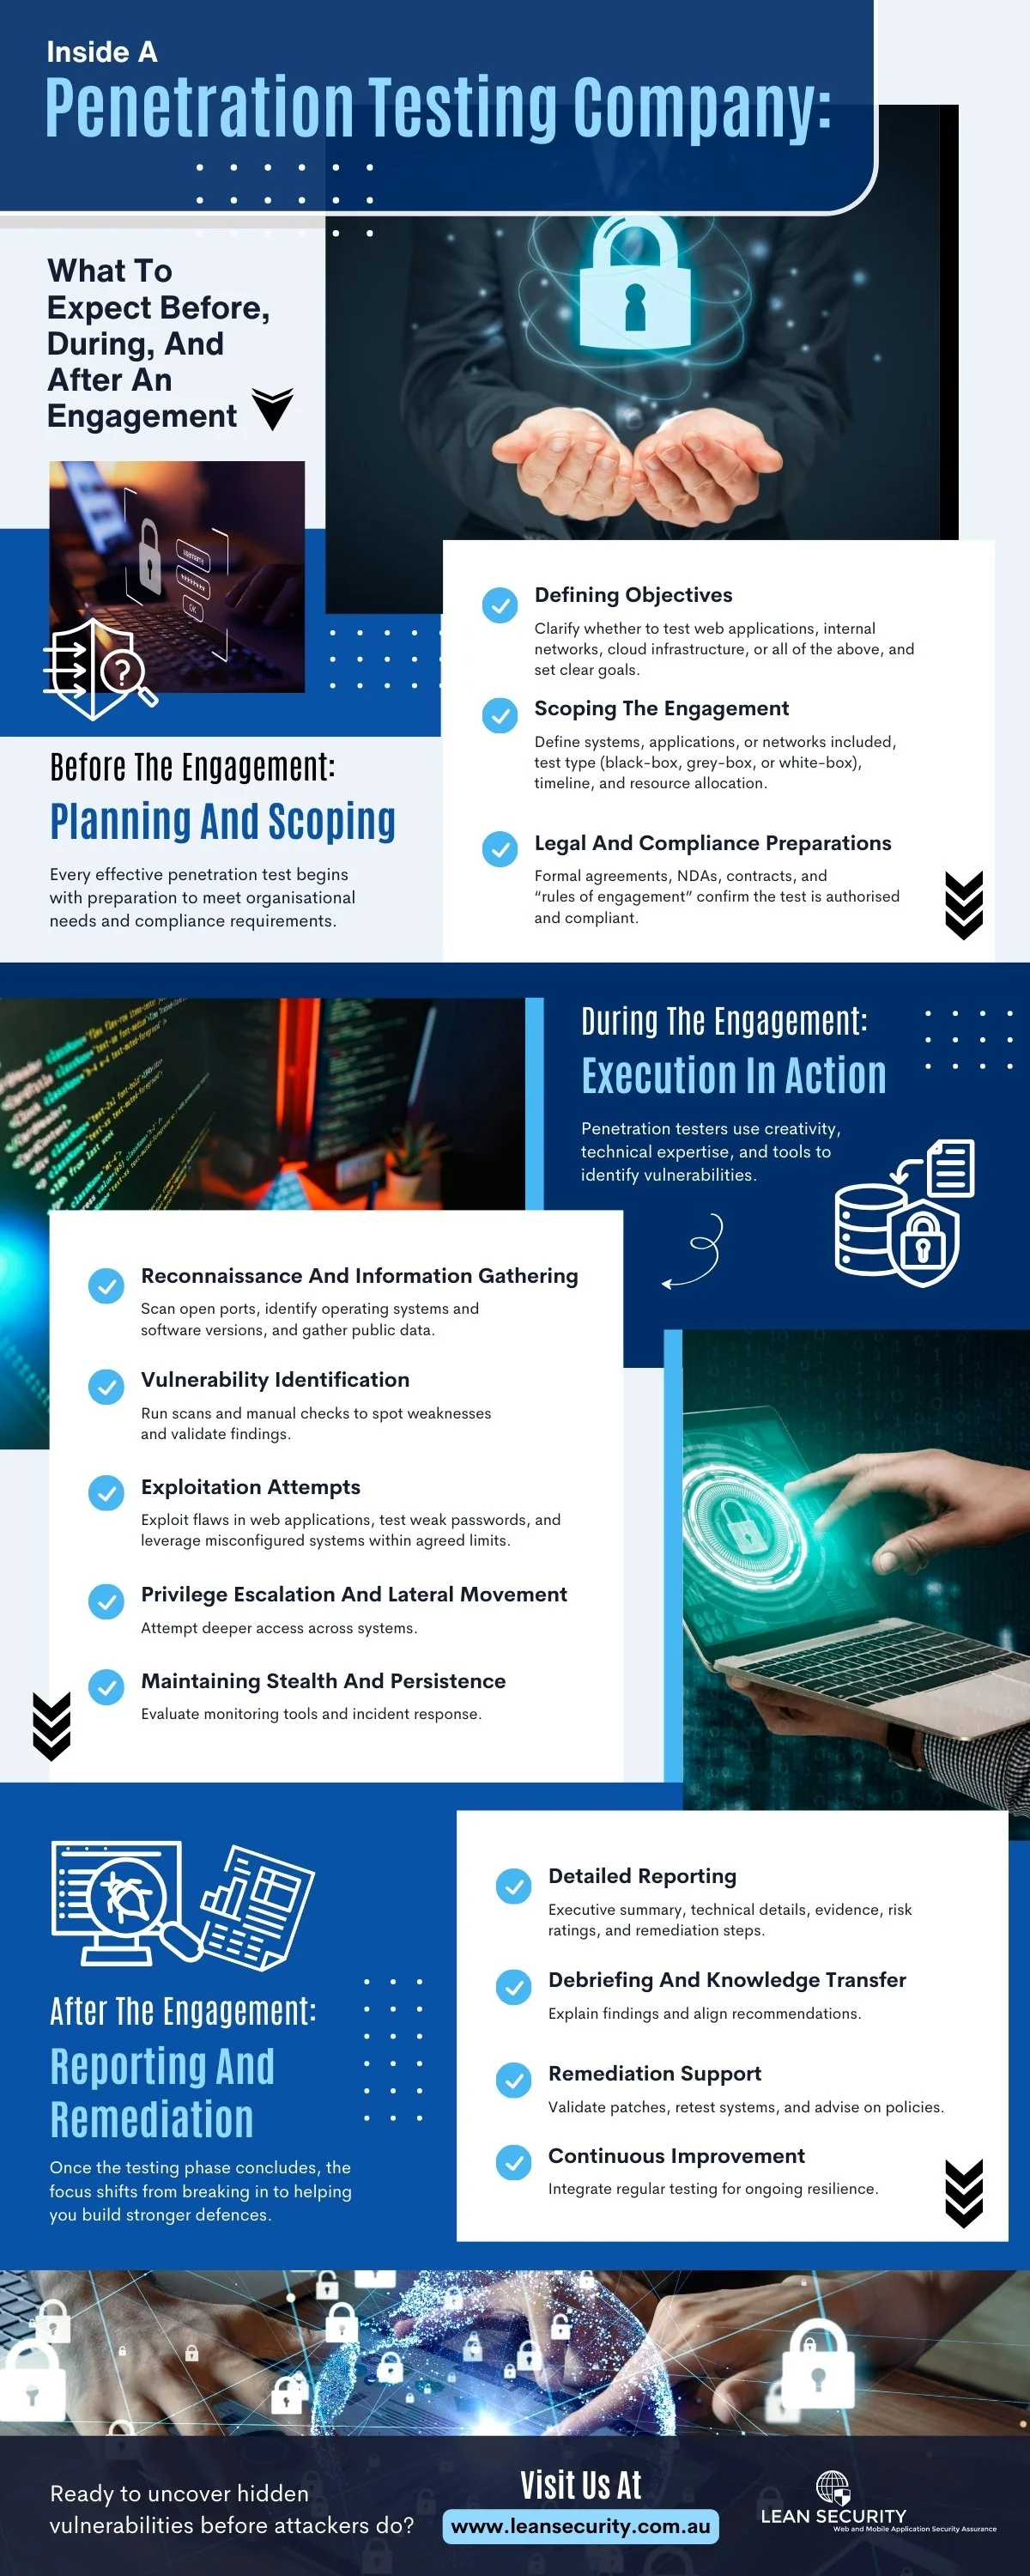
Inside a Penetration Testing Company: What to Expect Before, During, and After an Engagement
Discover what happens before, during, and after penetration testing. Learn how penetration testing companies strengthen defences.
When it comes to enhancing cybersecurity, penetration testing isn’t just a checkbox — it’s a critical process that reveals how secure your digital environment really is. Many businesses know the term “pen test,” but few understand what actually goes on behind the scenes at a penetration testing company.
So, what should you expect when you partner with a penetration testing provider? Let’s break down the process step by step, before, during, and after the engagement, so you know exactly how these companies work to safeguard your systems.
Before the Engagement: Planning and Scoping
Every effective penetration test begins with preparation. This stage ensures the engagement aligns with your organisation’s needs and compliance requirements.
1. Defining Objectives
The company will work closely with you to clarify the goals of the test. Do you want to test your web applications, internal network, cloud infrastructure, or all of the above? Are you aiming for compliance or strengthening defences proactively? Clear objectives drive the scope.
2. Scoping the Engagement
A detailed scope ensures the test targets relevant systems without disrupting business operations. Expect to define:
· The systems, applications, or networks included
· Whether the test will be black-box (no prior knowledge), grey-box (partial knowledge), or white-box (full access)
· Timeline and resource allocation
3. Legal and Compliance Preparations
Penetration testing requires formal agreements to avoid misunderstandings. Non-disclosure agreements (NDAs), contracts, and “rules of engagement” documents protect both the company and the client. This step confirms the test is authorised and compliant with regulatory standards.
During the Engagement: Execution in Action
This is where the real work begins. Penetration testers combine creativity, technical expertise, and industry tools to identify vulnerabilities just as an attacker would.
4. Reconnaissance and Information Gathering
Pen testers start by collecting as much information as possible. This may include:
· Scanning open ports
· Identifying operating systems and software versions
· Gathering publicly available data
Recon is about mapping the attack surface before attempting to breach it.
5. Vulnerability Identification
Next, testers run scans and manual checks to spot weaknesses. Automated tools flag potential issues, but skilled testers validate findings to avoid false positives.
6. Exploitation Attempts
Here’s where the engagement gets interesting. Testers attempt to exploit vulnerabilities to gain access. This may involve:
· Exploiting web application flaws (SQL injection, XSS, and authentication bypass)
· Testing weak password policies
· Leveraging misconfigured systems
While real-world attack techniques are used, testers operate within agreed boundaries to prevent actual damage.
7. Privilege Escalation and Lateral Movement
If access is achieved, testers often attempt to escalate privileges or move laterally across systems. This demonstrates how an attacker could deepen their control within your environment.
8. Maintaining Stealth and Persistence
Some engagements include testing whether attackers could remain undetected. This evaluates monitoring tools, intrusion detection systems, and incident response capabilities.
After the Engagement: Reporting and Remediation
Once the testing phase concludes, the focus shifts from breaking in to helping you build stronger defences.
9. Detailed Reporting
Expect a comprehensive report that includes:
· Executive summary for leadership teams
· Technical details for IT staff
· Evidence of exploited vulnerabilities
· Risk ratings for each issue
· Actionable remediation steps
The best penetration testing companies translate complex technical findings into clear, prioritised insights for decision-makers.
10. Debriefing and Knowledge Transfer
A good provider doesn’t just hand you a report and walk away. They schedule a debriefing session to explain findings, answer questions, and align recommendations with your business context.
11. Remediation Support
After identifying weaknesses, companies often support remediation efforts. This could mean validating patches, retesting systems, or advising on security policies. The goal is to ensure fixes are not only applied but also effective.
12. Continuous Improvement
Penetration testing isn’t a one-time exercise. Leading companies encourage clients to integrate regular testing into their security strategy, aligning with compliance requirements (like PCI DSS or ISO 27001) and evolving cyber threats.
Behind the Scenes: What Sets Penetration Testing Companies Apart
Not all penetration testing providers are the same. Here are qualities that separate the best from the rest:
Expertise Beyond Tools: While automated tools help, skilled testers rely on creativity, experience, and human insight.
Industry-Specific Knowledge: Financial, healthcare, and retail sectors face different risks. Specialised knowledge ensures testing is relevant.
Clear Communication: The best firms simplify technical details, making results actionable for executives and IT teams alike.
Adaptability: Cyber threats evolve quickly. Strong companies continuously update methodologies to mimic current attack techniques.
Why This Process Matters
Understanding what happens before, during, and after a penetration test gives you confidence in the process. It also highlights why working with an experienced penetration testing company is so valuable: they don’t just find vulnerabilities; they help you close them and strengthen your overall security posture.
The Role of Collaboration Between Client and Tester
Penetration testing is not a one-sided effort. While the testers bring technical expertise and attacker-like creativity, the client’s role is equally important in shaping the outcome. Effective collaboration begins during the scoping stage and continues throughout the engagement. Your IT and security teams provide valuable insights into business priorities, critical systems, and operational concerns that help testers focus their efforts.
Clear communication also ensures the testing process doesn’t disrupt normal business operations. For example, scheduling tests during off-peak hours or identifying systems that cannot be interrupted minimises operational risks. When clients and testers work hand in hand, the results are not only more accurate but also more relevant to the organisation’s unique environment.
Turning Insights Into Long-Term Security Strategy
The end of a penetration test should mark the beginning of a stronger security journey. Too often, organisations view the final report as a checklist of fixes. In reality, the findings provide a roadmap for building long-term resilience.
By analysing recurring vulnerabilities and common weaknesses, businesses can identify patterns that point to deeper issues, such as insufficient staff training, outdated patching processes, or weak access controls. Penetration testing companies often highlight these themes and advise on preventative measures that go beyond immediate remediation.
When leveraged strategically, penetration test insights can influence policy decisions, guide investments in new technologies, and strengthen incident response readiness. Instead of reacting to individual vulnerabilities, organisations build a proactive security culture that evolves with the threat landscape.
Leading Penetration Testing Company
At Lean Security, we believe penetration testing should be more than a technical exercise — it should empower your business with clarity, protection, and confidence. Our expert team guides you through every stage of the process, from vulnerability scanning to web application security, ensuring your systems are tested against real-world attack techniques without unnecessary disruption.
Whether you’re preparing for compliance, defending sensitive data, or strengthening customer trust, Lean Security delivers results that go beyond reports. Don’t leave your organisation exposed to unknown risks. Partner with Lean Security today and take proactive steps toward a more resilient security posture.
Reach out now.

ACSC HIGH ALERT: Your CI/CD Pipeline is the New Frontline. Are You Prepared for a Supply Chain Attack?
The ACSC has issued a high alert on attacks against Australia's software supply chain. Adversaries are no longer just targeting your live systems; they are infiltrating the "factory" where your software is built. We simulate these advanced, multi-stage attacks to validate your defences against this critical threat.
Executive Summary: The Australian Cyber Security Centre (ACSC) has issued a high-level alert on the active targeting of online code repositories, signaling a strategic shift by adversaries towards Australia's software supply chain. Threat actors are no longer just attacking production systems; they are infiltrating the very "factory" where your software is built, turning trusted applications into delivery mechanisms for catastrophic breaches. This report deconstructs this evolving threat, analyses the multi-million dollar business impact, and outlines how adversary simulation is the only effective method to validate your defences against a compromise of your CI/CD pipeline.
Understanding the Threat: A New Battleground
The traditional cybersecurity paradigm focused on defending the perimeter—the hardened walls around production environments. However, a recent high-level alert from the Australian Signals Directorate's Australian Cyber Security Centre (ACSC) confirms a fundamental shift in the threat landscape. Adversaries are moving upstream, targeting the soft underbelly of modern enterprise: the software development lifecycle (SDLC).
The ACSC explicitly warns of the "ongoing targeting of online code repositories," where threat actors are actively working to "scan for and extract secrets, access private code bases, and modify packages to infect users". This is not a theoretical risk; it is an active campaign targeting Australian organisations now.
Adversary Tactics, Techniques, and Procedures (TTPs)
The sophistication of these attacks lies in their subtlety. Instead of deploying noisy, bespoke malware that traditional security tools might detect, threat actors are employing "living-off-the-land" techniques. The ACSC notes that adversaries are "abusing legitimate tooling and functions to achieve these results". This means your security operations centre (SOC) is looking for a wolf in a field of sheepdogs; the malicious activity is deliberately cloaked in the guise of legitimate developer workflows.
Key intrusion vectors identified by the ACSC include :
Compromised Credentials & Tokens: Stolen passwords or authentication tokens provide direct access to source code repositories.
Phishing & Social Engineering: Highly targeted campaigns designed to trick developers into divulging credentials.
Infected Software Packages: The manipulation of open-source dependencies to introduce malicious code.
A prime example is the recent "Shai-Hulud" npm worm. This attack began with a targeted phishing campaign to compromise developer accounts, which was then used to inject a self-replicating worm into popular JavaScript packages. The payload was designed to steal cloud service tokens and hunt for more secrets, demonstrating the speed and scale of these automated supply chain threats.
The Critical Enabler: Secrets Sprawl
The single greatest internal vulnerability amplifying this external threat is secrets sprawl. This refers to the unintentional leakage of sensitive credentials—API keys, database passwords, cloud access tokens, and private certificates—within source code, configuration files, and CI/CD pipeline logs.
For developers working under tight deadlines, hardcoding a credential can seem like a harmless shortcut. However, once that secret is committed to a version control system like Git, it is effectively permanent and exposed. Attackers know this. One of their first post-compromise actions is to run automated scanners against repositories to harvest these exposed secrets, turning a minor code exposure into a full-blown, multi-system breach. A single exposed cloud token embedded in an application's source code can lead directly to the compromise of sensitive customer data stored in cloud buckets.
Business Impact Analysis: The Multi-Million Dollar Fallout
A compromised CI/CD pipeline is not just a technical problem; it is a business-ending event. The financial and reputational fallout from a software supply chain attack is catastrophic and multifaceted, extending far beyond the initial cleanup costs.
For Australian organisations, the average cost of a data breach has already reached $3.35 million. However, a supply chain attack acts as a threat multiplier, with unique characteristics that inflate this cost dramatically:
Regulatory Annihilation: Under the Notifiable Data Breaches (NDB) scheme, the Office of the Australian Information Commissioner (OAIC) can now impose penalties for serious or repeated privacy breaches of up to $50 million, 30% of the company's adjusted turnover, or three times the value of the benefit obtained through the misuse of information—whichever is greater. This is a monumental increase from the previous $2.22 million cap.
Operational Paralysis: When a core software component is compromised, business operations can grind to a halt. The Kaseya supply chain attack famously forced a Swedish supermarket chain to close 800 stores for days because their point-of-sale systems were rendered inoperable, showcasing how digital compromises have devastating physical-world consequences.
Ecosystem-Wide Contagion: A single compromised software vendor can infect their entire client base. The SolarWinds attack provided threat actors with backdoor access to an estimated 18,000 organisations, including government agencies and Fortune 500 companies. Your organisation's security is now only as strong as your least secure software supplier. The OAIC confirms this trend in Australia, noting a high number of multi-party breaches originating from compromised cloud and software providers.
Irrevocable Trust Erosion: When your own software is used to attack your customers, the reputational damage is profound. The cost associated with customer turnover after a breach averages over $1.5 million, and the damage to brand equity can take years to repair, if ever.
How Red Teaming Exposes This Vulnerability
Standard vulnerability scans and annual penetration tests are no longer sufficient. These methods are effective at finding known CVEs or misconfigurations in production systems, but they are fundamentally blind to the sophisticated, multi-stage TTPs used to compromise a CI/CD pipeline.
To defend against a thinking adversary, you must simulate one.
A CI/CD Red Team engagement is an objective-based adversary simulation designed to answer one critical question: Can an attacker compromise our software development lifecycle to deploy malicious code into production?
Our approach moves beyond checklists to replicate the real-world attack paths that adversaries are using against Australian companies today. We validate your defences against established industry frameworks like the OWASP Top 10 CI/CD Security Risks, providing a clear, evidence-based assessment of your true risk posture.
Key Simulation Objectives
Poisoned Pipeline Execution (PPE) (CICD-SEC-4): Can we inject malicious commands into a build script (e.g.,
Jenkinsfile, GitHub Actions workflow) that execute on a build server, giving us a foothold in your infrastructure?Dependency Chain Abuse (CICD-SEC-3): Can we trick your build process into pulling a malicious package from a public repository instead of a legitimate internal one?
Insufficient Credential Hygiene (CICD-SEC-6): Can we find hardcoded API keys, tokens, or passwords in your source code and use them to pivot to sensitive cloud environments or databases?
Inadequate Identity & Access Management (CICD-SEC-2): If we compromise a single developer's account, can we escalate privileges due to overly permissive IAM roles within your SCM or cloud platforms?
Insufficient Logging & Visibility (CICD-SEC-10): Can we perform all of the above actions without triggering a single meaningful alert from your security monitoring team?
Our Methodology: A Controlled, Objective-Driven Assessment
Our red team engagements are meticulously planned and executed to test your entire SDLC, from developer identity to production deployment.
Threat Modelling & Reconnaissance: We work with you to understand your specific CI/CD architecture, tools, and workflows. We then perform reconnaissance to identify potential developer credentials or exposed information that could serve as an initial entry point.
Initial Compromise & IAM Exploitation: We simulate targeted attacks to gain an initial foothold, then probe your IAM configuration for weaknesses that allow for privilege escalation and lateral movement across your development ecosystem.
Pipeline Infiltration & Manipulation: We attempt to exploit weaknesses in your pipeline's configuration and access controls to achieve Poisoned Pipeline Execution, seeking to gain control of the build process itself.
Secrets Exfiltration & Impact Demonstration: We actively hunt for exposed secrets. Upon discovery, we demonstrate the potential business impact by using them to access a non-production data store or cloud service in a safe, controlled manner.
Reporting & Strategic Debrief: We provide a comprehensive report detailing not just the vulnerabilities found, but the entire attack narrative. Our executive debrief focuses on providing a prioritised, actionable roadmap for remediation, addressing the root causes in your people, processes, and technology.
Secure Your Software Factory Today
The ACSC's alert is a clear warning: the software supply chain is the new frontline in cybersecurity. Waiting for a breach to occur is no longer a viable strategy, especially with regulatory penalties and reputational stakes at an all-time high. Proactive validation through realistic adversary simulation is the only way to understand and mitigate this pervasive threat.
Don't let a compromised commit unravel your entire enterprise. Contact our team of experts for a confidential consultation to discuss how a CI/CD Red Team engagement can secure your development pipeline and protect your business.

Beyond the Basics: Advanced Security Testing Techniques for 2025 Threats - Infograph
This Lean Security infographic outlines advanced testing strategies for evolving 2025 cybersecurity threats, including AI-driven vulnerability scans, realistic red team simulations, adaptive testing, cloud-specific evaluations, and the combined strengths of automated and manual security testing for comprehensive protection.
This Lean Security infographic outlines advanced testing strategies for evolving 2025 cybersecurity threats, including AI-driven vulnerability scans, realistic red team simulations, adaptive testing, cloud-specific evaluations, and the combined strengths of automated and manual security testing for comprehensive protection.
